Speed up RIOT-filtered IP exports
The IP export API now applies RIOT exclusions through bulk, concurrent lookups, allowing large filtered exports to complete faster while preserving result order and fail-open behavior.
Sep 21, 2026
Speed up RIOT-filtered IP exports
The IP export API now applies RIOT exclusions through bulk, concurrent lookups, allowing large filtered exports to complete faster while preserving result order and fail-open behavior.
Protect SSO-managed workspace memberships
The workspace API now identifies SSO-managed workspaces and rejects owner-initiated member removal with a conflict response, preventing IdP-managed membership from being changed through the API.
Sep 20, 2026
Retry blocklist builds sooner
GNQL blocklists now retry transient build failures after one minute instead of five, allowing more attempts before a cached blocklist becomes stale. The monitor also defaults a missing refresh interval, preventing startup failures from an omitted configuration value.
Sep 18, 2026
Link to externally hosted briefs
In the public Visualizer, authorized users can create threat briefs backed by an external HTTP(S) link instead of an uploaded PDF. Linked briefs open their external source from the catalog and article page.
Configure sensor address blocks
Sensors running greygent can now use an IPv4 CIDR block in public_ips instead of listing each address individually. The agent excludes network, broadcast, gateway, and configured excluded addresses before applying the resulting capture destinations.
Sep 17, 2026
Remove workspace members
Workspace contact owners can now remove a member through the public DELETE /v3/workspace/users/{user_id} API endpoint. The endpoint also removes that account's pending invite and prevents an owner from removing themselves.
Show pull-only feed activity
Pull-only feeds now record activity when events are retained, so their Event Volume chart no longer shows zero activity solely because no webhook destination is configured.
Sep 16, 2026
Complete wide callback file queries
Callback file-facet queries can now complete for wide time windows, including 90-day requests, rather than having their response cut off by the server timeout.
Explore tag activity through API
The public Tag Activity API is now documented for retrieving a tag's time-bucketed active-IP counts, with optional per-bucket IP lists. Invalid tag IDs now return a 400 response instead of failing.
Sep 15, 2026
Block unauthorized workspace queries
The public GNQL API now refuses workspace_id queries that name another customer's workspace. Scheduled alerts also reject stored workspace_id clauses so they cannot run against another workspace.
Identify IP result data sources
The public IP and GNQL APIs now return source_workspaces for results from multiple selected scopes. Sensor-only workspaces can also query their personal scope without requiring Community access.
Restore official tag filters
Official GreyNoise tags now resolve in Community and personal GNQL scopes instead of returning empty results.
Sep 14, 2026
Choose a signup path
The public Visualizer now gives signed-out visitors a /signup page where they can choose personal or business email account creation. The page lists the access included with each path and preserves a valid in-app return path through signup.
Prevent oversized entitlement cookies
The Visualizer now uses a compact entitlement cookie format to prevent requests from exceeding the load balancer header limit. Existing oversized entitlement cookies refresh automatically, avoiding the affected 400 error.
Use sensor profile overrides
Workspace-scoped sensor profile override routes are now reachable, so sensor operators can use override, diff, and seal actions without the missing workspace context causing an authorization error.
View Tactics detection chains
The public API now serves the Tactics detection chain with inbound packet-correlation evidence and egress connection observations. Tactics customers can view GreyNoise IP context and available inbound capture details alongside those chains.
Sep 11, 2026
Prevent cross-workspace tag timeline limits
The public API now sends the caller workspace with v3 tag volume timeline requests. This keeps the timeline's request limits isolated per workspace instead of allowing one workspace's traffic to affect another's.
Sep 10, 2026
Unregister sensors during unbootstrap
When you run the sensor unbootstrap script with an API key, it now unregisters that sensor from your workspace after local cleanup succeeds.
Sep 9, 2026
Create Suricata rule retrohunts
The public API now supports creating named Suricata rule retrohunts with an optional Arkime query and time range, and can estimate matching file counts before a hunt runs.
Keep long IP timeline values readable
Long, space-free values such as web paths now wrap within their column in the public Visualizer IP timeline, so they no longer overlap the activity sparkline.
Sep 8, 2026
See blocklist refresh health
Blocklist rows in the public Visualizer now show query-invalid and stale states instead of appearing healthy. The status filter includes those states, and invalid queries expose GreyNoise's rejection reason.
Clarify workspace invitation outcomes
The public Visualizer now explains expired, already-used, and unsuccessful workspace invitations on the invite-accept page. Successful invitations show a joined-workspace confirmation instead of an error state.
Sep 4, 2026
Show blocklist query errors
When a Block user saves a GNQL blocklist query that cannot run, the Block form now shows the service validation message instead of asking them to retry.
Search comma-separated IP lists
GNQL now treats a comma-separated list of IPv4 addresses, CIDRs, or IP ranges as an OR search, including lists pasted into a query.
Return newest IP exports first
The IP export API now orders matching IPs by most recently observed first, so size-limited exports return the newest matches instead of the lowest IP addresses.
Speed up Visualizer plan loading
Visualizer now runs plan and customer entitlement lookups in parallel and caps entitlements service calls at three seconds during server rendering.
Keep sessions working after workspace switches
Visualizer now keeps the selected workspace API key in place during bootstrap and workspace switches, preventing key-only routes from treating signed-in users as unauthenticated.
Sep 3, 2026
Keep silent tags out of timelines
IP classification timelines now exclude silent tags when determining an IP's daily classification. Visible tag intentions continue to determine the classification returned by the public API.
Use Turnstile for public access
The public Visualizer now uses Cloudflare Turnstile to issue a short-lived visitor pass for anonymous API access. The pass is renewed while visitors browse, with a one-hour limit from the original verification.
Sep 2, 2026
View Arkime queries in retrohunt details
The public v3 retrohunt detail API now returns arkime_queries when present, so API clients can inspect the Arkime expressions used to select PCAP files.
Callback data defaults to organic detections
Callback data now excludes research-initiated callback IPs and files by default, so its dataset, bulk downloads, and feed events reflect organic detections. Source filters remain available when you need to include those records.
Access silent tags through the API
Entitled workspaces can retrieve silent tags through the public tag list, detail, query, and timeline API endpoints. Session-volume charts now receive the same entitlement context.
Keep tag summaries visible
Tag summary responses continue to return enabled tags when the newest enabled tag cohort contains only silent tags.
Sep 1, 2026
Disable blocklists with invalid queries
Blocklist API users can now disable, rename, or adjust IP limits on a blocklist with a stored GNQL query that no longer validates, without deleting it.
Resend account verification emails
The sign-up verification screen can again resend a verification email. It now shows delivery errors and applies a 60-second cooldown after a resend request.
Workspace switches keep API access aligned
The Visualizer now stores the active workspace and its API key together, preventing requests from briefly using a key from the previously selected workspace after a switch.
Aug 27, 2026
Bound callback data in analysis reports
IP Analysis reports now limit callback activity to the workspace's configured data-reach period, matching the report's other time-bounded data.
Aug 26, 2026
Clarify alert result datasets
Alert emails and webhook payloads now identify whether results came from global or workspace-only observations. Workspace-scoped alert emails also note that Visualizer links may show different results.
Expose blocklist build status
Blocklist API responses now include derived build status and relevant successful-build and validation details, making stale or invalid blocklists visible to API consumers.
Preserve multi-IP sensor capture
Sensors configured with multiple supplied public IPv4 or IPv6 addresses now preserve capture packet-filter rules for each address after health checks, rather than reducing them to one address.
Correct Visualizer country filters
Visualizer country filters and map labels now align with indexed country values, including Kosovo, so affected country selections return matching results.
Aug 25, 2026
GNQL queries recover from replica conflicts
GNQL API reads now retry transient backend conflicts instead of returning an internal error. Requests that still cannot complete return a retryable response.
Retrohunt jobs return failure details
The v3 Retrohunt list and detail responses now include the most recent job error when a Retrohunt fails.
Aug 24, 2026
CVE pages clarify non-observable vulnerabilities
CVE pages now show a non-observable verdict to signed-out and unentitled users when GreyNoise has no remotely observable detection. These pages no longer show Scanner Activity or an upgrade prompt when those controls cannot provide additional information.
Aug 21, 2026
Clarified CVE detection coverage states
The CVE page now distinguishes CVEs with no detection coverage, no observed threat activity, and active exploitation. It also offers related vendor or product detection links when a CVE has no tag.
JA4T tags for device categories
Added visible JA4T category tags for Smart TVs, Ubiquiti gear, gaming consoles, printers, and security appliances. Removed or returned contaminated device fingerprints to silent tags after an audit found false positives from Googlebot, TCPShield, and Censys.
Aug 20, 2026
Alert owners about invalid GNQL
Alert owners now receive an email when a scheduled alert cannot run because its stored GNQL is invalid. The notice includes the alert name, query, parser error, and links to edit the alert or try the query in the Visualizer.
Daily and weekly alerts fire reliably
Fixed daily and weekly scheduled alerts skipping their configured period because of small execution-time drift. Alerts now evaluate their interval at calendar-day boundaries while preserving the configured weekly day.
Feed controls preserve delivery settings
Fixed feed enable and disable controls so status changes do not rewrite delivery configuration or unsaved form changes. Feed history now uses a bounded scroll area, and the Visualizer gives clear feedback when a pull-only feed cannot be enabled.
Search ASNs without the AS prefix
GNQL now accepts bare numeric ASN values such as `asn:29465` and resolves them to the standard AS-prefixed value. The same behavior applies across supported search translators and ASN field aliases.
Tag rankings exclude hidden tags
Fixed tag summary rankings so hidden tags no longer empty Trending and Created views or appear in Most Active results. The summary API now fetches enough candidates to filter hidden tags before returning each requested ranking.
Validate GNQL without running searches
Added the public `POST /v3/gnql/validate` endpoint to check whether a GNQL query can be parsed and translated without executing a search. GNQL now also recognizes `NOT` as an operator while continuing to support operator words as field values.
Aug 19, 2026
Bulk IP lookups use less memory
Bulk IP lookups now stream results while preserving the existing API response shape, reducing the memory required for large requests by hydrating records as they are emitted.
Translate Suricata rules for session search
The Detection & Tags API now includes POST /v2/***********, which converts supplied Suricata rules into session-search query strings and returns a diagnostic when no query can be produced.
Aug 18, 2026
Dashboard panels retain saved filters
In the public Visualizer, dashboard panels now preserve saved tag and country filters when edited. Filtered dashboard maps also show only the selected countries and use the same result depth as the Classic Visualizer.
Eight business services added to BSI
Business Service Intelligence now recognizes HubSpot, HubSpot Crawler, Zendesk, Mimecast, Adobe Marketo Engage, Salesforce Marketing Cloud, Zoho, and ADP infrastructure.
Port statistics match search counts
Port statistics and search counts now apply the same recency logic for the same GNQL query. Sampled statistics remain marked as approximate where sampling is used.
Workspace comparisons load faster
Compare tab tag and destination-country results now use the denormalized 30-day data path, reducing the slowest comparison queries from several seconds to under half a second. The results also exclude stale values outside that window.
Aug 17, 2026
Bare GNQL queries resolve predictably
Bare IP addresses, CIDRs, and boolean flags in GNQL now resolve to their intended fields. Unsupported unqualified terms return a validation error explaining that the field must be specified.
Sign-in redirects clear stale destinations
Signing out or starting a new login now clears stale return paths, and signed-out workspace invite flows show the correct invitation experience.
Switch between the Classic and New Visualizer
Authenticated users can now switch directly between the Classic and New Visualizer from the top navigation, without visiting account preferences.
Aug 15, 2026
CVE pages distinguish missing data from invalid IDs
Visualizer now labels well-formed CVEs without available data as unavailable instead of invalid, while malformed CVE identifiers retain the existing validation message.
OpenAPI correctly describes V3 IP intelligence responses
Production and staging OpenAPI specifications now describe IP intelligence tags as arrays and document the actual tag, callback IP, volume, and classification timestamp fields returned by /v3/ip and /v3/gnql.
Aug 14, 2026
Business Service Intelligence adds five network providers
Business Service Intelligence now identifies IP ranges belonging to Oracle Cloud Infrastructure, Ahrefs, Tailscale, Linode, and Vultr using provider-published range data.
Event Feed APIs return accurate validation errors
Event Feed webhook tests now preserve downstream 400 responses instead of returning 500 errors. Mailbox operations also reject unsupported session feeds with clear validation responses.
Event Feed classification filters find retained events
Event Feed classification searches now find retained IP classification-change events stored in legacy payload formats. New events also populate the canonical classification field without changing webhook payloads.
Long GNQL queries no longer fail
The public `/v3/gnql` and `/v3/gnql/stats` endpoints now accept queries up to 4096 characters instead of 1024. This fixes Visualizer-built facet queries that were valid but were being rejected on length before they could run.
Profile pages show assigned sensors
In the public Visualizer, profile details now load assigned sensors from a profile-scoped endpoint instead of filtering the first fleet page. Multi-CIDR profile assignments also include a `View Profile` link, so large workspaces no longer lose mapped sensors after the first 1000 results.
Slow GNQL searches get more time to finish
GNQL search pages now have up to 60 seconds to complete, reducing premature failures for legitimate cold-cache queries while preserving bounded concurrency.
Aug 13, 2026
CVE timelines drop duplicate prefixes
In public API tag timeline responses, CVE event titles and descriptions no longer repeat the `CVE` prefix. The fix covers first-known publication, publication, last update, and CISA KEV timeline events.
GNQL now includes workspace tags
Published workspace tags now participate in `tags_30_day`, tag volume data, and GNQL tag hydration alongside official tags. This lets GNQL-backed workspace-tag queries resolve metadata and surface matching tag data instead of omitting those tags.
Aug 12, 2026
Sign-in returns you to your requested page
The public sign-in flow now defaults the post-login return URL to the route you were trying to reach. When you land on a protected page before logging in, you are returned there after authentication instead of being sent to `/` unless the app overrides the destination.
Workspace tag pages show activity again
The existing tag activity, tag IPs, and timeline endpoints can now resolve published workspace tags instead of only official tags. In the public Visualizer, workspace tag detail pages with the `My Workspace` scope now show activity data when matching data exists.
Aug 11, 2026
Callback filter branches reject invalid keys
In the public Visualizer, callback IP, stats, and export requests now reject mis-cased or invalid OR-branch filters with a 400 response instead of silently widening results. This prevents bad filters from returning unfiltered data.
Dashboards open to your preferred view
In the public Visualizer, the Dashboards page now lets you choose which view opens first: the Daily Intelligence Dashboard or your most recently updated dashboard. The preference is stored per user and applies across workspaces.
Feed staleness checks stop timing out
Feed listing and feed statistics requests now avoid the delivery-staleness query paths that were causing slowdowns and timeouts, while preserving stale feed indicators where they are shown. The underlying delivery lookups are now scoped by workspace so production can use the intended index.
Live Suricata feeds include workspace rules
The `/v2/***********` API now returns published workspace tag rules in addition to official rules. This lets live PCAP processing apply workspace-specific Suricata detections in real time.
Aug 10, 2026
Sidebar facets build valid GNQL queries
Facet clicks in Visualizer IP search now add explicit operators and group repeated values for single-valued fields with OR. This prevents combinations such as two classifications from producing zero results and keeps query badges and operator controls consistent.
Suricata feeds load all detection rules
GreyNoise Suricata feeds now use unique signature IDs for 13 rules that were previously rejected as duplicates. Ten tags whose only rule was affected are active again in both v1 and v2 feeds.
Visualizer headers stay full width
Constrained Visualizer pages now limit only body content while keeping headers and their dividers full width. Loading and error states follow the same layout.
Aug 7, 2026
Manage Event Feed API consumers
Event Feed API users can now create, reset, and delete named consumers through the public API. Each consumer keeps its own server-held progress for a feed, and new or reset consumers start at the earliest currently retained event.
Preserve callback stage filters
In the public Visualizer, callback queries with multiple OR groups now keep stage filters such as `isStage1` and `isStage2` when request filters are serialized. This fixes incorrect results, facet counts, and CSV exports for those queries.
Aug 6, 2026
Choose your Visualizer version anytime
In Visualizer account preferences, the App Version selector is now shown for every user and saves `vizVersion` without requiring the old `feature-viz-redesign` entitlement.
Compare view prompts sensor deployment
In the public Visualizer's Observe → Compare view, workspaces without deployed sensors now see a deploy-a-sensor call to action instead of empty comparison cards. The comparison waits for the sensor check before starting and keeps the sidebar stats visible.
Verify Visualizer entitlement cookies
The public Visualizer now signs and verifies its entitlement cookie before using it for entitlement checks, and refetches entitlements rather than relying on client-supplied cookie data. Logout also clears entitlement cookies completely so stale access data does not linger in the browser.
Aug 5, 2026
Alerts list returns summary responses
The public Alerts API list endpoint now returns a summary shape instead of the full alert detail payload. List requests no longer decrypt webhook headers or compute delivery status on every row, while the detail endpoint still returns those fields.
Persona lookups return vulnerable profiles
The public Sensors API now returns persona details by ID even when the persona is marked vulnerable, unless `include_vulnerable=false` is passed explicitly. This fixes persona lookups that were incorrectly returning 404s for vulnerable profiles.
Aug 4, 2026
Toggle alerts without full updates
The public Alerts API now supports a dedicated enabled toggle endpoint, so clients can enable or disable an alert without resending its full schedule, recipients, and parameters. In the public Visualizer, opening the alert edit form now fetches the current alert details and shows a retry path if that load fails.
Webhook health is per destination
Feed webhook delivery health is now tracked per destination instead of per feed. If one destination goes stale, GreyNoise skips only that destination and continues delivering to healthy sibling destinations.
Aug 3, 2026
Tactics links redirect to Observe
Bookmarks and shared links using `/tactics` or nested tactics paths now redirect to the corresponding Observe pages instead of returning a 404 or landing on the wrong route in the public Visualizer.
YARA rules for botnets and miners
Callback file analysis now tags 15 more patterns, including DASANI GPON and FastDex droppers, XMRig config files, bot registration responses, embedded C2 endpoints, and updated Mirai and Mozi ELF coverage.
Jul 31, 2026
Alerts survive broken webhook headers
Alert reads and updates no longer fail when one webhook recipient has undecryptable headers. GreyNoise now returns the rest of the alert normally and leaves the broken recipient with empty headers instead of 500ing the whole alert.
Bulk IP lookups support HTTP QUERY
The public multi-IP lookup endpoint now accepts the HTTP QUERY method with a request body while returning the same results as POST. Browser clients can use the method through the updated CORS policy.
Create Event API feeds without webhooks
Entitled workspaces can now create non-session feeds in the public Visualizer without adding a webhook URL. Events remain available through the Event Feed API, while session feeds still require webhook delivery.
Event Feed search finds standardized spikes
Exact Event Feed API searches now find retained spike events that store tag and CVE data in the standardized criterion fields. Existing retained events that still use the older top-level payload fields continue to match too.
New public Threat Map is live
The redesigned Threat Map is now live at threat-map.greynoise.io. It shows current attack activity on a 3D globe or 2D world map with intention colors, country details, and a live activity counter.
Sensor names mask embedded IP addresses
When IP redaction is enabled, sensor names in the public Visualizer now mask any embedded IPv4 or IPv6 addresses instead of showing them raw. The descriptive parts of each name stay visible across sensor, session, profile, PCAP, and tactics views.
Jul 30, 2026
30-day GNQL queries stop timing out
Default 30-day GNQL queries that filter on windowed scalar fields now read precomputed rollups instead of per-IP daily aggregates. Queries such as sensor-count filters stay on the same search path but return with much lower latency and avoid the timeout this fix targeted.
Sensor deployment keys finish bootstrap
Deployment-key auth now works across the remaining public sensor lifecycle routes, including sensor create, update, delete, and bootstrap or unbootstrap scripts. Sensor agent health posts and sensor agent package downloads now authorize against the workspace tied to the key instead of failing with 401 or 403 responses.
Jul 29, 2026
Alert notifications show executed query
Alert runs now record the query they actually executed, and alert emails, webhooks, and run details include that executed query and its anchored lookback window. The Visualizer link in an alert notification now reproduces the alert's result set more reliably after the fact.
Profiles flag vulnerability and page commands
Profile cards and profile detail pages now show whether a profile is marked vulnerable. Session detail responses also page command timelines in 500-command chunks and return total-count and pagination metadata instead of always sending the full command history.
Tactics detections add network and files tabs
Visualizer tactics detection pages now split Commands, Network, and Files into separate tabs. The Network tab lists related destination IPs with links into Session Explorer, and the Files tab lists mutated files with per-file downloads when artifact-content access is enabled.
Jul 28, 2026
BSI defaults to local calendar day
On the public Visualizer's BSI page, the date picker now defaults to your local calendar day instead of UTC. This avoids landing on an empty future partition for users behind UTC.
Workspace deployment keys for sensors
Workspace admins can now create, list, and revoke deployment keys through the console. Those keys can authenticate the sensor bootstrap and sensor agent routes that opt in to deployment-key access.
Jul 27, 2026
Alerts list recipientless alerts reliably
Alerting pages and API responses now handle alerts with no recipients without failing. Recipientless alerts return `recipients: []`, so one empty-recipient alert no longer hides the rest of a workspace's alerts.
Jul 24, 2026
Alert webhooks accept all 2xx
Alert webhook deliveries now treat any HTTP 2xx response as successful instead of requiring an exact 200. This keeps valid 201 and 204 webhook endpoints from being marked as failed or going stale.
Callback IP pages stop flashing errors
On the public Visualizer IP page, callback-only IPs now keep the loader visible until callback data finishes loading. That prevents the brief "Further investigation recommended" error flash before the callback view appears.
Technique-linked command timelines on detections
Detection detail pages in the Visualizer now show a per-command timeline when command event data is available. You can filter the timeline by technique to see which commands triggered a detection, with timestamps and linked IPs kept inline.
Jul 23, 2026
Complex GNQL searches return faster
The GNQL count and search path now chooses a lower-cost query shape for certain complex child-dimension searches. This reduces latency for those searches without changing the query syntax.
GNQL filters child values by recency
GNQL now supports companion `.last_seen` filters for child-table dimensions. This lets you target child values that were seen within a specific recency window.
PG search counts can be capped
The public `/api/v1/***********` count and search endpoints now accept a `max_count` parameter. It caps the reported total while still returning the requested result page, which helps broad searches return an "at least N" count without scanning the full match set.
Query errors distinguish throttling and timeouts
In GreyNoise Visualizer, the query page now shows dedicated messages when a valid search is throttled or times out. This replaces cases where those responses were surfaced as a syntax error.
Query viz handles throttles and timeouts
The public Query experience in Visualizer now shows specific messages when a search is temporarily throttled or times out, instead of treating those responses as a query syntax error. Timeout and throttle states also avoid suggesting more searches while the request can't be completed.
Session charts show multi-day dates
In GreyNoise Visualizer's Session Explorer, time-series charts now show date labels for multi-day ranges instead of time-only labels. The chart formatting now adjusts to the selected span so longer ranges stay readable.
Shared API links enforce scoped access
Shared-link access on the public GN API enforces scoped read permissions and revocation checks for supported routes, so API consumers using share-link tokens get exactly the access the link was issued with.
Jul 22, 2026
Bulk IP lookups support multiple workspaces
The bulk IP lookup endpoint now supports querying across multiple workspaces on the public API. Results are merged into one record per IP so bulk lookups can return combined tags, ports, and classifications across the selected workspace set.
Jul 21, 2026
IP timelines use lifetime first seen
IP timelines now use a dedicated lifetime first-seen lookup instead of relying on a shorter loaded window. This makes the first-seen date on timeline views and related API responses stay accurate for IPs first observed longer ago.
GNQL supports date ranges
GNQL queries now support date comparison operators like `>=`, `>`, `<=`, and `<` on date fields such as `last_seen` and `first_seen`. This lets you express bounded date windows directly in GNQL with absolute dates, relative dates, and `today` or `yesterday`.
Resolved GNQL queries rerun cleanly
Adjusted GNQL queries returned by the public API now stay valid GNQL when you resubmit them. That fixes cases where the resolved query included engine-specific syntax that broke reruns on the primary search path.
Tag activity honors custom ranges
In GreyNoise Visualizer, tag and CVE activity charts now honor the exact entitled day range instead of being limited to preset windows. The legacy tag activity and volume-timeline proxies also now accept positive whole-day ranges and keep the chart labels aligned with the selected window.
Workspace Compare moved to Search
GreyNoise Visualizer's query page now includes a Compare view for comparing the same GNQL query across workspaces. The view adds comparison stats in the sidebar, unique-IP and unique-value comparison cards, and redirects the legacy compare page into the query flow.
Jul 20, 2026
API single-IP lookups use IP detail
Public single-IP lookup endpoints now use the dedicated IP detail path instead of running point lookups through the broader search flow. This gives those lookups the fuller single-IP record and keeps timeline lookups on the detail path as well.
Dashboard selection and GNQL sync
In the Visualizer dashboard drawer, switching dashboards now shows immediate selection feedback instead of waiting silently for the load to finish. Geo Map country dropdowns also now read from and write to the underlying GNQL query so saved filters and the query stay in sync.
Search results on collection layout
GreyNoise Visualizer's `/query/:gnql` page now uses the shared collection layout with a facet sidebar, list and card views, more IP fields, and export and automate actions. Inline search suggestions on that page also now filter correctly while you type.
Jul 17, 2026
Dashboard time range adapts to your data access
The Visualizer dashboard time-range selector now disables the "Past 10 days" option for accounts whose plan does not include that much history, showing the available limit (or, for consumer-email accounts, a note that a business email unlocks more data). A dashboard set to a range the account can no longer access falls back to "Past 24 hours" automatically.
Broader sensor IP masking in the Visualizer
Sensor IP and CIDR masking in the Visualizer now covers more surfaces: multi-CIDR sensor profile assignments and the profile target/carve builder are masked by default with a reveal control, and sensor IPs are masked in the Session Explorer packet hex and ASCII dump. Masked values keep their shape and the underlying selection behavior is unchanged.
Full MITRE ATT&CK tactic lifecycle in the Visualizer
The Visualizer's Tactics sidebar now lists all 14 MITRE ATT&CK enterprise tactics in lifecycle order — adding Reconnaissance and Resource Development — each filterable like the rest. A tooltip explains why the leading stages (Reconnaissance, Resource Development, and Initial Access) currently read zero: GreyNoise observes only post-compromise host activity.
Jul 16, 2026
Stay signed in to the Visualizer across restarts
The Visualizer now keeps you signed in across browser and computer restarts: the session cookie is set to persist (about a year) instead of expiring when the browser closes. Unusually large sessions that previously exceeded the browser's per-cookie size limit — and were silently dropped, appearing as a logout — are now split across multiple cookies and reassembled automatically.
Jul 15, 2026
ASN subnet in IP data, GNQL, and Timeline
Entitled workspaces (feature-ip-asn-subnet) can now see an IP's latest observed ASN subnet in IP metadata and query it in GNQL via asn_subnet / metadata.asn_subnet, with the value included in CSV exports and field autocomplete. The daily IP Timeline adds an ASN subnet history section listing each distinct subnet observed per day (up to 90 days), across the public API and the Visualizer.
GNQL auto-routes bare CVE, ASN, and tag terms
A raw CVE ID, ASN, or tag name typed into GNQL search now auto-expands to the matching field — for example CVE-2025-55182 to cve:CVE-2025-55182, AS16509 to metadata.asn:AS16509, and mirai to tags:"Mirai" — so the term routes to the correct lookup instead of a broad, often-empty generic search. Matching is case-insensitive and supports quoted and wildcard forms.
Build dashboard panels from GNQL queries
Visualizer dashboards can now use a saved GNQL query as the source for Key Numbers, Activity Map, and Activity Trend panels. Queries are validated before saving, and activity-trend charts appear when the workspace has access to the required time-series data.
GNQL supports Lucene field grouping
GNQL now accepts Lucene field-grouping syntax — field:(a OR b) — applying one field to every value inside the parentheses, so you can write metadata.asn:("AS16509" OR "AS7224") instead of repeating the field. It works for any value type (strings, numbers, IPs, and IP ranges) and composes with AND, OR, and negation.
Fix GNQL searches that failed on free-text terms
Several valid GNQL queries that returned an error — including single-word searches like switzerland, multi-word terms, and queries excluding long lists of ASNs — now run correctly. Free-text terms are no longer matched against date fields (which caused date-parse failures), and a multi-word value is no longer swallowed into an adjacent typed field.
Faster tag-name searches in GNQL
A GNQL tags:"..." search whose name matched no tag could take 16–60 seconds (and occasionally time out); these now return instantly. Tag-name filters are pre-resolved so the query planner can fold an unmatched name to an immediate empty result.
Prevent SSH lockout when unbootstrapping a sensor
Running the sensor unbootstrap script no longer risks locking the operator out of the box over SSH. The script now stops the conflicting SSH unit before restarting and verifies sshd is listening on port 22 before ending the current session, leaving the connection open with a warning if recovery does not succeed.
Fix repeated Visualizer logouts
Visualizer users who were being signed out multiple times a day are no longer logged out by refresh-token rotation races. The auth layer now de-duplicates concurrent token refreshes into a single exchange and retries once when a concurrent refresh has already rotated the session, instead of clearing it.
Jul 14, 2026
Control per-IP child data in API lookups
The API's IP lookups (/v3/ip), GNQL search (/v3/gnql), and /v3/gnql/metadata now accept an optional max_children_per_ip parameter (1-10000) that caps how many child records are returned per IP. By default, single-IP lookups return up to 10,000 child records while bulk and search results return up to 100.
Jul 13, 2026
New AI infrastructure scanner tags
Added a ComfyUI /system_stats scanner tag and expanded the Ollama API endpoint crawler tag to also cover the /api/tags endpoint.
RSS feeds for Threat Briefs
The public API now serves Threat Briefs as RSS feeds: an open community feed at GET /v3/articles/rss, plus authenticated per-workspace feeds whose contents follow the workspace's live article entitlements. Retrieve or rotate a workspace's feed URL via the GET/POST /v3/articles/rss-token endpoints.
New GNQL IP export and count API endpoints
The API adds GET /v3/gnql/count and GET /v3/gnql/ips, letting you count and export every IP matching a GNQL query as JSON. The IP export accepts an optional exclude_riot parameter to omit RIOT (known-benign business service) IPs from results.
Redact sensor and destination IPs in the Visualizer
Sensor and destination IPs across the Visualizer's session explorer, sensors, and profiles views are now masked by default and revealed on click, controlled by a new "Redact sensitive data" account preference. Workspaces without the sensors entitlement are always redacted.
Jul 10, 2026
Resolved query restored on the GNQL search path
The Query page's "Show Resolved Query" view now works consistently across GNQL search paths: searches return the expanded query (for example, a relative time like last_seen:1d resolved to a date) along with the query-adjusted flag and any restricted-field message.
Jul 9, 2026
AWS VM Import guidance on OVA profile creation
When creating a sensor Profile from an OVA, the Visualizer now shows an info note linking to the AWS VM Import documentation on the upload form, and the failure alert links to the same docs — an actionable next step when an OVA uses an unsupported operating system or image configuration.
Daily dashboard pinned in the selector
The default daily intelligence dashboard now stays pinned at the top of the dashboard selector with a clear "Daily Intelligence Dashboard" name and the same active styling as saved dashboards, making it easy to return to.
Dashboard map and activity drilldowns
The Visualizer intelligence dashboard adds graph views to the CVE and Tag detail cards, lets you widen the map from its three-dot menu, and opens new dashboards on the past-10-days view. Clicking a point on a tag or CVE activity chart now reveals the IPs seen that day.
New variant rule for Redis Lua sandbox escape
Added a Suricata rule variant to the Debian Redis Lua sandbox escape tag (CVE-2022-0543) to flag exploitation attempts that load liblua and luaopen_io, extending coverage beyond the existing signature.
Jul 8, 2026
NETLINK_GPON_RCE tag now catches Mozi variant
Added a raw-TCP Suricata rule to the NETLINK_GPON_RCE tag so it flags a Mozi botnet variant that injects commands against Netlink/RealTek GPON routers via malformed request lines and the formLogin endpoint — traffic the existing formPing-anchored rules did not match.
Jun 24, 2026
Download precomputed Psychic snapshots via API
A new POST /v1/psychic/snapshots endpoint streams precomputed Psychic snapshot artifacts — 7- or 30-day rolling windows for models 1-3 and the latest model 4 snapshot — in binary or MMDB format. Requires the Psychic feature entitlement.
Jun 23, 2026
Credential-observed event type for Feeds API
The Feeds API now supports the credential-observed event type. Entitled workspaces can create and update feeds for credential-observed events, with the credential criteria filter validated on create/update and the public webhook payload documented in the Feeds OpenAPI spec.
Session Explorer understands vendor tag searches
Natural-language Session Explorer queries now resolve multi-word vendor names to the correct tag filter — for example "Show me IPs targeting palo alto" maps to gnTagMetadata.name:Palo\ Alto* instead of a broken wildcard, matching the GNQL translator's behavior.
Jun 18, 2026
CVE search routes to GNQL results on Enter
Pressing Enter on a bare CVE identifier (e.g. CVE-2021-3129) in the Visualizer search bar now routes to GNQL results in the current dataset scope, matching what happens when you click a suggestion. Previously, pressing Enter silently switched the scope chip to CVEs and redirected to the CVE detail page instead.
Jun 17, 2026
Callback IP graph fixed for business-service-only layers
Fixes 500 errors on the /v1/callback/*********** endpoint when a traversal layer contained only known-business-service IPs. The graph now returns data from all completed layers instead of failing with an error.
Country filters added to dashboard map panels
Dashboard geo map panels now include country pickers for source and destination countries. You can select one or more countries in the panel editor to filter the map view without changing the underlying query.
Dataset scope selector visible to all Visualizer users
The Community and My Workspace dataset scope selector now appears on every Visualizer page regardless of Swarm sensor status. Users without the community dataset entitlement see the options greyed out with a tooltip explaining that deploying a Swarm sensor grants access within 6 hours.
Multi-IP sensor bootstrap capture fix
Sensors bootstrapped with multiple manually-specified public IP addresses now capture traffic destined to each of those addresses. Unbootstrapping a sensor also restores its original configuration more reliably.
Jun 15, 2026
CVE activity chart now defaults to 30-day view
The activity chart on CVE detail pages in the Visualizer now defaults to a 30-day window instead of 24 hours, matching the page summary which already reported in-the-wild activity over 30 days. The default is capped at your data reach entitlement; the ?days= URL parameter still overrides it.
Jun 12, 2026
The Visualizer now includes a Tactics section (/observe/tactics) showing adversary tactics and techniques detected by sensors in your workspace, organized by MITRE ATT&CK tactic and searchable by technique name or IP. List and detail views are available to accounts with the feature-tactics entitlement.
New tags for Check Point VPN, llama.cpp, and WordPress CVEs
GreyNoise now tags IPs probing for CVE-2026-50751 (Check Point Remote Access VPN IKEv1 authentication bypass) and CVE-2026-34159 (llama.cpp unsafe deserialization RCE). Detection for the Burst Statistics WordPress plugin authentication bypass (CVE-2026-8181) was added and the LeRobot deserialization RCE rule (CVE-2026-25874) was updated.
Jun 11, 2026
Intelligence Dashboard opens with live trending panels
The Visualizer intelligence dashboard now shows a pre-seeded starter view on first open — populated with the current trending tag, activity timeline, map, and CVE panel — instead of an empty canvas. The starter is temporary and not saved unless you choose to save it. Available to accounts with the intelligence dashboard entitlement.
Tactics API routes now require the Tactics entitlement
The tactics list and detail routes (POST and GET /v3/workspaces/:workspace_id/tactics) now require the feature-tactics entitlement. Workspaces previously reaching these routes via feature-swarm alone will now receive 403 responses.
Tag volume chart fixes for multi-workspace and filter reload
Two fixes for the tag volume timeline chart: multi-workspace views now show the correct combined data, and switching workspace filters triggers a reload with a loading indicator rather than briefly showing stale data.
Tag pages now show a scan-volume timeline chart
Tag detail pages in the Visualizer now include an activity chart showing how scan volume for that tag has changed over time. Available to accounts with the tag volume timeline entitlement.
Natural language GNQL now handles tag-based queries
The natural language GNQL translator now understands tag-targeting requests, producing queries like tags:"VendorName*" for questions about specific vendor scanning activity. Wildcard matching is used when the exact tag name is ambiguous.
Jun 10, 2026
New tags for UniFi OS exploit chain (CVE-2026-34908/09/10)
GreyNoise now tags IPs observed scanning for the three-CVE UniFi OS exploit chain: CVE-2026-34908 and CVE-2026-34909 (authentication bypass and path traversal) and CVE-2026-34910 (command injection RCE). All three are being actively chained for unauthenticated root access on UniFi OS devices and seen in Mirai botnet activity.
Customizable intelligence dashboards in the Visualizer
The Visualizer now includes an intelligence dashboard page where you can build, arrange, and save panels — country heat maps, time series, tag intelligence, treemaps, and more — into a named workspace view. Available to accounts with the intelligence dashboard entitlement.
Jun 9, 2026
Natural language queries in Session Explorer
The Session Explorer search box in the Visualizer now suggests a generated query when you type a natural language description. Clicking the suggestion populates the search with the corresponding Explorer query syntax. Requires the natural-language-search entitlement (feature-natural-language-search).
Natural language GNQL now recognizes JA4 fingerprint fields
The natural language GNQL translator now understands the five searchable JA4 fields, producing accurate GNQL output for queries about JA4 TLS, SSH, and HTTP fingerprints.
Jun 8, 2026
A new page at /cves/recent lists recent CVEs that GreyNoise has scan data for, sorted by publication date, with a matching public endpoint at GET /v3/cves/*** for sortable, filterable results. Previously there was no way to discover CVEs through the API without supplying a list of IDs. The CVE menu in the navigation now links directly to this page.
Attack chains show a truncation notice and a load-all option
When the backend truncates a Callback IP's attack chain graph, a warning banner now appears. A "Load all chains" button re-fetches with a 5,000-node limit (versus the default 500).
Lookups consider a wider data-freshness window
Business Service Intelligence lookups now include records from the last 48 hours, up from the previous 8-hour restriction.
Callback IPs filter by multiple trust levels at once
The Business Service Intelligence trust-level filter on the Callback IPs page is now multi-select: several trust levels can be combined in one search, and the backing API accepts a riot_trust_levels list parameter.
GNQL result counts now reflect the true total
/v3/gnql and /v3/gnql/metadata were returning request_metadata.count: 10000 for any query matching more than 10,000 IPs, regardless of the actual total. The fix restores accurate counts.
Type plain English to generate a GNQL query
The search modal now accepts natural-language input and returns an equivalent GNQL query. The same translation is also available programmatically through the API.
New GET /v3/openapi.yaml endpoint serves the full API spec
A new endpoint returns GreyNoise's OpenAPI specification in machine-readable YAML, making it straightforward to generate client libraries, import into API tools, or run automated validation.
"Create Free Account" now lands on the signup screen
Clicking "Create Free Account" was routing users to the login screen rather than the signup screen. The sign-up flow now correctly opens the account-creation screen.
Selected v2 API endpoints return 410 Gone
The /v2/noise/*, /v2/riot/:ip, /v2/meta/*, and /v2/experimental/gnql endpoint families now return 410 Gone with a clear deprecation response. Equivalent functionality is available on /v3 routes.
Apr 30, 2026
Broken sensor-management doc links fixed in the Visualizer
Visualizer: dead `sensor-administration-guide` doc link updated to `sensor-management` on the Sensor List page and QueryErrors
PCAP export now streams to disk and respects the mode parameter
Sessions: PCAP export `mode` parameter now reaches the handler and the download streams via the native browser path instead of buffering into memory
Per-workspace active-sensor stats and alphabetical profile lists
Sensor service: new workspace endpoint aggregates active-sensor stats per workspace, and the profile list endpoint now supports sort-by-name (drives Visualizer alphabetical-by-default profile lists)
Profile protocol filter keeps its full option list while filtering
Visualizer: profile-page protocol-filter dropdown now derives from a separate `/protocols` endpoint so the full unfiltered list survives filtering
Session-explorer autocomplete no longer recomputes on every keystroke
Visualizer: session-explorer autocomplete no longer recomputes the field list on every keystroke
Apr 29, 2026
Callback pipeline now follows multi-stage payload downloads
Callback Pipeline: recursive download support — URLs detected in callback files re-enter the pipeline so the system follows multi-stage payload delivery
Same-week CVE/KEV coverage wave
Detection content: same-week CVE/KEV coverage wave — Langflow KEV (CVE-2026-33017), Cisco ASA/FTD auth-bypass (CVE-2025-20362), Cisco Catalyst SD-WAN Manager (CVE-2026-20129), Advanced Custom Fields RCE (CVE-2025-13486), Fortinet FortiClient EMS KEV (CVE-2026-35616), Tenda A15 buffer-overflow (CVE-2026-4567), Trivy supply-chain KEV (CVE-2026-33634), Marimo Terminal WebSocket RCE (CVE-2026-39987), NGINX UI auth-bypass (CVE-2026-33032), cPanel/WHM zero-day (CVE-2026-41940, CVSS 9.8), plus a vulncheck bulk push of 74+ rules.
Filter callback IPs that match all selected threats
Callback IP: multi-threat AND filtering — an IP must match all selected threat names, with multi-select in the Top Threats sidebar
Sensor-deploy provider labels no longer mislabel compute technologies
Visualizer: sensor-deploy provider labels normalized — "AWS EC2" no longer mislabeled as a provider when it's a compute technology
Ubuntu 26.04 now supported for sensor bootstrap
Sensor bootstrap: Ubuntu 26.04 added to the supported-OS allow-list
workspace_labels parameter now documented on v3 endpoints
OpenAPI: `workspace_labels` query parameter documented on relevant v3 endpoints
Apr 27, 2026
Analysis and GNQL JSON exports no longer produce broken files
Visualizer: Analysis and GNQL JSON exports fixed — no longer produce `"[object Object]"` files (client-side auto-parsing override)
Bare CVE searches now open the CVE detail page
Visualizer: search modal now routes bare CVEs (e.g. `CVE-2025-22952`) to the CVE detail page instead of misrouting through GNQL with a misleading "Destination country not currently supported" page
Default-profile sensors now prompt you to set a profile
Visualizer: Change Profile button made more prominent on sensor pages when profile is set to `Default`, with a persistent alert until the user changes it
RIOT Trust Level 3 marks IPs to neither block nor whitelist
Callback IP: RIOT Trust Level 3 — "never whitelist, but also don't block" — threaded through RIOT, the callback service, and the Visualizer (neutral L3 badges and labelling)
Sensor count now shown on the Sensors list and profile cards
Visualizer: sensor count surfaced on the Sensors list page and on the profile sensor card
Session fields endpoint now returns HTTP protocol groups in prod
Sessions: `/fields` endpoint now returns HTTP protocol groups on prod (field intersection fix)
Share links now available across Explore views
Share links are now available across Explore, Explore Graph, Explore Multi, and Session Explorer, with the share button moved into the app header. Shared views stay locked to the query they were issued with, so a recipient sees exactly what was shared.
Apr 24, 2026
New Yara rules for Mirai, Rondo, Beholder, and Linux persistence
VT Processor: Yara detection wave — new rules for Mirai XPL6, Rondo, Vequals, Beholder probe frames, and a range of Linux persistence and beacon patterns; plus benign-file rules and Yara diagnostics support
Apr 23, 2026
Host-artifact files split from callback files to clarify trends
Callback Pipeline: host-artifact files are now split from callback-capture files in callback queries so host-artifact volume doesn't bury actual callback trends; file-source field added to callback file data
Wildcard session queries with escaped spaces no longer split
Sessions: wildcard queries with escaped spaces (e.g. `profile.name:*My\ Profile\ *`) no longer split by the Lucene query formatter
Apr 17, 2026
The Callback page that launched in March gains a full investigation surface in April. Attack Chain cards let analysts trace malware and C2 sequences inline; IP detail sidebars surface full enrichment metadata (geo, ASN, RDNS, first/last seen); RIOT trust-level badges distinguish benign infrastructure from real C2; and the callback API adopts the platform's standard observed_by workspace scope. Callback IPs can now be investigated and triaged the same way as scanner IPs.
New entitled capability surfacing tag-volume counts — how many sessions each tag accounts for on a given IP — inside the GNQL Summary section of IP results. Lets analysts see at a glance how prevalent each tag is relative to the IP's total activity.
Profile tiers narrowed to private and greynoise
Visualizer: deprecated `community`, `basic`, and `premium` profile tiers removed, leaving only `private` and `greynoise`
The bot field is retired from GNQL queries
GNQL: `bot` field removed across schemas, query mappings, timeseries defaults, translators, ingest, type cards, similarity map, and OAS — `bot:true` queries now return a polite `DiscontinuedFieldError` with a clear explanation
Apr 16, 2026
Filter callback IPs by threat name
Callback IP: `threat_name` filter — searchable facet in the Callback search bar with ILIKE substring matching and negation; sidebar "Top Threats" entries become clickable filters
Apr 15, 2026
Community-workspace data no longer dropped from IP timelines
IP Timelines API: community-workspace data no longer dropped on multi-workspace requests like `workspace_labels=personal,community,greynoise` when the opted-out workspace list is empty
GNQL Stats endpoint now documented in OpenAPI
GNQL Stats: `/v3/gnql/stats` documented in staging and production OpenAPI specs, including query/count params and 200/206 (plan-adjusted) responses
Apr 14, 2026
Bulk file analysis surfaces callback IPs
Bulk File Analysis: callback data integration in Visualizer — submitted IPs now surface callback IPs with proper labels and a "Callback Unconfirmed" badge for callback-flagged but stage-unconfirmed IPs
Callback last-seen now reflects only successful downloads
Callback Pipeline: file download vs. last-seen separation — "last seen" now reflects only successful downloads, not URL transmission attempts; whole-day-timestamp tiebreaker added
Exclude facets from callback search with negation syntax
Callback IP: negation syntax (`-facet:value`) in the search parser, with negated-field support in the callback query API — users can now exclude countries, BSI levels, or other facets from results
GNQL result totals now always match classification counts
Visualizer: GNQL results display total now derives from the stats count so it always aligns with classification and spoofable totals
Toggling workspace scope no longer fires redundant requests
Callback IP: 1-second debounce on the multi-workspace data-scope selector on Callback, IP details, and Explore pages so quickly toggling multiple options doesn't fire N requests
Apr 10, 2026
Callback searches now survive refresh and link sharing
Callback IP: search query persisted as a `?q=` URL param so searches survive refresh, back-navigation, and link sharing; workspace scope preserved in URL state
Compare-page unique IPs list now loads correctly
Visualizer: Compare-page "unique IPs" list now requests data scoped to personal workspace so data actually loads when clicked
Workspace invites now retrieve correctly when logged in
Visualizer: workspace-invite retrieval fixed when logged in, with clearer email-mismatch language
Apr 9, 2026
Swarm's customer-facing observability surface goes GA with a new Observe tab in the Visualizer header. Live Preview defaults on for workspaces without sensors so newcomers see real data immediately. The customer-facing front door for everything the March Swarm launch was building toward.
API /ping now returns your plan and add-on modules
API `/ping`: now returns the customer's plan and modules (add-ons) alongside the legacy `offering` field, with a 4hr-TTL cache
BSI badge now shows on callback IP cards
Callback IP: BSI badge surfaced on IP cards in callback data, matching IP details and GNQL results views
Retired VPN and bot fields removed from callback pipeline
Callback IP: `is_vpn`, `vpn_service`, and `is_bot` fields removed from the pipeline — dead inputs (the third-party VPN feed was retired and the bot signal had zero invocations); `is_tor` retained
Sensor details page shows initializing-sensor status banners
Visualizer: initializing-sensor status banners on the sensor details page, with the "Missing Health Monitoring Agent" alert hidden during initialization
Apr 8, 2026
GNQL no-results page now guides you by workspace scope
Visualizer: GNQL no-results page now uses workspace-aware copy based on selected dataset scopes — "my workspace" with no sensors links directly to the Sensors page
Query callback IPs and use the yesterday keyword in GNQL
GNQL: `yesterday` keyword for time-based inputs (e.g. `last_seen:yesterday`) across every supported query translator; `callback_ips` (and `callback_ip` alias) registered as a queryable field end-to-end
Sensor bootstrap now supports Debian 13
Sensor bootstrap: Debian 13 added as a supported OS, including needrestart configuration
Apr 7, 2026
Callback endpoint docs promoted to production OpenAPI
OpenAPI: callback endpoint docs promoted from staging to production
Clearer description of the C2 Suspected classification signals
Callback IP: Stage 2 "C2 Suspected" description updated to clarify which behavioral signals weight into the classification (VT detections, sandbox network activity, malware associations)
Apr 6, 2026
Blocklist endpoints now validate GNQL syntax before saving
GNQL: blocklist create/update endpoints validate GNQL syntax before storing (400 if malformed); the Block UI's "Save as New" and "Save Changes" actions gated by query validity
GNQL gives clearer typing and type-mismatch errors
GNQL: type/error messages improved — invalid field names are now typing errors (not syntax errors), with better type-mismatch messages
Apr 3, 2026
Article PDF generation shows a dismissible alert
Visualizer: Article PDF generation alert added with session-level dismissal
Articles catalog moved out of the workspace section
Visualizer: Articles Catalog and View moved out of the workspace section of the app (manage section remains in workspace)
Articles endpoints added to production OpenAPI
OpenAPI: Articles endpoints added to production OAS (non-moderate fields only)
Create Suricata rules from HTTP requests and PCAP files again
Workspace Tag Service: Suricata rule creator reintroduced — customers can again create Suricata rules from HTTP requests and PCAP files, wired into Visualizer
RIOT data refresh expands business-service IP coverage
RIOT data refresh wave: IP-range updates across Ahrefs, Censys, GPTBot, CISA, Stanford, CoreWeave, and others; a new scraper for large CSV feeds; Strongswan IKEv2 custom rule (CVE-2026-25075)
Apr 2, 2026
Callback IP file columns now populate correctly
Callback Pipeline: `first_seen`, `last_seen`, and `file_name` columns now populated on callback file records; a `workspace_id` → `workspace_ids` field-name mismatch fixed in the callback query template
Create, exchange, and revoke share links via the API
ShareLinks API: `POST/GET/DELETE /v3/***********` endpoints — create (JWT, workspace-scoped), exchange slug for JWT (anonymous), revoke with workspace-boundary check, and list with status/click-count/creator — backend foundation for the March ShareLinks feature
GNQL syntax errors now report all issues with position hints
GNQL: parser now collects all syntax errors in a query instead of stopping at the first; structured `SyntaxError` types include human-friendly messages, positions, and context hints; Visualizer renders position markers on the failed query
Queries beyond your data reach now clamp instead of failing
GNQL Stats: redundant data-reach parsing removed so queries that exceed the user's data reach (e.g. `last_seen:91d` with a 90-day limit) now clamp instead of failing parse
Apr 1, 2026
Callback IP detail view now adapts to mobile and desktop
Callback IP: Attack Stage and Scanner IPs sections of the IP detail view made responsive (inline on mobile, sidebar on desktop); scanner+callback IP tooltip corrected when an IP is both
Callback time filters now respect your data reach entitlement
Data Reach: `feature-data-reach` entitlement now enforced on `last_seen_after` filters across the callback list, export, and overview endpoints; Visualizer hides callback time presets that exceed the user's entitlement
Mar 31, 2026
Customers can now generate a short link to any Visualizer view — IP detail, GNQL query, Sessions, and more — and share it inside or outside their workspace. A Share Link Management UI tracks, revokes, and shows click activity for every link a workspace has issued. The first publish-and-share loop in the product.
Block now surfaces the correct sensor identity
Block: `sensor_name` now threads through the API correctly so Block surfaces the right sensor identity
Host-activity detections filter out vanilla OS noise
Vanilla-OS-noise rules filtered out of the host-activity ruleset so detections focus on real signals
Manage view added to the Articles surface
Articles: Manage view option added to the article surface in Visualizer
Mar 30, 2026
Protoss Siren tag now catches in-the-wild variants
Detection content: Protoss Siren tag updated to catch in-the-wild mutations, then generalized to catch additional variants
Set a custom sensor name at deploy time
Sensor service: customers can now set a custom name on a sensor at deploy time
Mar 27, 2026
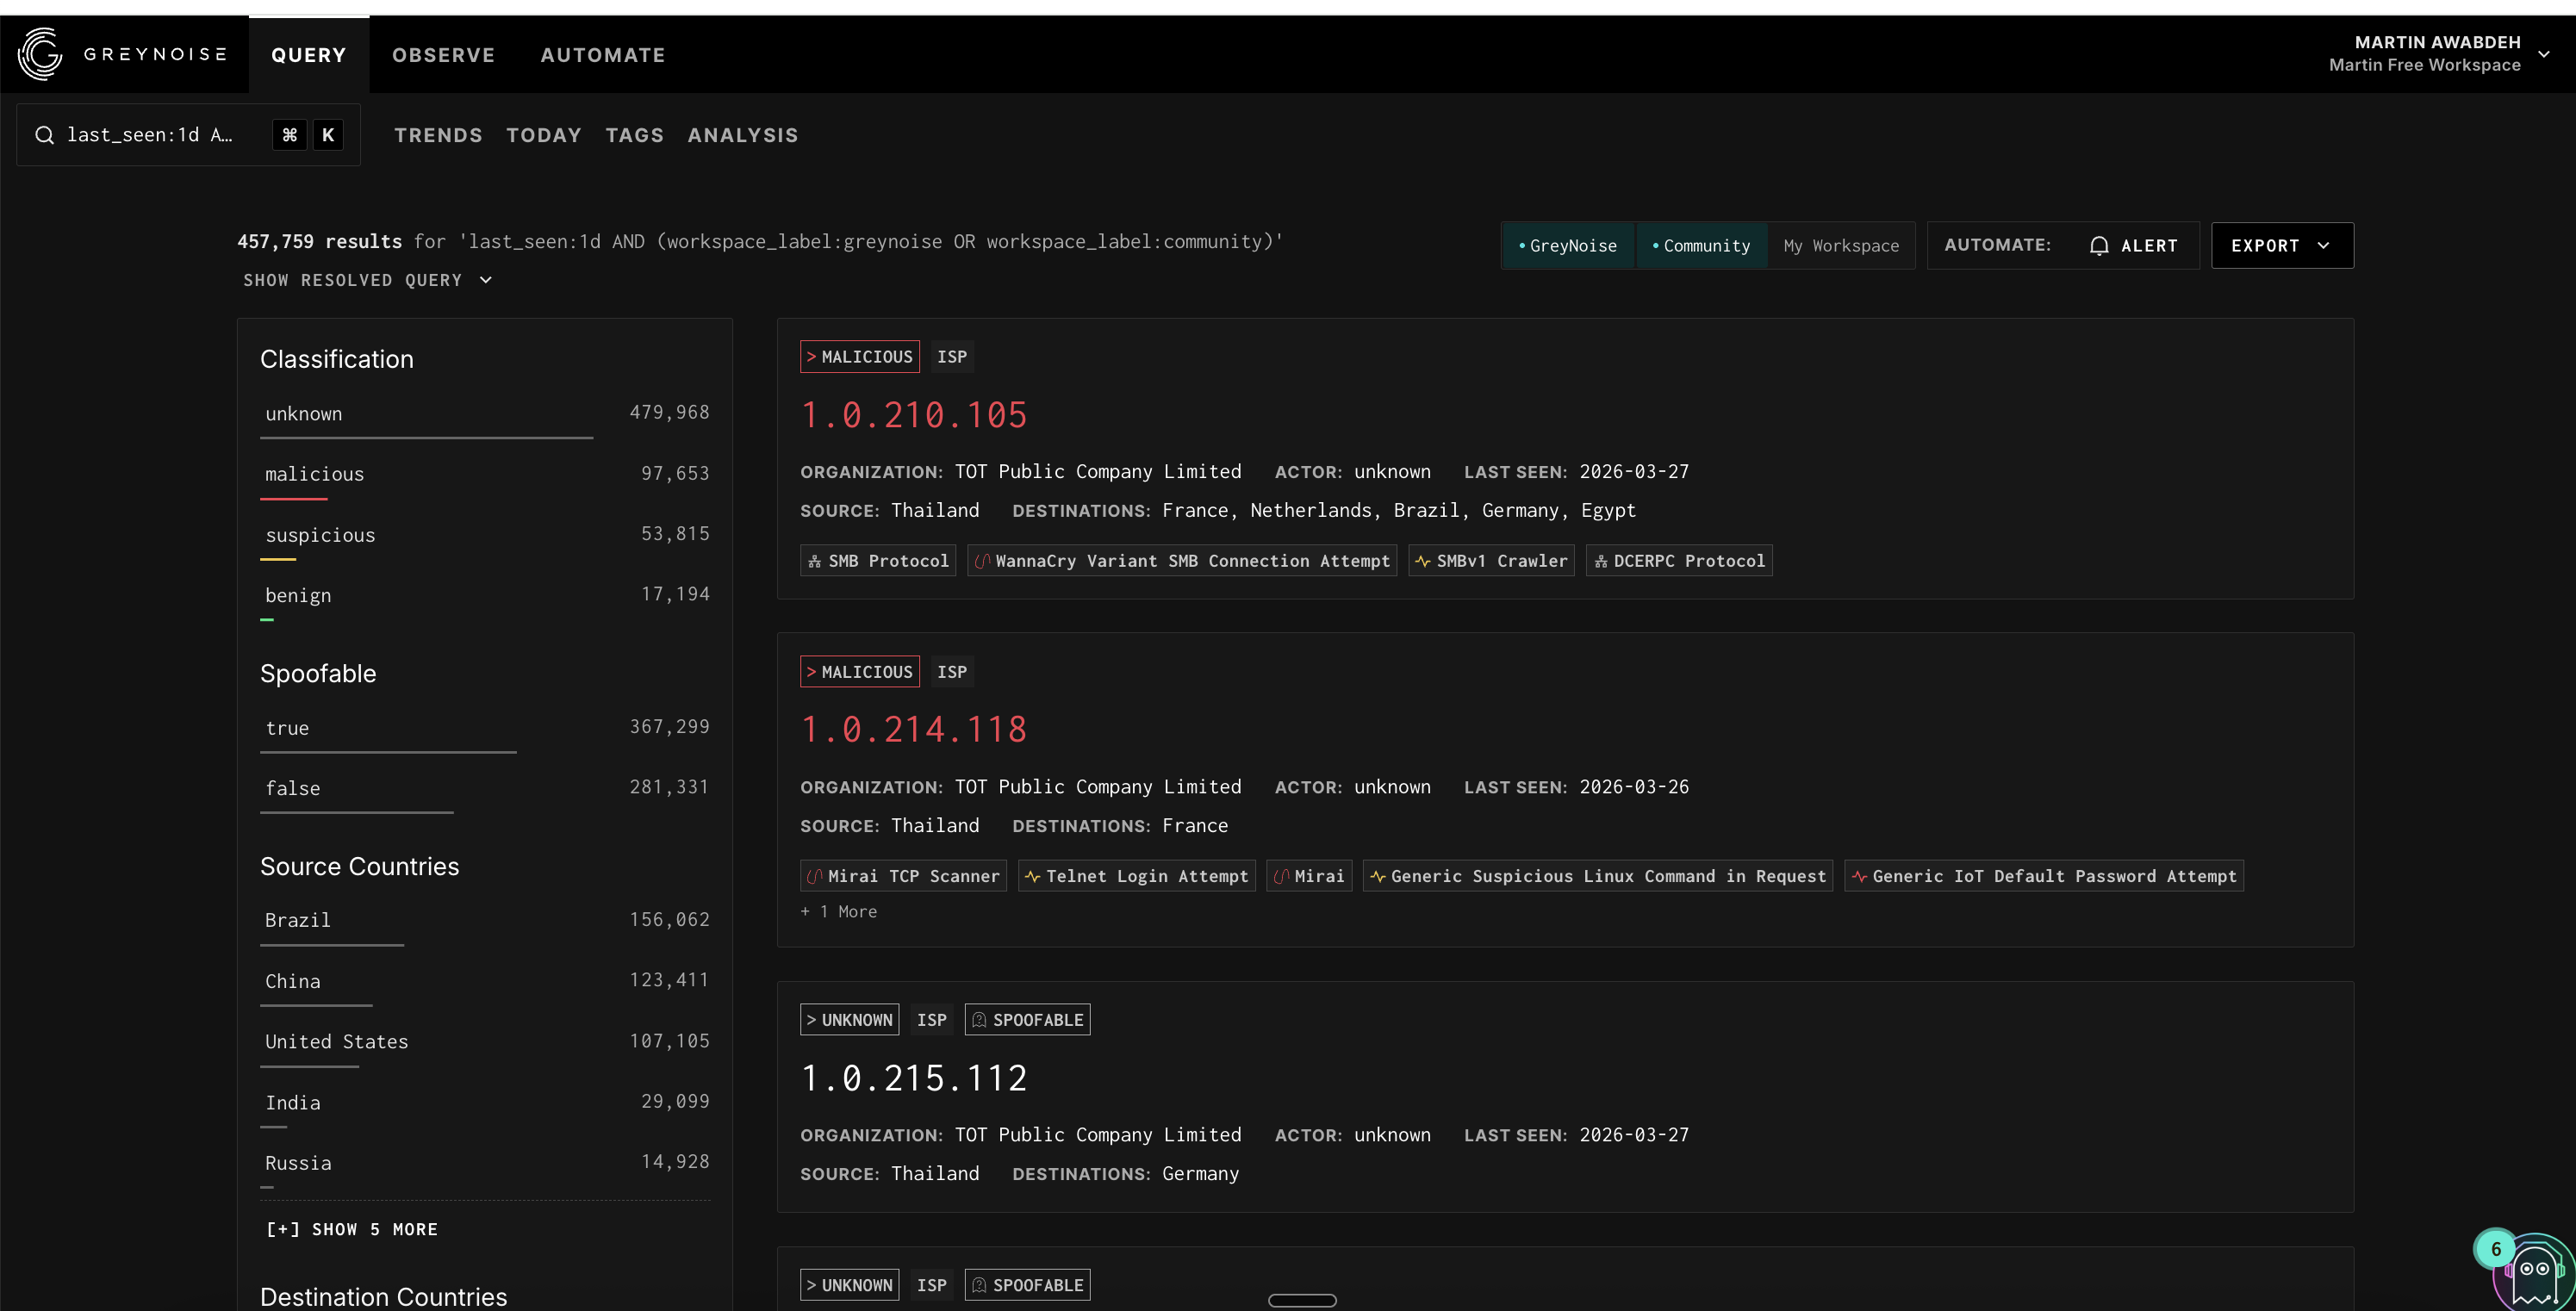
GreyNoise adds a third data tier alongside its own production fleet: telemetry from community-member-deployed sensors. Users can now switch between or combine three data scopes — GreyNoise, Community, and My Workspace — directly in GNQL results, IP details, and tag detail pages. Community sensors extend coverage into IP spaces and network environments GreyNoise's own fleet doesn't typically reach, resulting in broader, more diverse internet-wide visibility. Access is earned by deploying sensors: only users with active sensors (and paying customers) receive the entitlement — making the dataset a direct, tangible payoff of joining the Swarm. The more sensors the community deploys, the more powerful the dataset becomes.
Articles auth and entitlement checks now resolve correctly
Articles: auth and entitlement checks resolved across the Articles flow in Visualizer
Callback URL parsing tightened for cleaner IoC extraction
Callback pipeline: URL parsing tightened for cleaner IoC extraction, callback IPs no longer mixed into sensor IP data, and commonly-empty values ignored
Switch workspace without re-authenticating your account
Visualizer: Workspace and Account are now separated — users can switch workspace without re-authenticating their account context
Mar 26, 2026
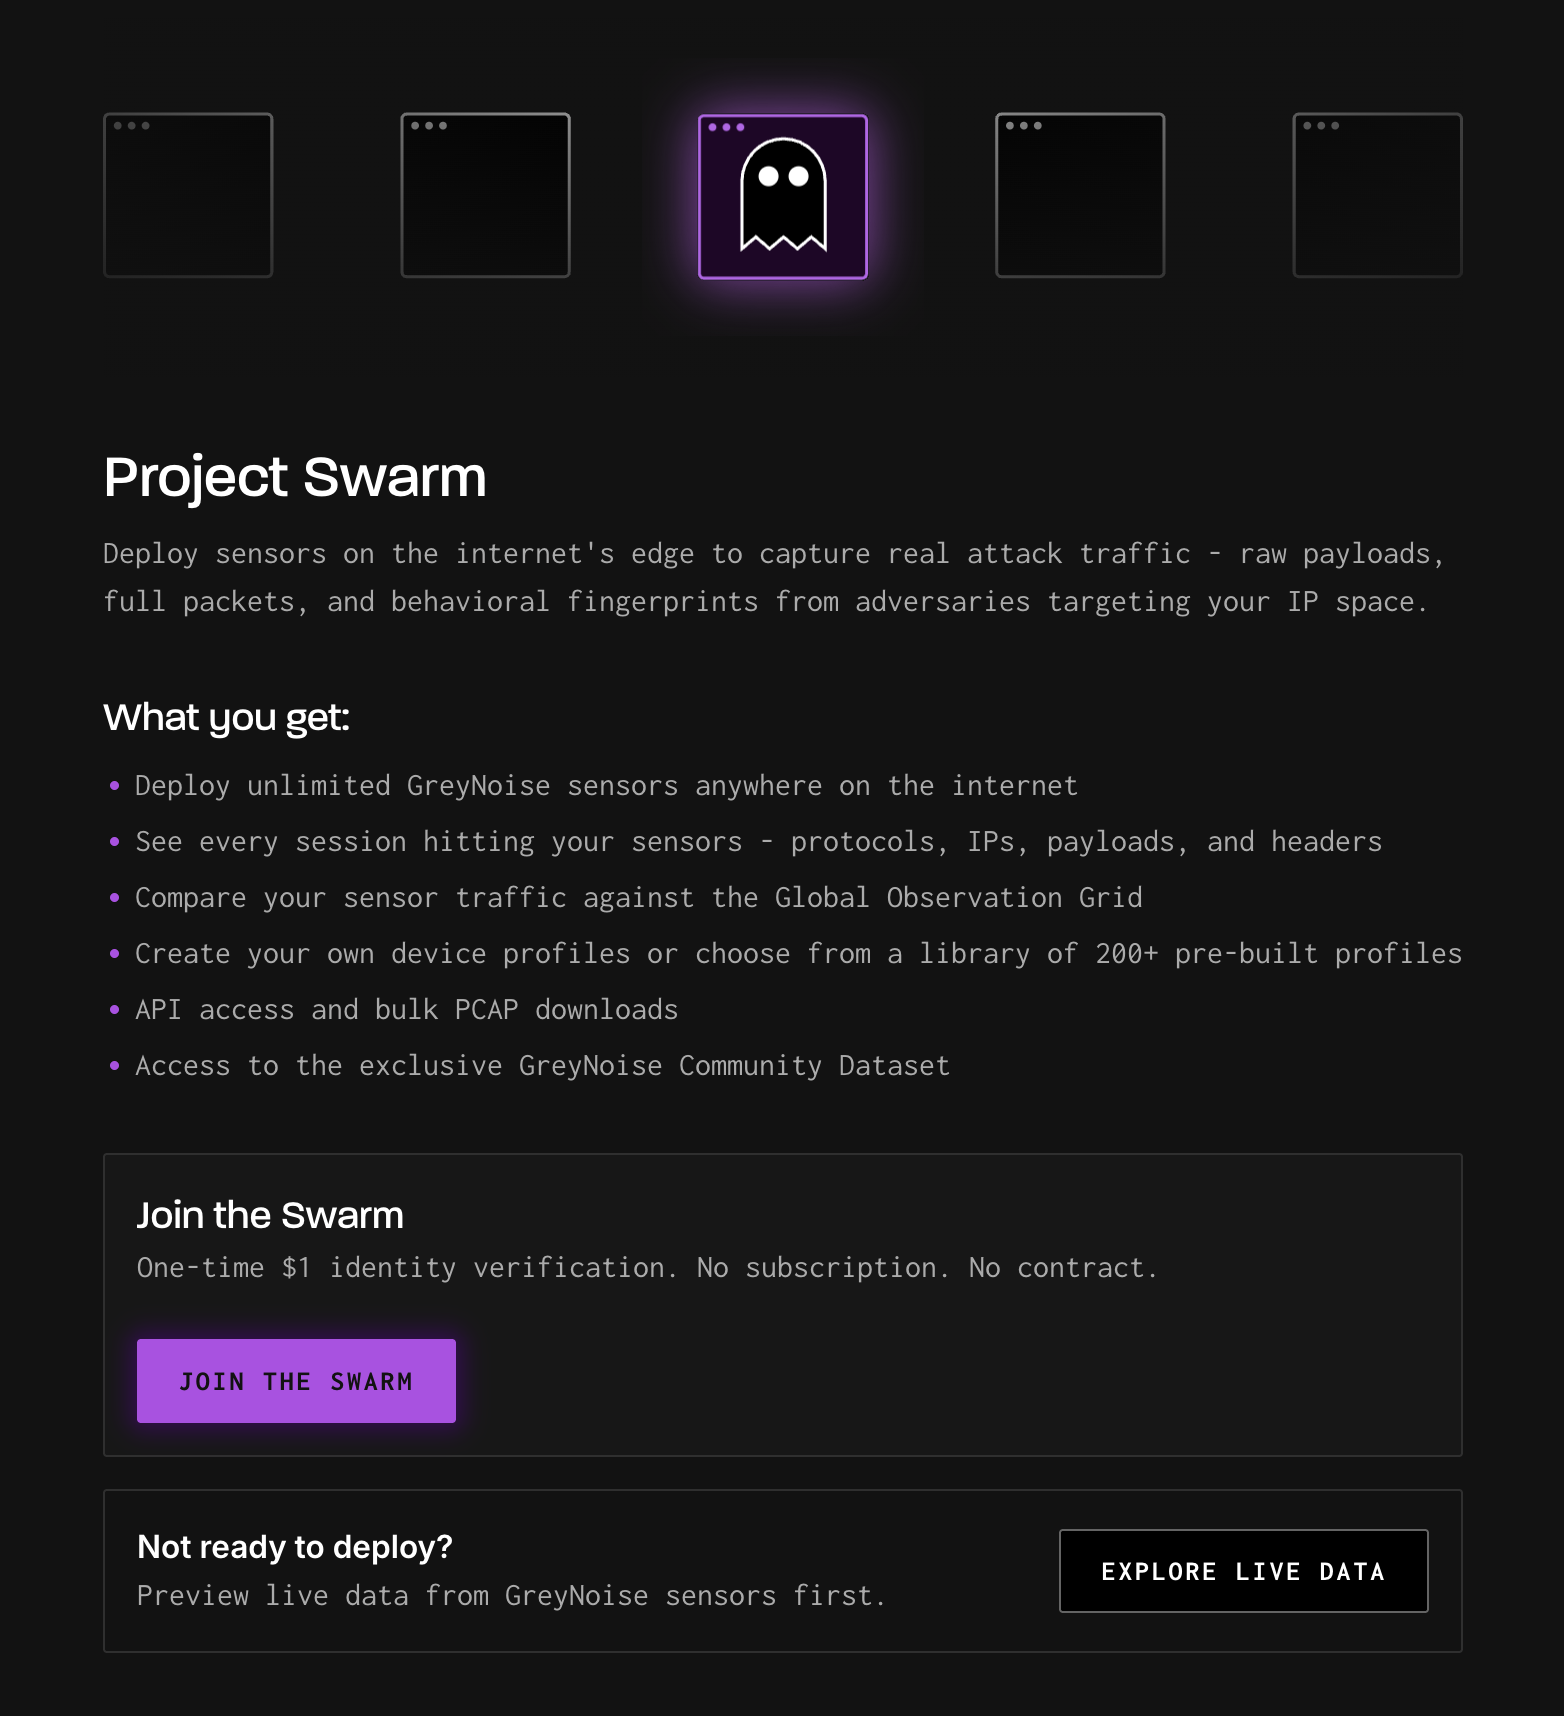
First revenue-bearing GreyNoise self-serve flow ships end-to-end. A new `/observe` paywall route hands users a Stripe checkout to buy Swarm for $1 and redirects back with a success state, fronted by a Swarm splash animation. Once paid, the Swarm/Spacewar onboarding flow walks new buyers through deploying their first sensor — a sensor-deployment UI and onboarding entry on Explore so a customer goes from credit-card to first sensor without a sales touch. Underneath, a new "greynoise" profile tier is recognized end-to-end (Visualizer display and behavior, sensor service API). The first self-serve product surface GreyNoise has ever shipped.
Session Explorer adds live auto-refresh
Session Explorer: live auto-refresh option added for continuously updated results
Workspace tags now returned from rulesets and batch tag endpoints
Workspace Tags: `/v2/***********` and `POST /v2/***********` ungated for workspace tags — returns official + workspace tags with `workspace_id` and `isOfficial`, unpublished drafts excluded
Mar 25, 2026
Customer-visible billing automation that ties entitlements directly to product participation. After the 30-day trial expires, the community-dataset entitlement is automatically granted or revoked based on whether the workspace contributed data in the past 90 days. Runs on the existing 24-hour schedule and uses promotional entitlements; an entitlement endpoint also exposes the list of workspaces opted out of community contribution. Customers who keep contributing keep access; customers who stop see access naturally lapse — no manual intervention from CS.

Newly deployed sensors now show an initializing state
Sensor service: new "initializing" sensor state surfaced for newly deployed sensors
Pivot dataset scope inline from the tag detail view
Tag Detail: DatasetScopeSelector added so analysts can pivot scope inline (powered by `workspace_labels` support on tag activity and IPs endpoints in GN API)
Session recall now supports captures up to 100 GB
Session service: recall max-bytes cutoff raised to 100 GB to accommodate larger captures
Skopje, Viettel, and Seville added to hosting provider data
Hosting data: Skopje (North Macedonia), Viettel (Vietnam), and Seville (Spain) added to the provider set
SSO now accepts Auth0 groups claim as string or array
Visualizer: Auth0 `groups` claim now accepted as either string or array, unblocking SSO/OIDC integrations whose IdPs return either format
Mar 24, 2026
Bosnia/Herzegovina and Cloud Adore added to hosting data
Hosting data: Bosnia/Herzegovina and Cloud Adore added as net-new providers
Full Articles CRUD, categories, sorting, and RSS now available
Articles: full backend CRUD lands — `CREATE`, `UPDATE`, `DELETE /:id`, category support, sorting, and an RSS feed — fleshing out February's in-product Articles surface
Scope selection added to IP timelines
Visualizer: scope selection added to IP timelines (with backing GN API workspace-filter support)
Workspace tags now sync through the same pipeline as official tags
GNQL sync: workspace-aware tag support and a new tag client — synced workspace tags now flow through the same pipeline as official tags
Mar 23, 2026
Article edit screen gains a change history view
Articles: edit screen gains a history view backed by a new changelog API endpoint; publish flow refactored into its own component
Workspace invite emails normalized to prevent mismatches
Visualizer Admin: workspace invite emails normalized to lowercase to prevent invite mismatches
Mar 20, 2026
Community Dataset URL and stats accuracy fixed
Community Dataset: URL and stats accuracy fixed, and the data-scope selector now hides when the workspace lacks the entitlement
Manage Articles view with create, update, and delete flow
Articles: Visualizer Manage Articles view added — create/update/delete drawer flow with ArticleForm
Workspace selectors added to Results and IP Details pages
Visualizer: workspace selectors added to Results and IP Details pages
Mar 19, 2026
BCM Footprints tags added from watchTowr research
Detection content: BCM Footprints tags added from watchTowr research
gRPC upgraded to patch CVE-2026-33186 across services
gRPC upgraded to v1.79.3 across the affected backend services to address CVE-2026-33186
Mar 18, 2026
Visualizer remembers your default workspace at sign-in
Visualizer: user default workspace persisted so Viz lands on the right scope on sign-in
Mar 17, 2026
Fewer periodic 502s when loading the Visualizer
Infrastructure tuning to cut the periodic 502s seen when loading the Visualizer
Mar 13, 2026
Two new feed types — Callback File Feed and Callback IP Feed — exposed through the existing Feeds workspace UI. Customers who already subscribe to tag, CVE, and JA4 spike feeds can now get callback-derived signal the same way: every new callback file or IP the pipeline observes fans out to their configured webhook.
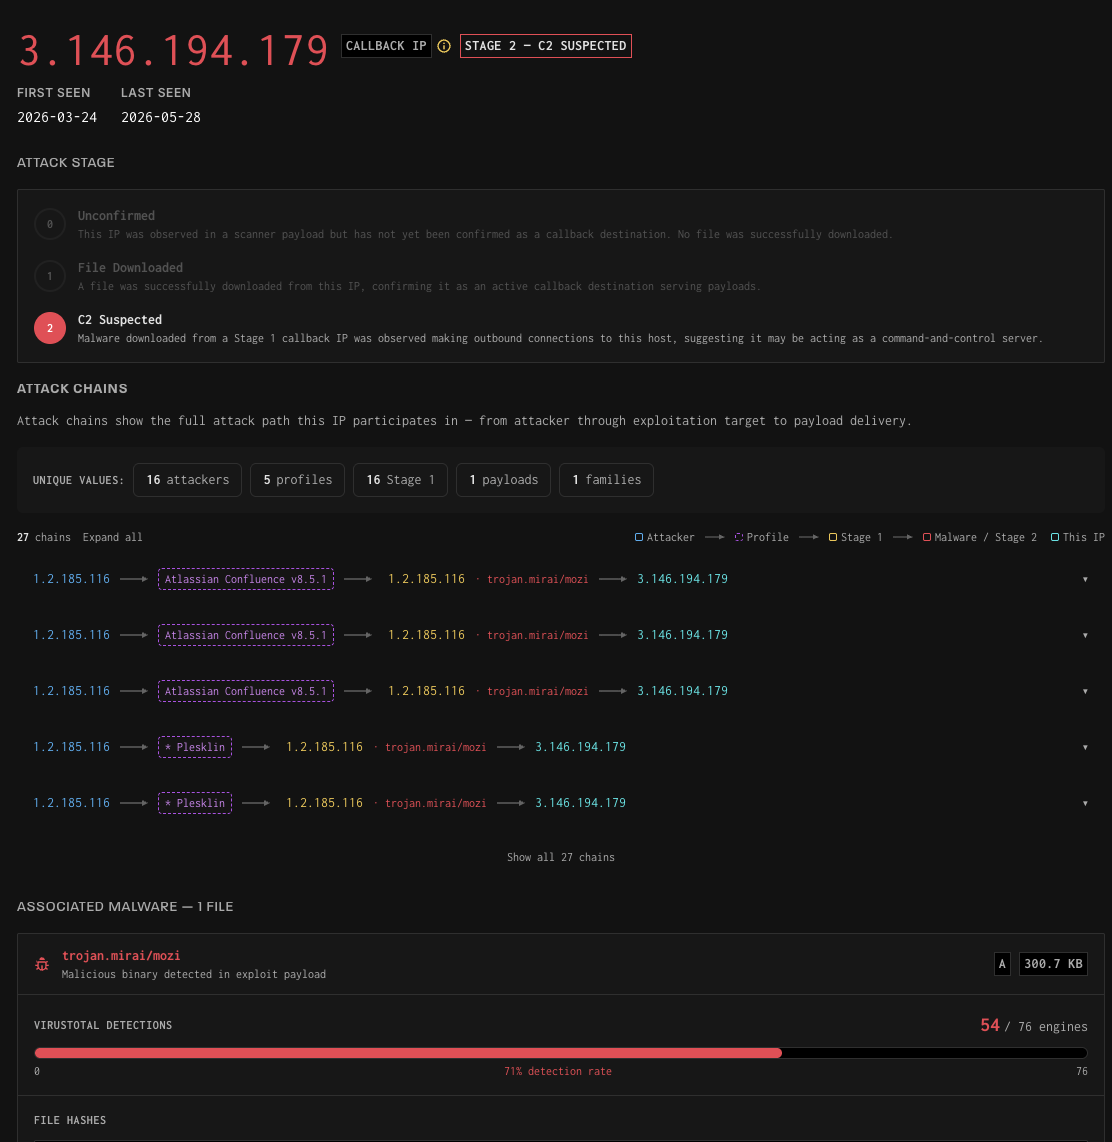
Callback Intelligence is a new dataset that exposes attacker-controlled infrastructure referenced in exploit payloads — shifting GreyNoise from pre-exploitation visibility into post-exploitation intelligence. Where scanner data answers 'who is scanning me?', Callback Intelligence answers 'are systems in my environment communicating with attacker infrastructure?'. A dedicated Callback tab in the Visualizer surfaces searchable, filterable callback IPs with attack stage classification (Unconfirmed → Stage 1: File Downloaded → Stage 2: C2 Suspected), detail pages with associated malware files, hashes, and multi-engine VirusTotal detections, and full API access. Analysts get faster identification of compromised hosts, clear prioritization by attack stage severity, and direct access to malware hashes for triage and hunting. A major step toward 'moving further right on MITRE'.
GNQL adds workspace_label facet and free-text search terms
GNQL — workspace_label Facet, "greynoise" Alias, Generic Search Terms: workspace_label is now a first-class queryable facet, "greynoise" works as an alias for "noise", and the query engine accepts generic free-text search terms
March CVE wave adds dozens of new detection tags
Detection content: March CVE wave — substantive month of individual CVE tags including Junos OS Evolved (CVE-2026-21902), Cisco/Snort regex fixes, Artica Pandora FMS, Alibaba metadata, plus ~30 others spanning CVE-2024 through CVE-2026, and bulk triage batches
Resolve IPs directly through the GNQL query path
GNQL: IP-lookup endpoints added to the GNQL query service so callers can resolve IPs directly through the same path
Mar 12, 2026
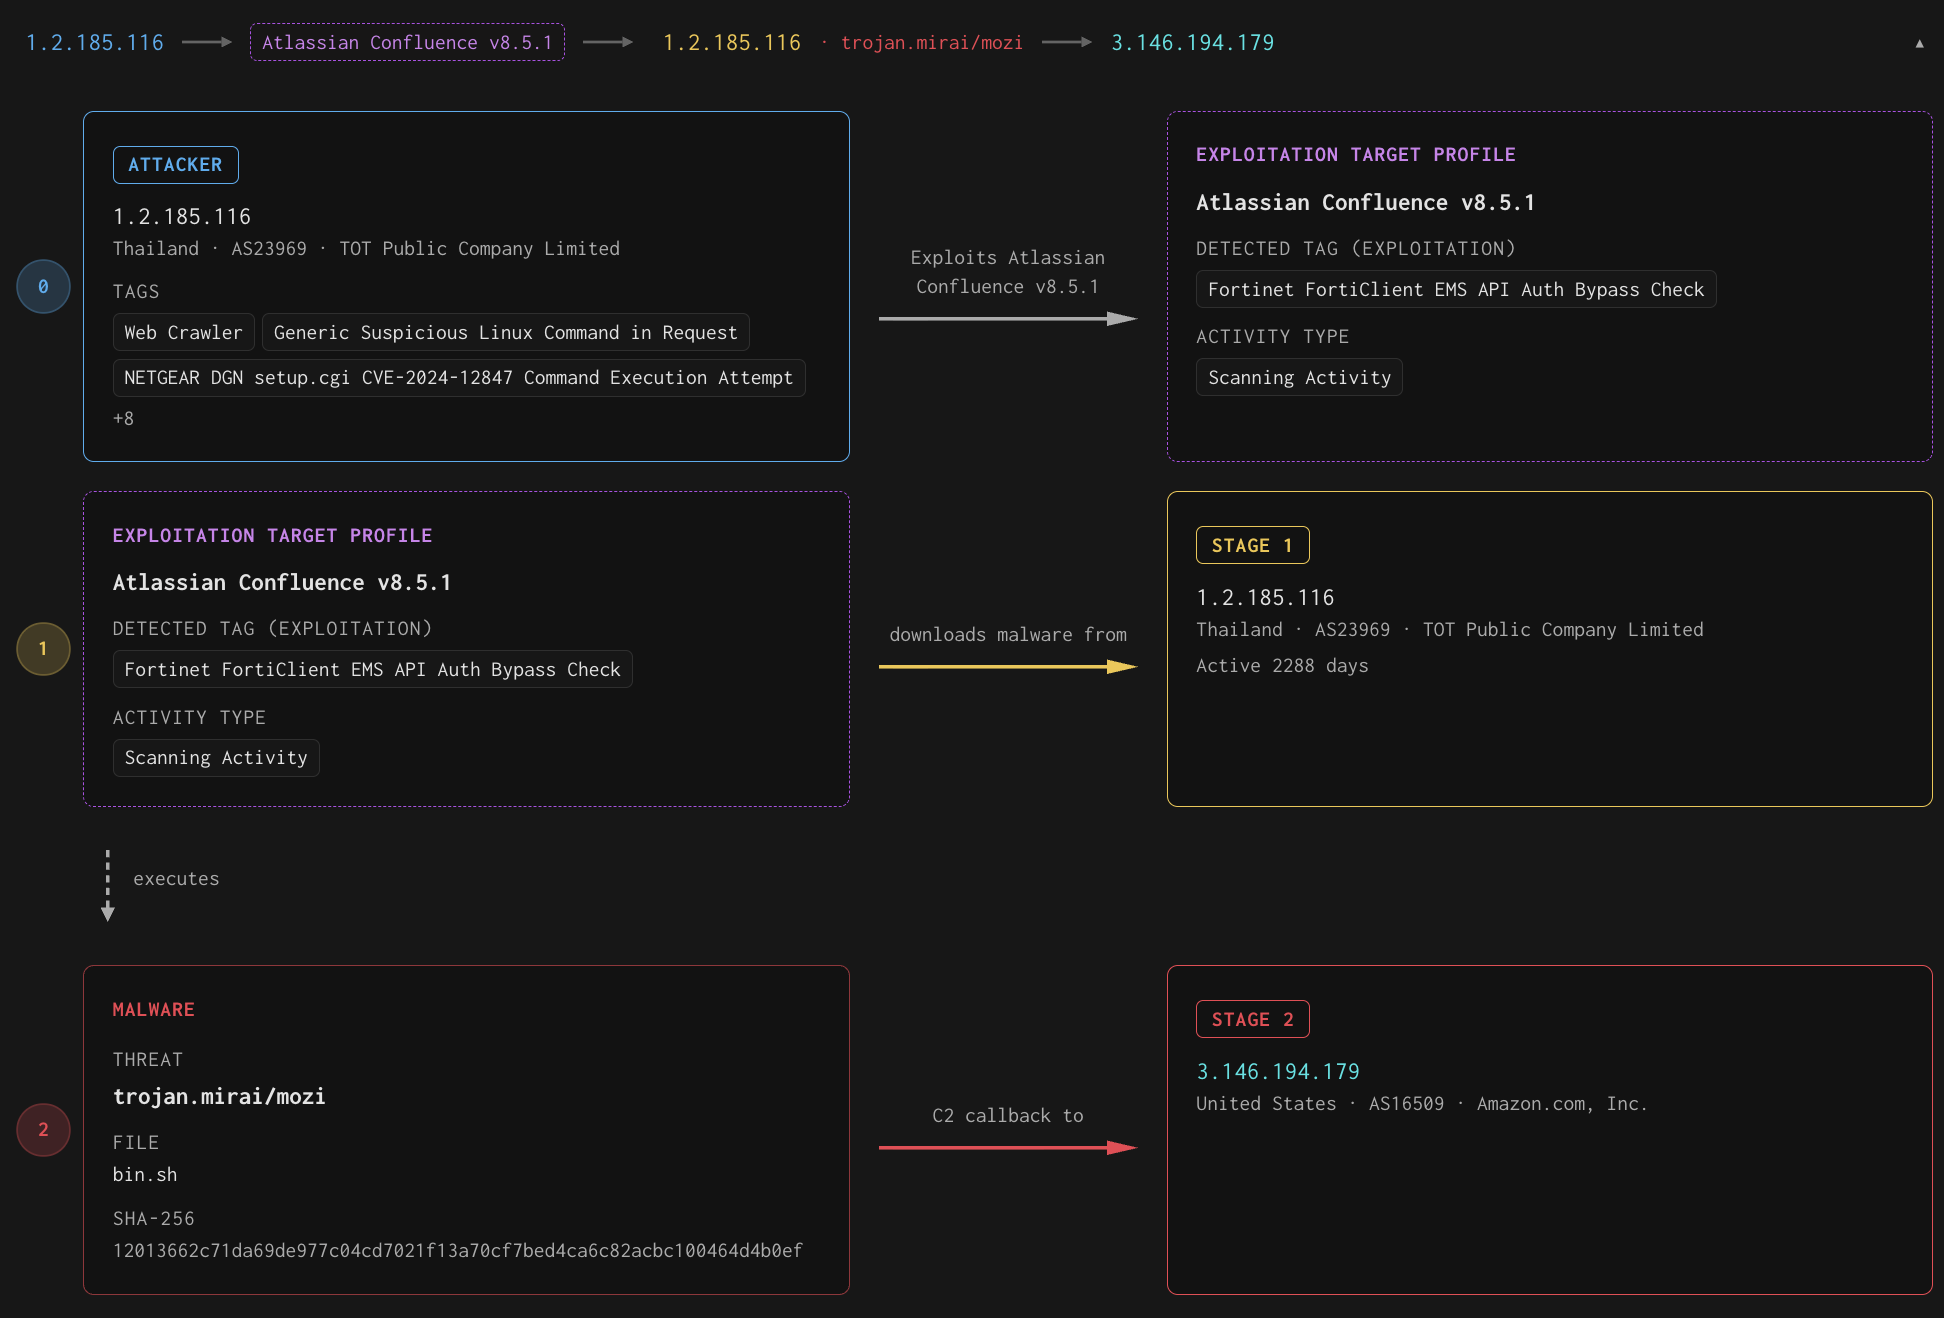
Replaces the prior 2-tier model with a `0=detected / 1=file analyzed / 2=confirmed` progression across the full callback pipeline, the GN API, and the Visualizer. Adds `is_stage_1`/`is_stage_2` booleans, drops the legacy column, and tightens Stage-2 promotion to require corroborated VirusTotal evidence. Gives analysts a sharper read on how far an attack chain has been validated — `detected` (we saw the callback), `file analyzed` (we pulled and analyzed the payload), `confirmed` (multi-engine corroboration). The classification ships through GNQL and is visible on every callback record customers query.
Mar 11, 2026
Same-week Citrix NetScaler KEV tag and VulnCheck import wave
Detection content: same-week Citrix NetScaler ADC/Gateway KEV tag (CVE-2025-6543), experimental Citrix NetScaler scanner module, large VulnCheck import wave catching up on missing rules, and a wave of scanner tags migrated to the new transactional style
The AI agent adds GPT-5.4 and recommends gemini-3-flash
AI agent: model lineup expanded — GPT-5.4 added, gemini-3-flash labeled recommended (preview label removed), plus explorer-translate and small UI follow-ups
Mar 9, 2026
25 more Snort-derived Suricata tags converted
Detection content: the Snort-conversion program — another 25 Snort-derived Suricata tags converted (batch 3)
Sensor search no longer redirects to the deploy wizard
Visualizer: sensor search no longer incorrectly redirects to the deploy wizard
Mar 6, 2026
Session Explorer adds an explicit Demo scope
Session Explorer: `all_workspaces` replaced with an explicit Demo scope
View a single article in the Visualizer
Articles: Visualizer View Article page wired up to the Articles API — first customer-visible single-article surface
Mar 4, 2026
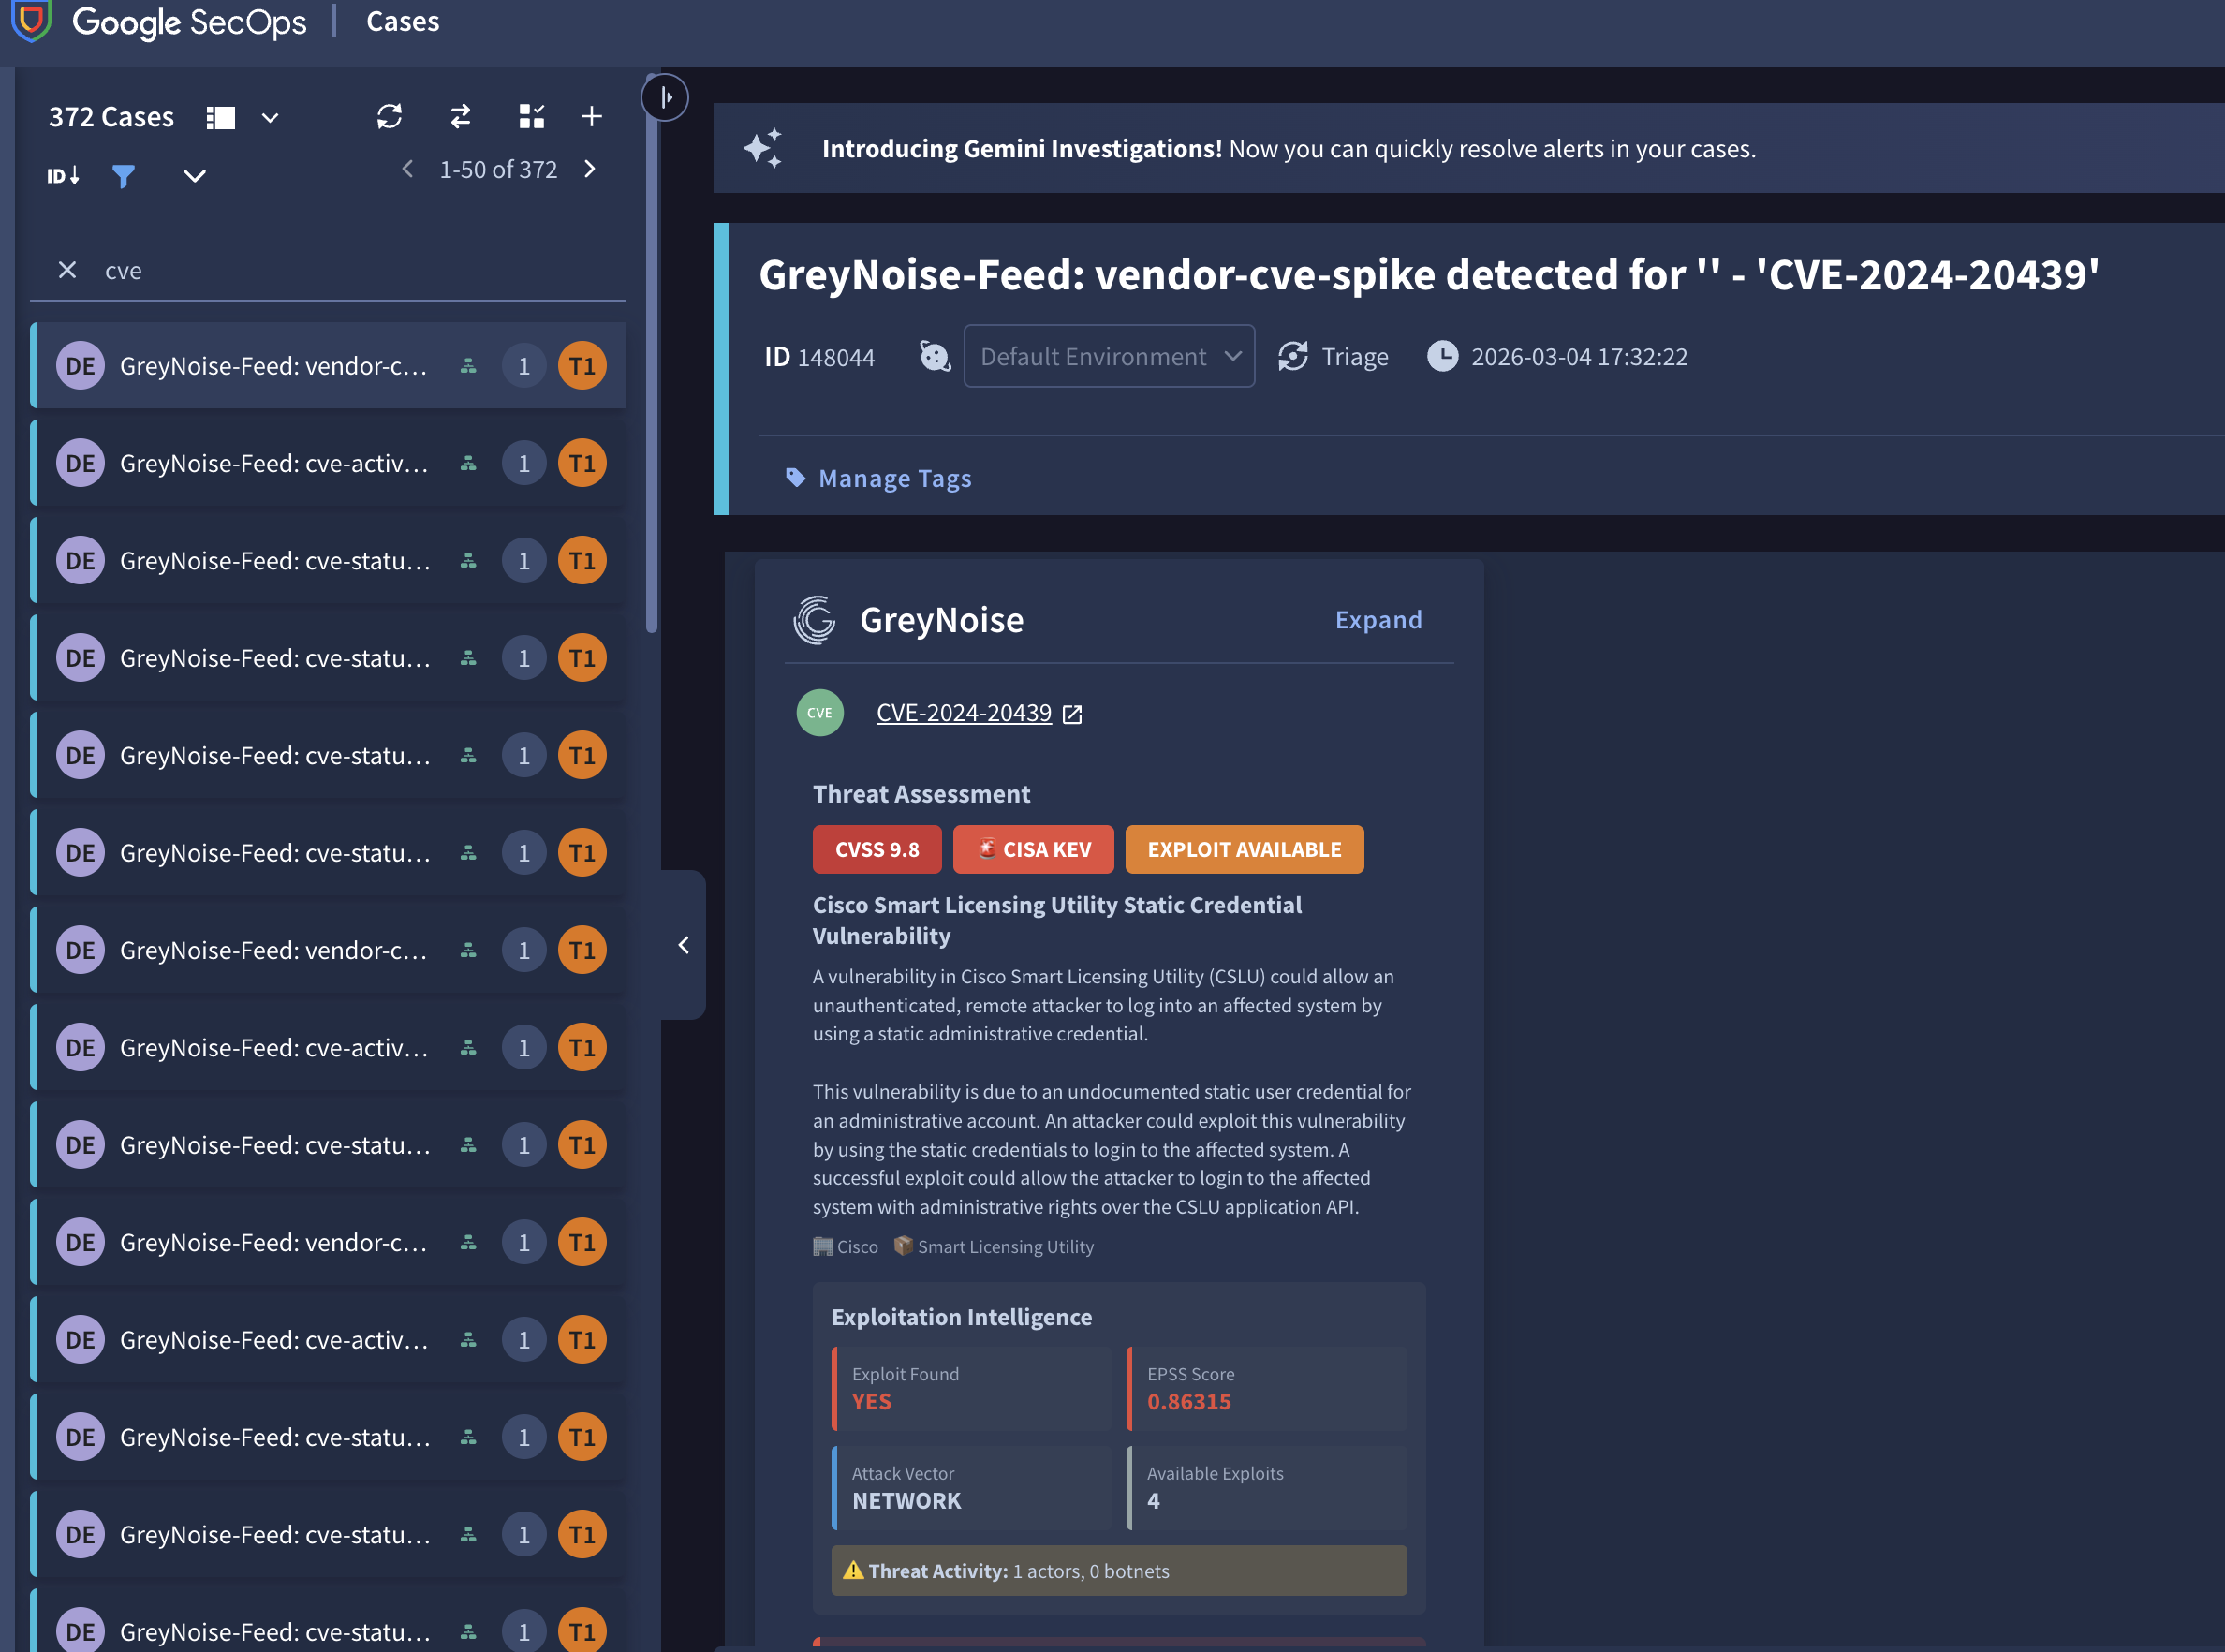
Comprehensive Google SecOps integration ships across both SIEM and SOAR. On the SIEM side: a Google-approved ingest script for importing GreyNoise indicators, new dashboards, detection rules, and saved searches. On the SOAR side: updated response actions covering IP Lookup, Quick IP, IP Timeline, CVE, and GNQL; webhook support for GreyNoise Alerts and Event Feeds; and new playbooks. Any joint Google SecOps customer gets access — no additional data module required for IP enrichment.
Mar 3, 2026
Session Explorer column menu no longer cut off on short lists
Session Explorer: column-header menu no longer cut off when the session list is small
Mar 2, 2026
Session Explorer now shows HTTP details on existing sessions
Session Explorer: field list now always includes HTTP fields, fixing missing HTTP details on existing sessions
Feb 27, 2026
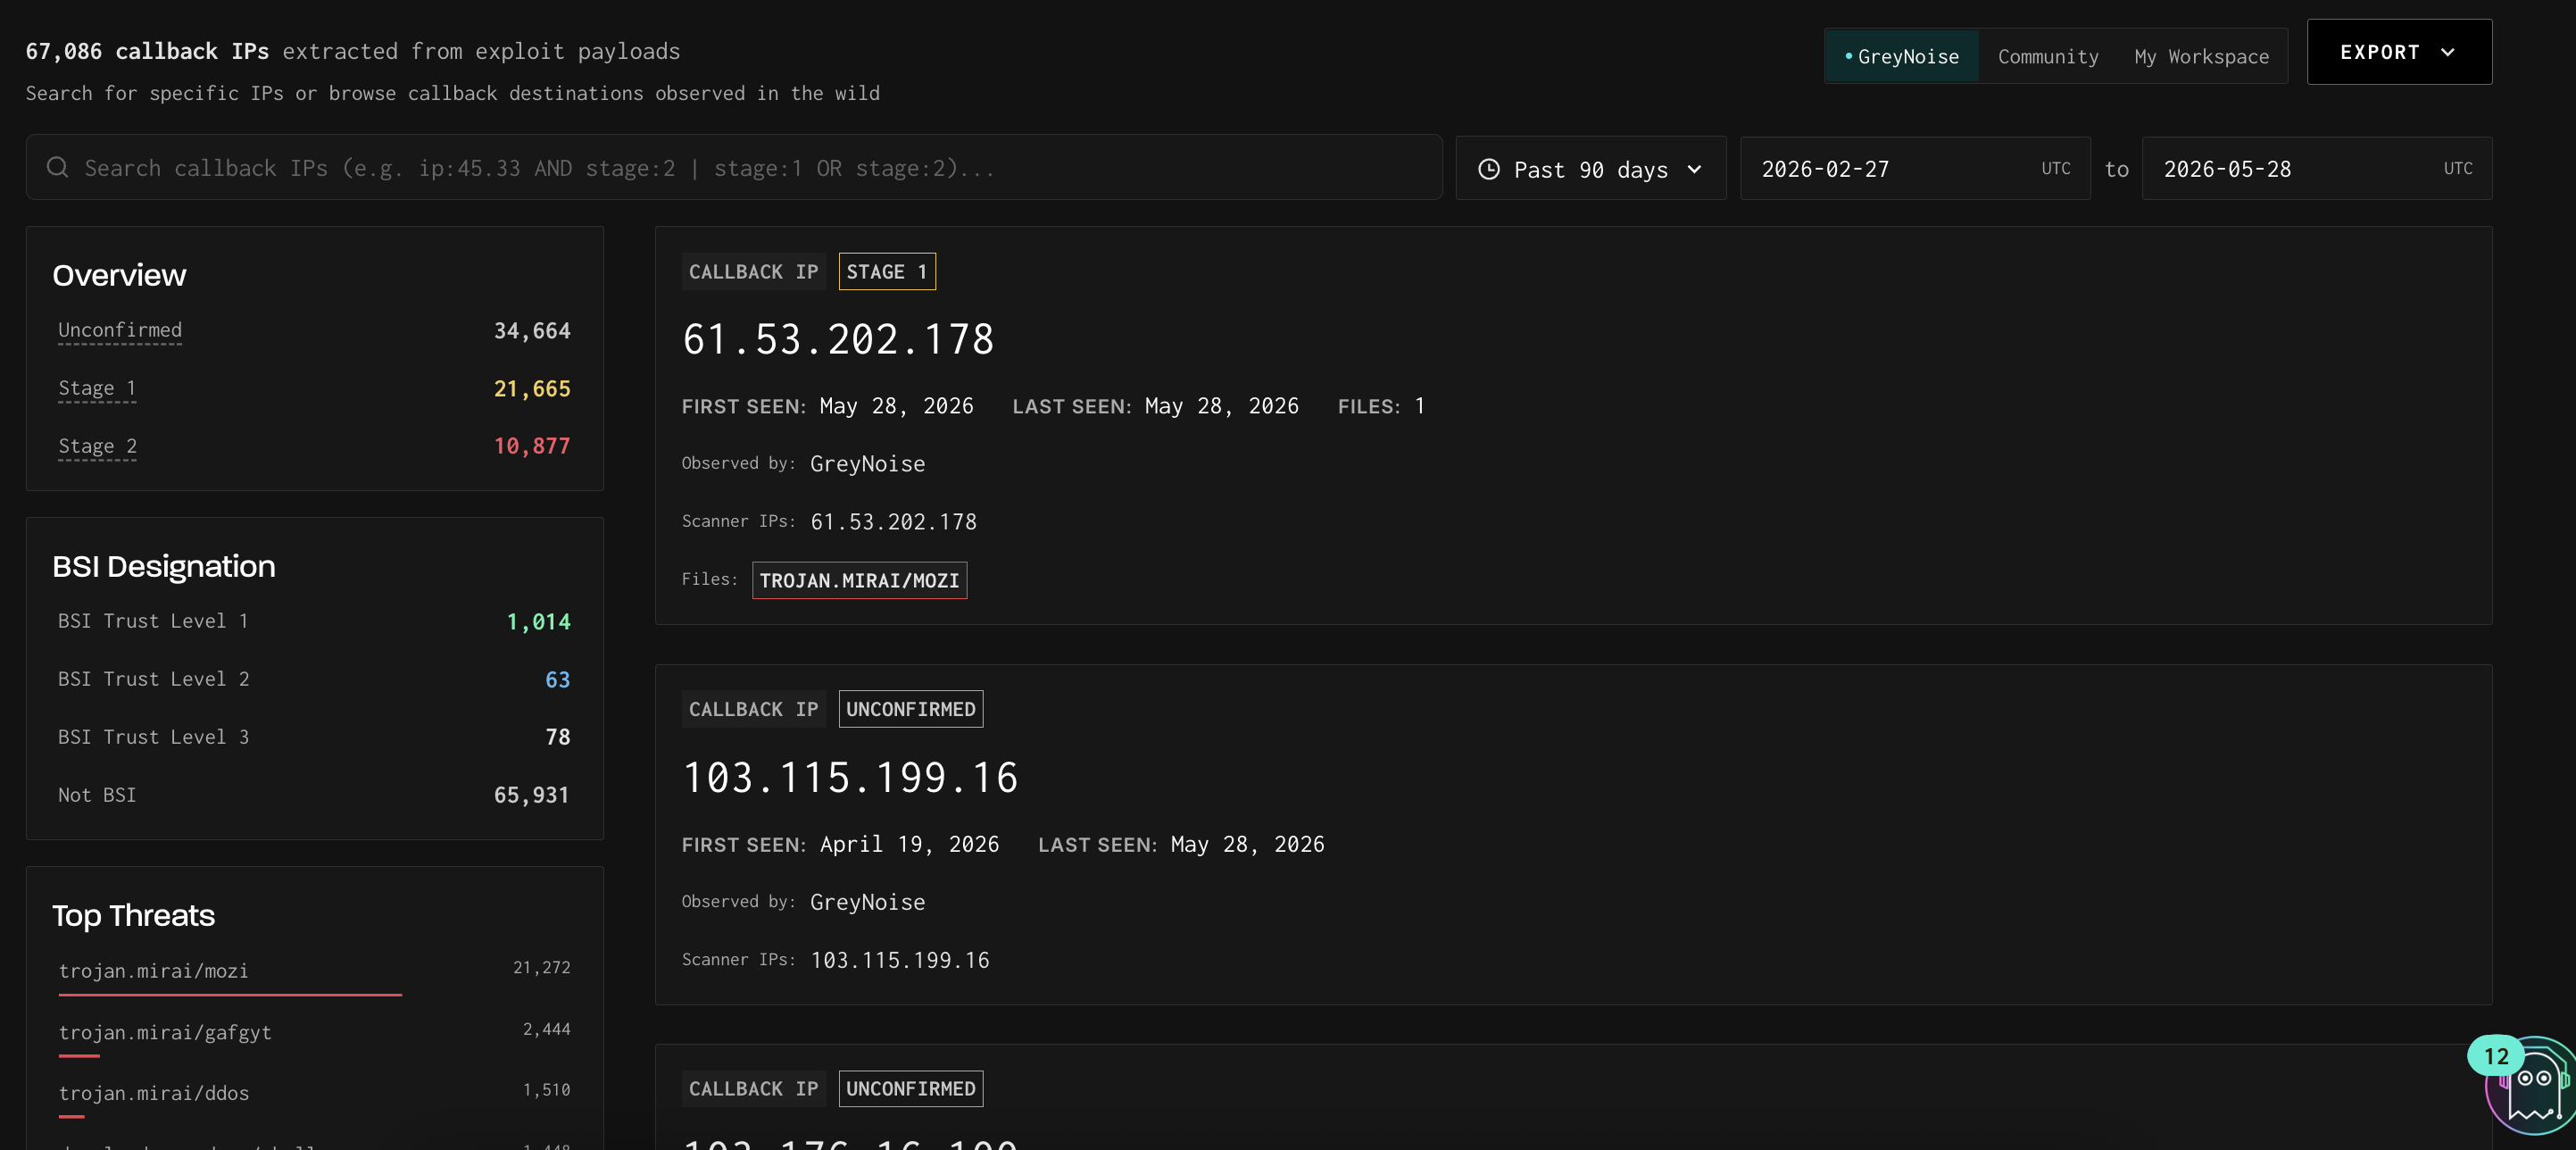
New `callback_ips` GNQL facet lets customers find every scanner whose captured payloads referenced a given C2 IP — e.g. `callback_ips:1.1.1.1` returns every scanner pointing back at that destination. GreyNoise extracts callback IPs from captured HTTP traffic, aggregates them daily, and makes them queryable through GNQL and the public API with entitlement gating.
Feb 26, 2026
GNQL searches retry to avoid intermittent errors
GNQL Query: searches now transparently retry on the class of backend script error that produced intermittent 400s on records with unexpected nulls
Same-day Cisco SD-WAN RCE tag plus Sparkrat and more
Detection content: same-day tag for Cisco SD-WAN DTLS RCE (CVE-2026-20127); new tags for Sparkrat, CVE-2021-27931, the second Snort-generated rules batch, and a WordPress enum update; plus multi-week tag drops and triage batches
Suricata-rule linting blocks invalid workspace tag submissions
Workspace Tags: Suricata-rule linting now runs inside the tag-creation flow — errors block submission until lints pass, raising the floor on customer-authored detection content
Feb 25, 2026
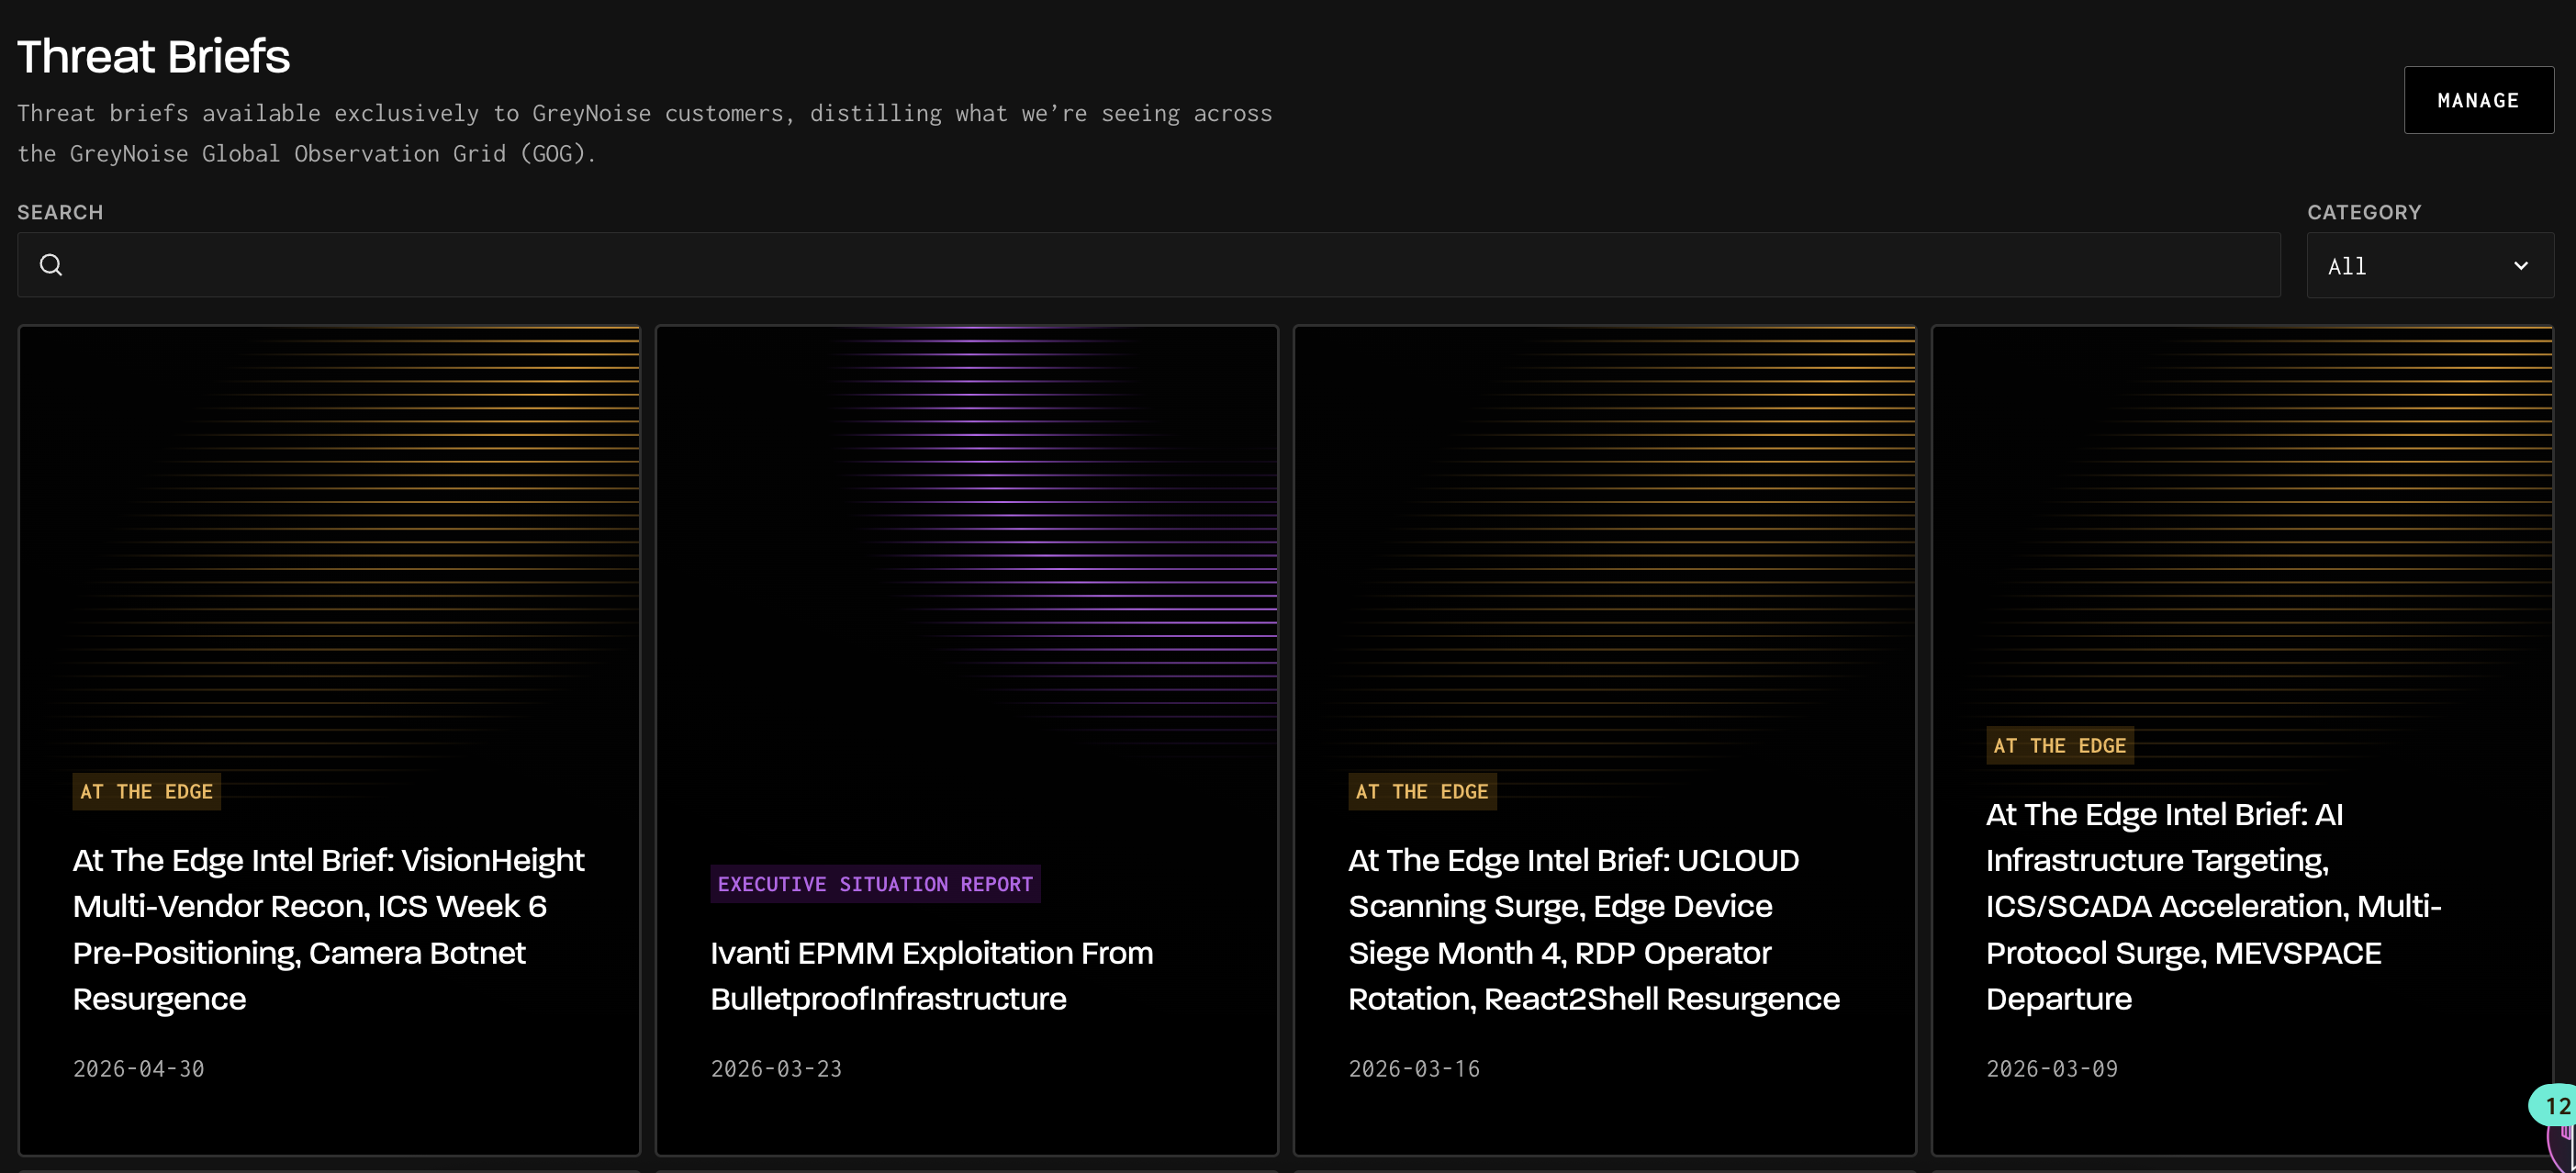
A new Article Catalog inside the Visualizer surfaces GreyNoise threat research — Threat Briefs, Executive Situation Reports, and At The Edge intel — directly alongside the data it covers, searchable and browsable without leaving the product. The first net-new content surface added to the Visualizer.
Daily CVE-CPE refresh backs CVE vendor and product endpoints
CVE data: daily CVE-CPE mapping refresh from the public data set now backs the CVE vendors and CVE products endpoints
Feb 24, 2026
IP Diff endpoint pagination fixed
GreyNoise API: pagination on the IP Diff endpoint fixed
JA4 queries null-check fields to stop intermittent 400s
GNQL Query: JA4 field lookups now null-check parent objects before child access, eliminating intermittent 400s on records with missing tcp/tls/http/ssh raw data
Feb 23, 2026
The complete JA4+ fingerprint suite is now queryable in GNQL, visible in the Visualizer's IP activity summary with encoded/decoded toggle, and exposed in the public API with entitlements. Hunt customers gain four additional fields: JA4T (TCP) fingerprints the underlying OS and network stack from handshake characteristics; JA4H (HTTP) distinguishes browsers from bots and scanners by header structure; JA4SSH fingerprints encrypted SSH sessions to identify brute-force tools and automation; and JA4L (Latency) flags inconsistencies between claimed geolocation and observed network timing — a reliable signal for VPN and proxy masking. Stacked together, these signals let analysts pivot on behavioral fingerprints instead of IP reputation alone, cluster attacker infrastructure with higher confidence, and detect shared tooling even through encryption. Bulk Data customers on GCP also receive JA4 in daily exports.
New SonicWall, Proxmox, and Cypex detection tags
Detection content: generic SonicWall login tag, Proxmox VE API credential-attempt tag, Cypex scanner tag, and SSL VPN login + CVE-2024-53704 refinements
Feb 20, 2026
Empty-state messages restored on the IP activity summary
Visualizer: empty-state messages restored on the IP activity summary view
JA4 fields now ship to GCP bucket customers
Bulk Data: JA4 fields now shipped to GCP-bucket customers separately from S3 payloads, so JA4 reaches new consumers without changing existing S3 contracts
Feb 19, 2026
New tags for Hanwang, Hail Cock botnet, and five CVEs
Detection content: Hanwang EFACEgo file-upload tag, Hail Cock botnet tag, and a five-CVE batch covering CVE-2018-1217, CVE-2018-11686, CVE-2019-20224, CVE-2023-27351, and CVE-2024-6393
Spike alerts now name the exact CVE, tag, or vendor that fired
Spike detection: when no value filter is set, each CVE/tag/vendor is now spike-checked individually and fires a separate event with the triggering identifier, so downstream consumers know exactly which entity tripped the threshold
Feb 18, 2026
IP detail dates now align with GNQL search boundaries
GNQL Query: IP-data endpoints now use day-rounded date math matching GNQL search boundaries — fixes the case where a GNQL search returned an IP near the data-reach edge but the IP detail endpoint showed 'Not Observed'
Spike query thresholds now reject zero, matching the UI minimum
GNQL Query: minimum-IP-count and percentage spike criteria now reject `0` at the API, matching the UI's minimum of 1
Feb 13, 2026
Two new Feeds event types give Advanced and Elite customers high-signal alerts when attacker interest meaningfully surges — without tracking individual CVEs or maintaining custom detection logic. Vendor Activity Spike fires when activity across a vendor's CVE ecosystem spikes over a rolling window; Tag Spike fires when activity matching a specific GreyNoise tag surges. Both are configurable by the customer and use wildcard matching to stay current as tags and CVE mappings evolve. Customers can prioritize patching, response, and investigation based on real-world exploitation trends tied to the vendors and threat categories they care about.
Major expansion to Feeds giving customers significantly more control over how and when alerts fire. Target Workspace selection scopes feeds to either the Global Observation Grid or a customer's own sensor data — so teams with private infrastructure monitor threats to their environment, not just internet-wide trends. Configurable comparison windows (Hour-over-Hour, Today vs Yesterday, Week-over-Week, 20-Day Baseline, and Custom intervals) let teams detect spikes on business-relevant timeframes. Silence Periods suppress duplicate alerts for a defined duration, reducing fatigue on high-volume CVEs, vendors, or tags. Spike payloads are also restructured with `baseline_counts`, `analysis_counts`, and `delta_total_ip_count` — plus a timestamp field to prevent deduplication issues in webhook platforms — making downstream automations more reliable.
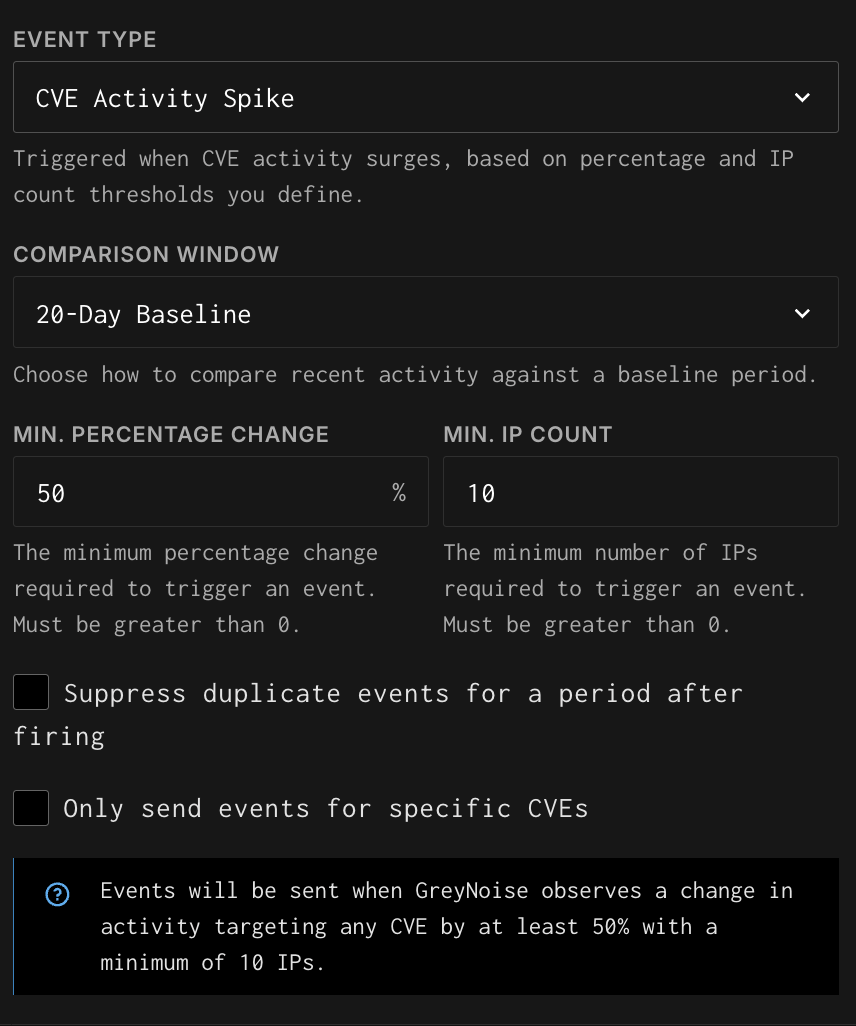
New customer-facing export path: run any GNQL query against Sessions and download a PCAP containing the packets associated with every matching session, in one shot. Pairs with January's in-product Streams Viewer and December's PCAP Viewer to close out the Sessions investigation surface — analysts can now inspect payloads in product and extract bytes for any matching cohort without leaving the Visualizer. Required a sessions-export endpoint on the Session service, channel-based streaming through the session client, and a public GN API export endpoint.
Block now shows a cookie consent banner
Block: cookie consent banner added, modeled on Visualizer's dismiss-based consent but native to Block's Nuxt UI / Tailwind stack
Choose a target workspace when creating an alert
Visualizer: alert form now has a Target Workspace dropdown matching the blocklist pattern, with backend support across the alerts handler and validation schemas
Disabled legacy tags no longer appear in the tag list
Visualizer: Tags list switched to the v3 endpoint, so disabled tags from the legacy tag server no longer leak into the UI
Same-week tags for AdForest, plus new CVE coverage and a Suricata fix
Detection content: same-week tag for CVE-2026-1729 (AdForest WordPress auth bypass), new tags for CVE-2025-52488 and CVE-2025-64095, Friday triage batch covering Adobe AEM default-login, BeyondTrust CVE-2024 session-search rule, and a ProxyLogon SSRF investigation, plus a Suricata `distance:0` fix unblocking missed tags
Feb 12, 2026
Alert delivery now skips stale alerts and broken endpoints
Alerts: two-level staleness tracking (alert-level and recipient-level) added — alert runs now skip known-stale alerts and broken delivery endpoints instead of burning compute on them
Feeds stop retrying webhooks known to be broken
Feeds: stale-webhook tracking — the feeds consumer now records delivery outcomes, computes staleness from consecutive failures, and stops attempting delivery to webhooks that are known broken
Run blocklist GNQL queries under a chosen workspace
Blocklists: workspace selector — GNQL queries can now run under a chosen workspace context via a `query_workspace_id`, with periodic refresh deduplication keyed on (query, workspace) instead of query alone
Feb 11, 2026
New tag for CVE-2026-1731 plus a bulk VulnCheck tag batch
Detection content: new tag for CVE-2026-1731 (company-identifier check) and a bulk VulnCheck-derived tag batch
Tags with forward slashes now match in GNQL queries
GNQL Query: tags containing forward slashes (e.g. `IF-T/TLS VPN Negotiation Attempt`) now match correctly — the slash is properly escaped in the Lucene regex pipeline
Feb 10, 2026
New CVE and research tags, plus suspicious tags now recommended
Detection content: tag for CVE-2020-29597, research tag for CVE-2026-0770 (Langflows validate endpoint), Odin tag, and a bulk update marking all `sus` (suspicious-classification) tags as recommended
Feb 9, 2026
Activity spike detection compares any field against its baseline
Spike detection: a generic Activity Spike observation type — compares a recent analysis window against a historical baseline for any supported field, with CVE spikes live first and tag/JA4/port spikes only needing a constant added; the framework under future spike-based feeds
New v3 API endpoints to manage workspace-scoped tags
GN API v3: new workspace tag endpoints under `/v3/***********` for listing, creating, reading, updating, and deleting workspace-scoped tags, backed by the new tag service
Feb 6, 2026
GNQL input now detects and wraps IP ranges in queries
Visualizer: GNQL query input now detects IP ranges, supports ranges mixed with other parameters, wraps long resolved queries in the code box, and handles line breaks in the resolved-query dropdown
New Nuclei-derived tags across Cisco XE, Yonyou, Dahua, and Jira
Detection content: multi-day Nuclei-template-derived tag drop covering a cleaned-up Cisco XE tag, the full Yonyou directory, Weaver, Prestashop, a large Dahua batch, and additional Jira tags
Feb 5, 2026
Block IP list now shows the configured max instead of a misleading count
Block: IP-list view now shows the configured `max_ips` value when total IPs exceed the configured limit, instead of the misleading completed-scroll count (e.g. `4000/4000` instead of `4265/4000`)
CVE spike alerts now fire per subscribed workspace
Spike detection: a new CVE-spike observation type fires one event per subscribed workspace, with per-workspace time-series queries
Ghostie avatar gains a glasses disguise option
Visualizer: Ghostie avatar gains a disguise (glasses) option
Pass IP ranges directly in GNQL queries
GNQL: IP-range syntax in queries is now parsed into CIDR ORs, so users can pass IP ranges directly without manual conversion
Workspace Stats counts now display inline with bars
Visualizer: Workspace Stats sidebar refactored so count numbers display inline with bars
Feb 4, 2026
Non-admins can now update sensor outbound and access settings
Sensor Service: non-admin users can now update sensor outbound and sensor access settings — permission scope broadened from the prior admin-only model to match how teams actually operate sensors
Feb 2, 2026
Alerts backend rebuilt with encrypted webhook headers
Alerts platform: backend rebuild — a dedicated alert-operations service with encrypted webhook headers, alert and delivery logging moved behind an API client, and the legacy alert storage retired
New session-received observation type with persistent observations
Spike detection: a session-received observation type and feed event added end-to-end, plus a delete endpoint and observations that persist between runs
Refreshed trending tags content in Block
Block: trending tags content refreshed
Tag-spike lookups gain partial match and benign/threat counts
Spike detection: partial-match support for tag-spike lookups and the tag-name field, and vendor CVE spike events now carry benign/threat counts for downstream classification context
Workspace-isolated tag service with edit history now live
Workspace Tag Service v2: backend cutover landed — workspace-isolated tag schema, per-user ownership, tag revisions for edit history, and full CRUD; the substrate under the customer-managed-tags experience that shipped in November
Jan 30, 2026
Compare moves to the investigation surfaces and goes mobile-responsive
Compare: moved from /query/compare to /observe/compare to live alongside the rest of the investigation surfaces, with a mobile-responsive fix for the workspace selectors
Design and use a custom Ghostie as your avatar
Visualizer: Ghostie Avatars — customers can design and use a custom Ghostie as their user avatar, with access controls and a 'Download Ghostie as PNG' option
Recall visualizer added to the experiments page
Visualizer: Recall visualizer added to the experiments page
Same-week tags for Ivanti EPMM and Vite KEV, plus new CVE coverage
Detection content: same-week tags for the second Ivanti EPMM 2026 CVE and the KEV-flagged Vite CVE-2025-31125; new tags for CVE-2026-1281 and CVE-2026-23760; historical-CVE backfill batch and an additional protocol-tags batch
Jan 29, 2026
New botnet tag category surfaced in the UI
Visualizer: new 'botnet' tag category surfaced in the UI
New RondoDox botnet tag, two CVE tags, and a tag-naming cleanup
Detection content: new tag for the RondoDox botnet, CVE tags for CVE-2025-68645 and CVE-2021-4039, and a tag-cleanup pass that renames tags that should have carried a CVE
Jan 28, 2026
Unique IP Addresses card stays visible with an idle state
Compare: idle/empty state added to the Unique IP Addresses card, which is now always visible
Jan 27, 2026
Autocomplete no longer overwrites your full Compare query
Compare: autocomplete selection no longer replaces the entire query on the Compare page
GNQL Production workspace renamed to Global Observation Grid
Compare: the legacy 'GNQL Production' workspace is now named 'Global Observation Grid (GOG)' across the workspace dropdowns, customers with Data Reach entitlement can access GOG without explicit membership, dynamic workspace names replace the hard-coded 'Production only' label, and the IP Distribution card shows spinning loaders instead of misleading zeros while jobs are still running
IP export no longer fails with a 400 error
Compare: export-IPs 400 error fixed by reducing page size
Jan 26, 2026
Sessions timeseries view now supports nested items
Visualizer: Sessions timeseries view gains nested-items support
Tag substring search no longer returns duplicates
Tag Service: substring search no longer returns the same tag multiple times
Jan 23, 2026
New Compare page lets customers stack two workspaces side-by-side and see exactly how they differ — classification breakdowns, tag distributions, unique IPs, and unique values. An async engine scales unique-IP comparison past the previous 1,000-IP cap. Launches alongside the renamed Global Observation Grid (GOG) workspace, answering 'what do I see that the global grid doesn't?' directly in product.
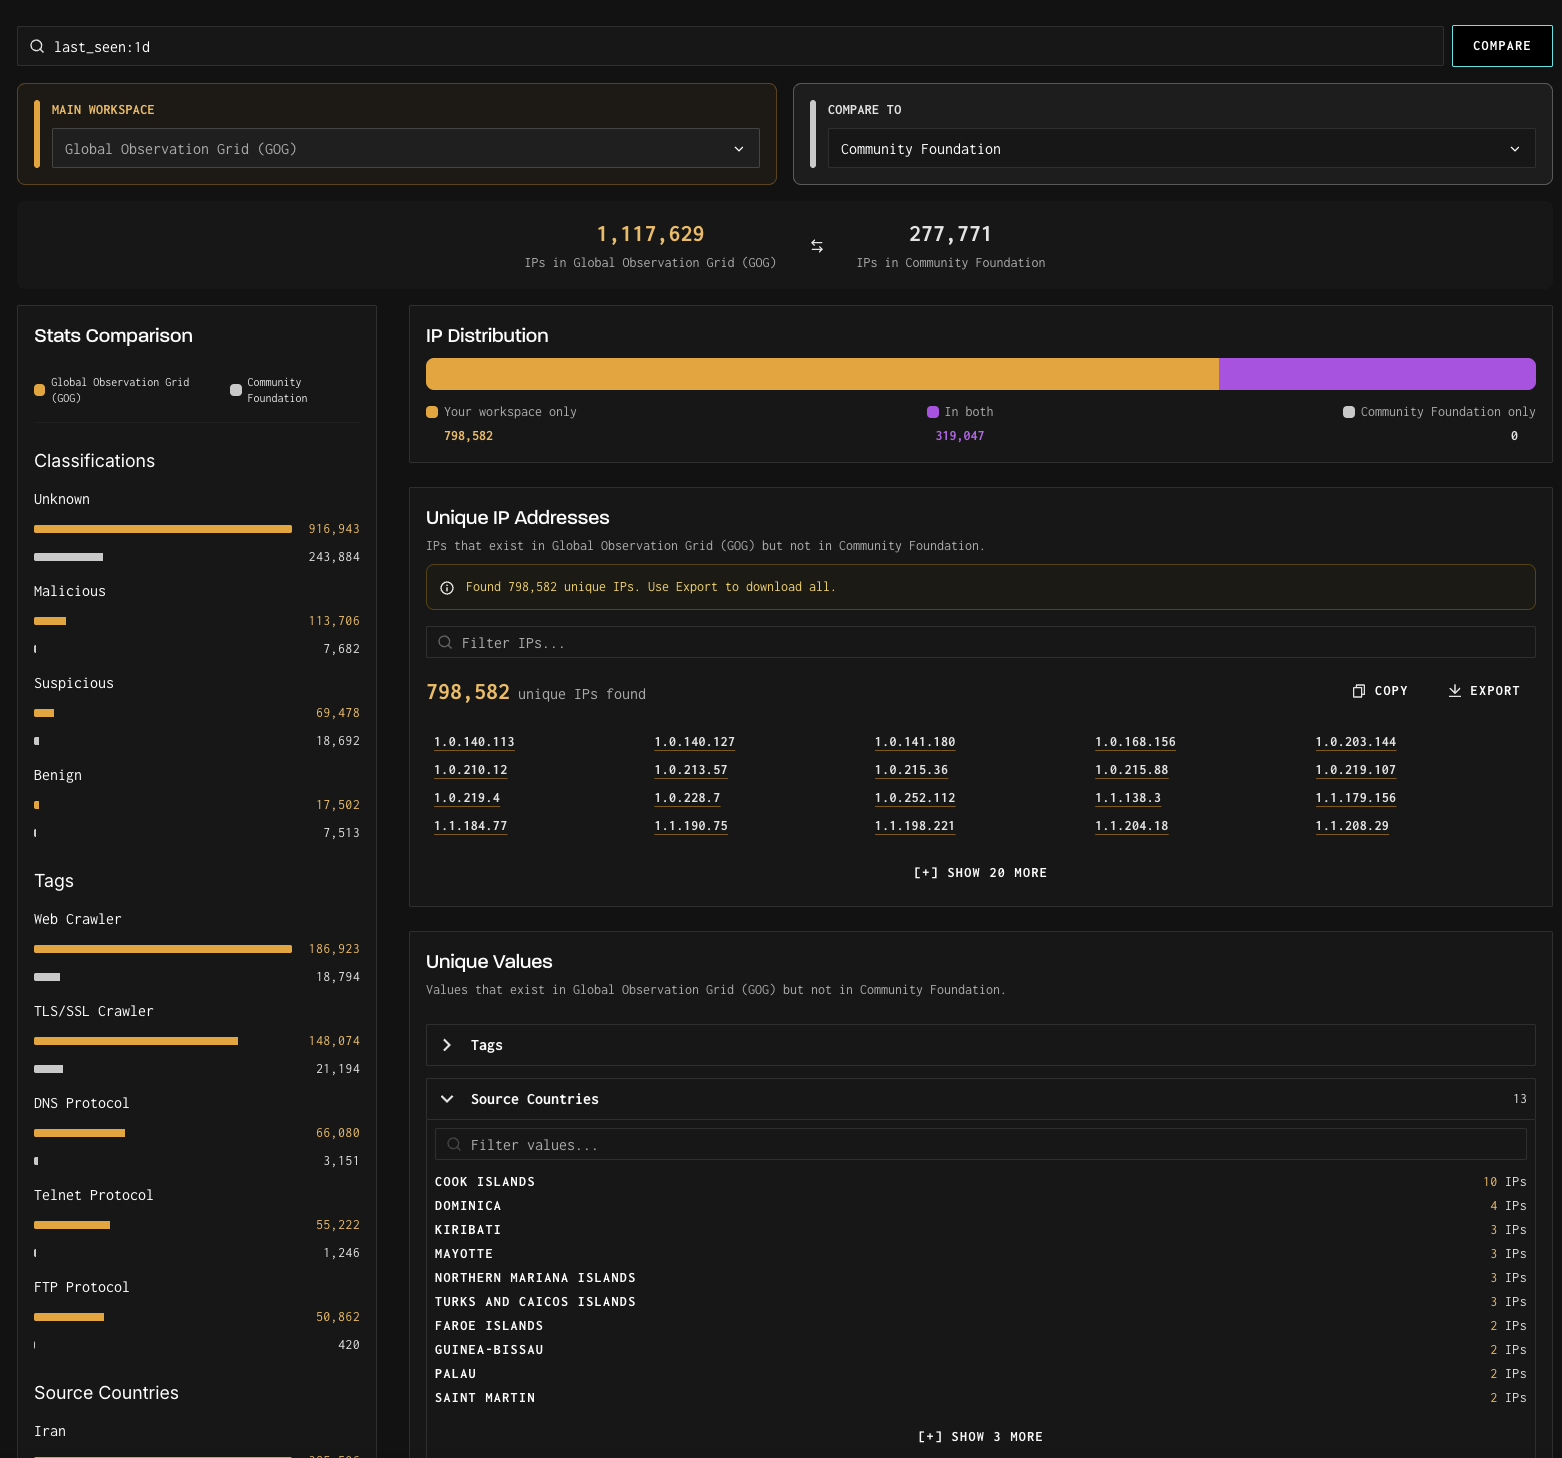
Recall queries can now be scoped to your workspace
Recall: workspace-scoped time-series queries landed end-to-end — the foundation under workspace-scoped Recall queries for customers
Jan 22, 2026
New translator endpoint that turns plain-English questions into valid GNQL queries, with multi-model support beyond OpenAI. This is the customer-facing surface of the GreyNoise AI agent stood up in December and the foundation under the Charlotte AI natural-language search story — analysts will be able to type something like 'show me Cobalt Strike activity from the last 24 hours in Brazil' and get back a GreyNoise query, results, and context without ever learning the query language.
Backend support for customer-controllable sensor egress
GN API: backend support for enabling sensor outbound traffic, mapping each sensor access level (none, LAN, internet, all) onto the persona outbound model — the backend half of customer-controllable sensor egress
Download a single session PCAP from the API
Session Service: single-session PCAP export endpoint — public API path to download a per-session PCAP from Recall data, paired with the in-product PCAP viewer shipped in December
New CVE, Nuclei, and WordPress scanner detection tags added
Detection content: VulnCheck Suricata-rules batch, additional Nuclei-based tag batch, generic WordPress plugin scanner tag, and new CVE tags for CVE-2026-21962 and CVE-2026-20045
New feed types available in the Feeds experience
Visualizer: new feed types added to the Feeds experience
Opt out of community signal sharing per workspace
Community GNQL sync: a separate sync agent and dataset for the community-shareable signal, with a per-workspace opt-out cached and refreshed every 24 hours — sets up a distinct community dataset alongside paid Recall data inside one stack
Set per-conversation message limits for the Charlotte AI agent
AI agent: optional per-conversation message limits for the Charlotte AI agent
Jan 21, 2026
Alert-schedule form validations restored
Visualizer: alert-schedule form validations restored
Faster app startup and workspace switching
Visualizer: smoother app initialization and workspace switching — initialization plugins for entitlements and user, and middleware triggered on workspace change
Workspace Compare scales unique-IP diffs to hundreds of thousands
GNQL Query Service: new async job manager for unique-IP diffs collects hundreds of thousands of unique IPs across two workspaces, streams partial results with a progress bar, and removes the previous 1,000-IP cap — the backend that makes Workspace Compare's Unique IPs experience usable at scale
Jan 20, 2026
Export entitlements now visible in the UI
Visualizer: Export entitlements now surfaced in the UI
IP Sim retired from the Visualizer
Visualizer: IP Sim removed, along with the chart components it was the last consumer of
Jan 16, 2026
Redis, WSUS, and sensitive-file-access detection tags refreshed
Detection content: Redis Scanner tag renamed to Redis Protocol with added rules, WSUS tag nocase matching, a generic sensitive-file-access-attempts tag, and a Nuclei-template-generated tags batch
Jan 15, 2026
New ASUS, Synology, and CVE-2025-64155 detection tags
Detection content: ASUS RT-AX55 authenticated RCE CVE-2023 tag, Synology test.cgi auth scanner tag, and CVE-2025-64155 promoted from silent to a full production tag
Jan 14, 2026
Download the current Sessions graph as JSON or CSV
Visualizer: one-click download of the current Sessions graph as JSON or CSV
Experimental GNQL endpoint matches main query handling
GNQL Query Service: the experimental endpoint now applies the same original-query/adjusted-query handling as the main path
Jan 13, 2026
New n8n CVE, apikeys.txt, and IoT login detection tags
Detection content: same-week tag for n8n unauthenticated file-access CVE-2026, apikeys.txt scanner tag, and updated generic IoT logins tag
Sessions table UI improvements
Visualizer: Sessions table UI improvements
Tags now load from the dedicated Tag Service
Visualizer: tags list now loads from the dedicated Tag Service rather than the legacy /v2/*********** path, with the new endpoint also used for tag enrichment
Jan 12, 2026
Block links and pricing prompts now use sales-led copy
Block: self-service copy replaced with sales-led language across links and pricing prompts
Logged-in users no longer hit the auth-required page
Visualizer: the confusing /auth-required page is no longer shown to already-logged-in users
New OpenFlow and N-Able tags plus crawler over-match fix
Detection content: new OpenFlow tag, N-Able tag promoted from silent to the CVE bucket (with duplicate removed), Ollama crawler over-matching fix, and a CVE-2023-41345 reference added
New protocol tag category surfaced in the UI
Visualizer: new 'protocol' tag category surfaced in the UI alongside its server route and TagIcon
Removed a duplicate Next button from Transporter Setup
Visualizer: extra Next button removed from the Transporter Setup flow
Jan 9, 2026
New streams view inside Sessions surfaces raw per-frame payloads directly in the Visualizer, bringing Wireshark-style payload inspection inside the product. Pairs with December's in-product PCAP viewer to close the gap between 'I see suspicious traffic in my sensor data' and 'I am reading the bytes' — no exporting, no third-party tool.
Session chips now link through to the source IP
Visualizer: SessionChip now links through to the source IP, and Observe nav items rearranged for the new layout
Jan 8, 2026
Clear alert now shown when authentication fails
Visualizer: explicit auth-error alert surfaced when authentication fails
Fixed remote-access detection in the sensor agent
Sensor agent: fixed remote-access service detection
Same-week tag for Cisco KEV CVE-2025-20393 and more
Detection content: same-week tag for Cisco KEV-flagged CVE-2025-20393, plus tags for the Ivanti LANDesk Remote Control scanner, Hikvision SDK/webLanguage scanner, new cmplatform and cryptominer scanning families, CVE-2025-14879, and a previously-silent scanner tag promoted to full production
URLs and indicators in analysis text are now defanged
Visualizer: URLs and indicators in analysis text are now defanged before display
Jan 7, 2026
Confetti when a profile is assigned to a sensor
Visualizer: confetti animation when a profile is assigned to a sensor
Jan 6, 2026
CVE queries in GNQL are now case-insensitive
GNQL Query Service: CVE queries are now case-insensitive
Fixed Block redirect behavior
Block: redirect-behavior fix
Fixed Sessions query autocomplete in the Visualizer
Visualizer: Sessions query autocomplete fixes
New Ivanti VTM and Palo Alto GlobalProtect tags
Detection content: new tags for the Ivanti VTM scanner, the classic Palo Alto GlobalProtect CVE-2019-1579, D-Link CVE-2026-0625, a PRELOGIN protocol rule, and an updated MCP/SSE-endpoint scanning tag
Jan 5, 2026
Block download timeout extended to four minutes
Block: download timeout extended to 4 minutes after large-file downloads were hitting the backend write timeout
Special characters in GNQL string values now escape correctly
GNQL Query Service: special characters inside string values are now properly escaped in the query string
Dec 23, 2025
First-time users accept an EULA before entering the product
Visualizer: first-time users now see an EULA acceptance step before entering the product
Quoted-keyword escaping fix corrects Visualizer results
GNQL Service: special characters inside quoted keywords are now properly escaped — fixes a class of incorrect Visualizer results
Dec 22, 2025
Blocklist downloads no longer catch files mid-write
Blocklist downloads: stored files are now versioned instead of overwritten in place, so customers no longer download a file mid-write
Same-week tags for HPE OneView and Fortinet flaws
Detection content: same-week tags for HPE OneView and Fortinet (Dec 2025) vulnerabilities
Dec 19, 2025
Compare workspace stats with a new stats-diff viewer
GNQL Query Service: stats-diffing between workspaces — API endpoint plus a stats-diff viewer page, extending the workspace-diff workflow from earlier in the month
Coverage for a related cluster of three November CVEs
Detection content: CVEs 2025-61675, 2025-61678, 2025-66039 covered as a related cluster
New Intel AMT scanner and exploitation tag
Detection content: Intel AMT scanner and vulnerability-exploitation tag
Refined OVA Profiles upload flow
Visualizer: OVA Profiles upload UI — follow-on improvements to the initial upload flow shipped the prior day
Send a real test payload to validate alert webhooks
Alerts: test webhook button — Visualizer button + API route that sends a real test alert payload to a configured webhook so customers can validate integrations before they fire for real
Session detail view auto-retries a failed initial fetch
Visualizer: Session detail view auto-retries on a failed initial fetch instead of showing an empty state
Suricata protocol-tag detection family now complete
Detection content: Suricata protocol-tag expansion completes (initial set Dec 3, remaining set Dec 19) — a new family of protocol-based detections distinct from CVE and actor tags
Toggle labels on dense Session Connections graphs
Visualizer: Session Connections graph gains a label-toggle for dense sessions where labels become unreadable
Dec 18, 2025
Alert links now work with special characters in queries
Alerts: query string is now URL-encoded when building alert links, so complex queries with special characters produce working pivots
Alerts page is now available to every user
Visualizer: alerts page and navigation no longer entitlement-gated — every user can reach the alerts experience
Fixed overlapping overlays in Session Explorer
Visualizer: cluster of z-index fixes across the sticky header, Session column-header menu, and other Session Explorer overlays
New VulnCheck and research-session detection tags
Detection content: VulnCheck mid-December batch + priority-queue research-session tags
RIOT stat replaced with a Business Service badge
Visualizer: RIOT stat in analysis view replaced with a badge, consistent with the new Business Service framing
Sensor bootstrap endpoint now checks entitlement
Sensor bootstrap endpoint is now entitlement-checked, in line with sensor creation
Enrichment accuracy improved across all workspaces
Enrichment now applies consistently across every workspace rather than production only — materially improving enrichment accuracy for all customer workspaces
Sensors and Profiles pages link directly into Explore
Visualizer: Sensors and Profiles pages now link directly into Explore for quick pivots
Time-axis intervals now show seconds or minutes as needed
Visualizer: time-axis intervals now choose seconds or minutes conditionally instead of always showing both
Upload OVA Profiles with backend image validation
Visualizer: initial OVA Profiles upload UI, paired with backend OVA-image validation in the Sensor Service
Dec 17, 2025
Blocklists now sorted by most recently updated
Blocklists: list now sorted by most-recently-updated so customers see what they actually touched last
Improved Transporter image rendering
Visualizer: UX improvements to Transporter image rendering
Metered endpoints now check allowance before counting usage
API: metered entitlement check ordering corrected across all metered endpoints — usage was being reported before the allowance was checked, leading to over-counting and incorrect throttling
More accurate Cisco SSL VPN brute-force block queries
Block: query-templates refinement, including more accurate Cisco SSL VPN brute-force queries
New tags and tags-over-time GNQL aggregations
GNQL Query Service: new `tags` endpoint and `tags-over-time` aggregation, with a 'Tags Over Time' sandbox view
New /v3/gnql/stats endpoint returns GNQL query stats
API: new `/v3/gnql/stats` public route surfacing the new GNQL Query Service stats capability
Recall service documentation now available in production
API: customer-facing Recall service documentation promoted to production
RIOT renamed to Business Service across the product
Visualizer: in-product 'RIOT' rebrand to 'Business Service' across the customer-facing experience
Sensor health now surfaced on update responses
Visualizer: sensor health now surfaced on update responses, plus follow-on PCAP viewer improvements
Dec 16, 2025
Customers can now open raw session packet capture directly inside the Visualizer — no exporting, no downloading, no jumping to Wireshark for the routine case. A first-class in-product PCAP surface for the Session Explorer, paired with sensor-status surfacing on update so users see the full picture of what a sensor is doing while they're inspecting its traffic.
Entitlement changes now propagate to customers faster
Entitlement Service: cache TTL reduced to 1 minute so entitlement changes propagate to customers faster
New tags for CVE-2025-8489 and CVE-2020-27866
Detection content: same-week tag for CVE-2025-8489 and a VulnCheck tag for CVE-2020-27866
Refreshed Visualizer top navigation
Visualizer: top navigation refresh — sets up the redesigned global navigation surface
Saving a blocklist now automatically rebuilds its query
GNQL Blocklist: creating or updating a blocklist now automatically triggers a build for that query hash
Smoother onboarding for users created before the new provisioning flow
Auth0 provisioning: distinguishes users created before vs. after the new provisioning flow — adds metadata and an updated expired-plan modal so customers no longer land on the wrong onboarding screen
Dec 15, 2025
Blocklist counts now accurately reflect non-RIOT IPs
GNQL Blocklist: RIOT filtering now happens before the size-limit cap, so returned counts accurately reflect non-RIOT IPs
Dec 12, 2025
Sensor and Profile pages now show clear error states
Visualizer: Sensor and Profile pages now show proper error states instead of blank views on failure
User preferences now save across the Visualizer
Visualizer: first user-preferences surface — backend endpoints in the GN API plus Visualizer wiring that consumes them
Dec 11, 2025
Better handling of malformed GNQL requests
GNQL Service: better handling of malformed GNQL requests
New tags for three CVEs and ScadaBR added same week
Detection content: same-week tags for CVE-2025-44823/4 and CVE-2025-64328; ScadaBR detection tag
Trends can now exclude protocol-based tags from scoring
Visualizer: Trends can now exclude protocol-based tags from scoring — Labs request after the protocol-tag rollout started crowding top-10 lists
Dec 10, 2025
Every GNQL query a customer runs — through the Visualizer, Block, Alerts, the public API, or any integration — now flows through GreyNoise's purpose-built query engine instead of the legacy monolith path it lived on for years. The cutover unlocks new public surfaces immediately: `tags`, `tags-over-time`, workspace stats-diff, tag-alias lookup, and a public `/v3/gnql/stats` route all ship the same month. The most consequential backend change GreyNoise shipped in 2025.
CSV and JSON exports now counted correctly for billing
GN API: `format=csv` and `format=json` query parameters now correctly recognized as export operations for billing and throttling
Manage hardware profiles via full CRUD API support
GN API: full create/read/update/delete support for hardware profiles, matching the underlying Sensor Service work
Multi-term Sessions searches now default to AND
Visualizer: Sessions queries now default to the AND operator, matching what users expect from multi-term searches
New CVE tag, actor IP refresh, and Nuclei rules shipped
Detection content: CVE-2022-40475 tag, AHREF actor tag IP refresh, Nuclei template rules drop
RIOT V2 web rule creation fixes and SSL options
RIOT V2: web-interface rule-creation fixes — schema validation errors resolved, rule URLs allowed, SSL options added
Dec 9, 2025
GNQL tag responses now include the latest slug
GNQL query service: tag responses now include the latest slug
New mobile nav matches the redesigned top nav
Visualizer: new Mobile Nav component aligned with the redesigned top nav
Profile Sensors card now refreshes after updates
Visualizer: Profile Sensors Card now refetches after an update so it reflects current state
Same-week tags added for two more CVEs
Detection content: same-week tags for CVE-2025-11749 and a CVE-2022-2290 tag
See sensor health directly in the Visualizer
Visualizer: new sensor-health views in product, driven by the canonical UserReasons backend work
Dec 8, 2025
Feeds drawer chart now matches the sparkline range
Visualizer: Feeds drawer chart now uses a 30-day range, matching the sparkline above it
Fixed percentage rendering on the SessionGraph timeseries
Visualizer: percentage rendering fix on the SessionGraph timeseries item
Dec 5, 2025
Improved Sensors table UX in the Visualizer
Visualizer: Sensors table UX improvements
New GNQL /stats endpoint with timestamp range filter
GNQL query service: `/stats` endpoint mirroring API behavior, integrated through the GN API handler with a timestamp range filter
New WSDL injection, React2shell, and benign-actor tags
Detection content: WSDL injection silent tag, OAST interaction-domain tag refresh, React2shell tag with CVE id, and Root Evidence benign-actor tag
Refreshed Block landing page with a new template
Block: landing-page updates with a new React template
Same-week silent tag added for CVE-2025-55182
Detection content: same-week silent tag for CVE-2025-55182 (with two same-day refinements)
Tag aliases now resolve to the canonical tag in GNQL
GNQL query service: tag-alias lookup so requests using a tag alias resolve to the canonical tag
VulnCheck-derived rules now carry a reference source
Detection content: all VulnCheck-derived rules now carry a reference-source field, improving auditability
Dec 4, 2025
Fixed alert reporting interaction with throttling
Alerts: fix for how the reporting path interacts with plan throttling
Fixed GNQL quoted-string and OR-operator parsing
GNQL Service: quoted-string parsing no longer leaves quotation marks on keyword fields, and OR operators now properly wrapped in parentheses — resolves a regression around quoted wildcards same-day
New tag search endpoint in the GN API
GN API: new `tag search` endpoint
Same-week and research-derived tags added for three CVEs
Detection content: same-week tag for CVE-2025-63207; research-derived tag for CVE-2023-45826; VulnCheck tag for CVE-2024-24578
Same-week tag added for React-ecosystem CVE-2025-64459
Detection content: same-week tag for the December React-ecosystem CVE (CVE-2025-64459), with a follow-up VulnCheck-backed tag
Validate uploaded OVA sensor images
OVA validation: backend support for validating uploaded OVA images — paired with the Visualizer OVA Profiles upload UI shipped Dec 18
Dec 3, 2025
GreyNoise's Anomali ThreatStream integration gains vulnerability enrichment alongside a full v3 API update. Joint customers with Investigate, Hunt, or VPI data modules can now enrich CVEs directly in ThreatStream with GreyNoise exploitation-activity context. IP enrichment is updated to the v3 API for all joint customers, surfacing new fields, and a broken IP Timeline view was rebuilt. Driven directly by customer feedback.
Session timeseries chart shows percentage alongside counts
Visualizer: Session timeseries chart now shows percentage of total alongside absolute counts
Sessions graph items are now searchable
Visualizer: Sessions graph items are now searchable
Suricata midstream session pickups improve coverage
Suricata: midstream session pickups now enabled, broadening coverage of long-running sessions
Dec 2, 2025
Sensor map UX improvements
Visualizer: Sensor map UX improvements
Timeseries API now runs entirely on the rebuilt Recall service
API: cutover from the legacy timeseries service to the rebuilt timeseries backend — every customer timeseries call now runs against the rebuilt service, completing the customer-facing rollout that started with the fall Time Series API redesign
Dec 1, 2025
Customers can now upload their own OVA virtual-machine images and turn them into sensor personas. Instead of choosing from GreyNoise's fixed catalog, they bring the exact operating systems and services that match their real environment — and sensors impersonate them. Closes the loop on the bespoke-deception story Spacewar has been building toward.
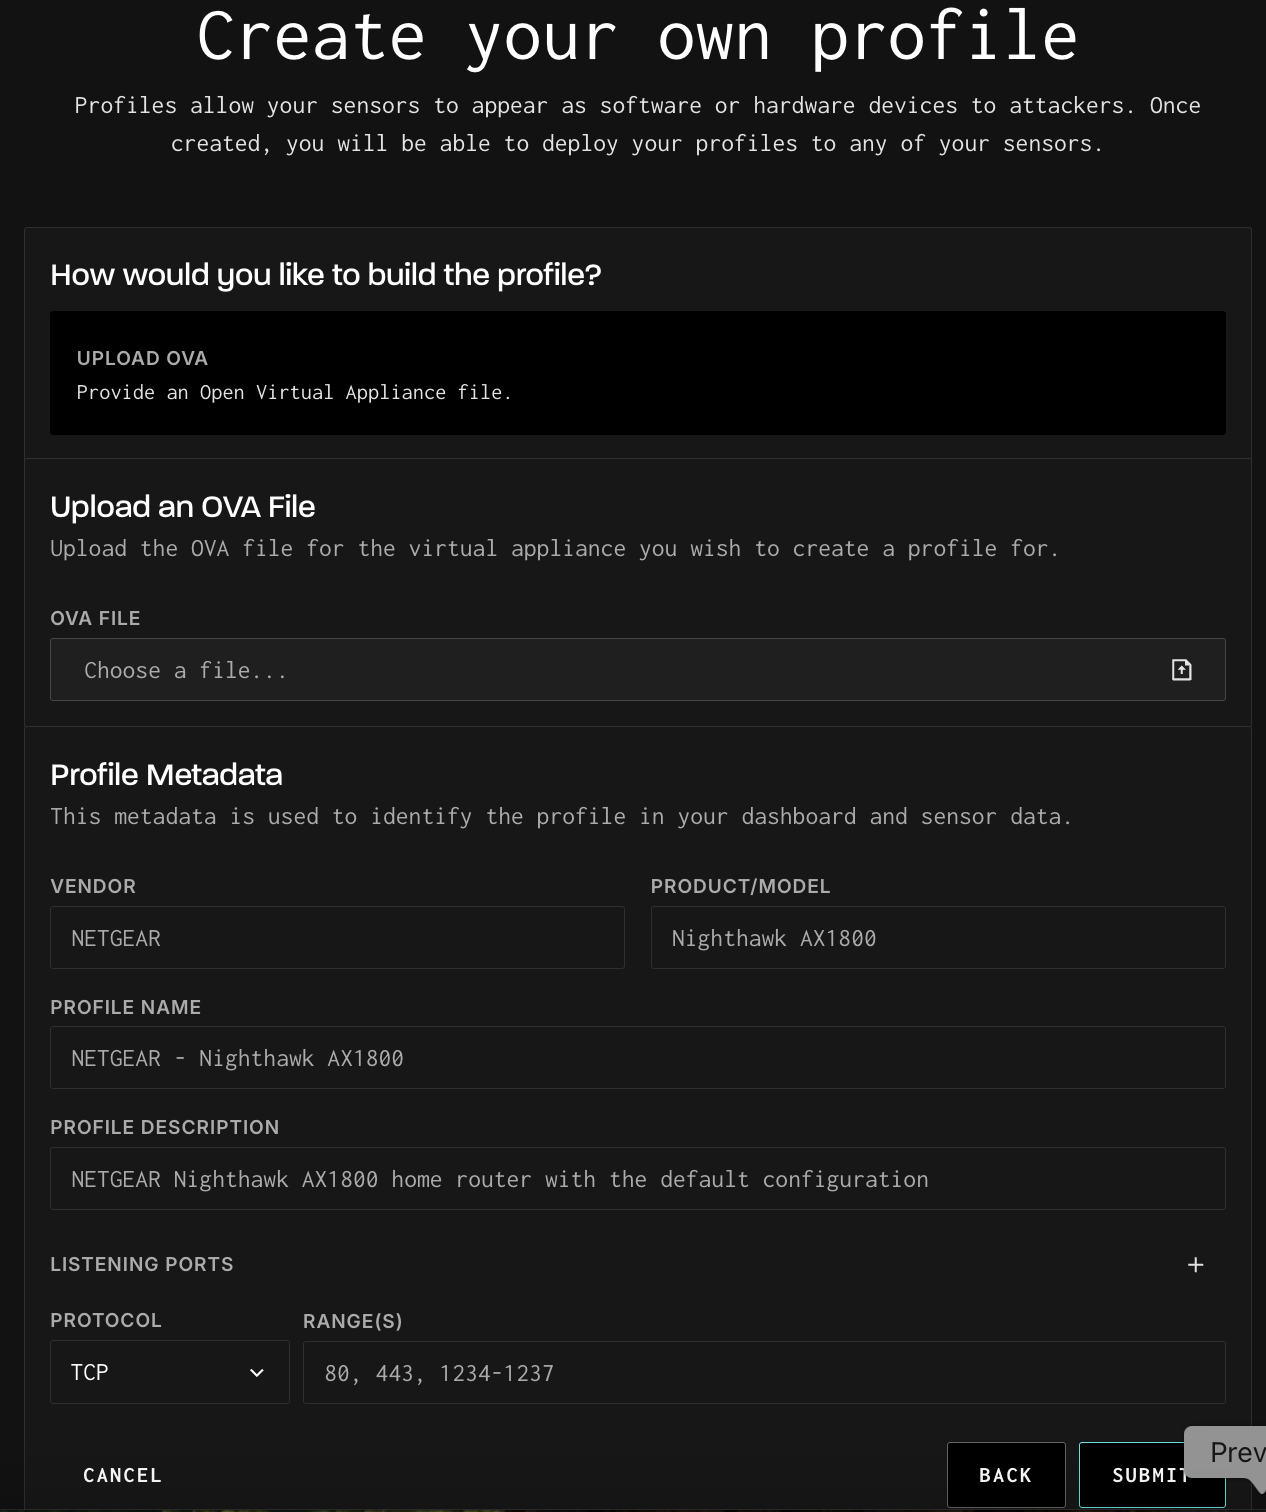
Block excludes benign RIOT scanner IPs by default
Block: RIOT (benign-scanner) IPs now excluded by default so customers don't block legitimate scanners
Historic data reach entitlement now enforced on session endpoints
Visualizer + API: historic data reach entitlement now enforced on session endpoints client-side and API-side, pairing with the broader Historic Data Reach feature
Sensor table column set refreshed
Visualizer: Sensor table column set refreshed
Session Explorer gains sticky query bar and keybinding fixes
Visualizer: Session Explorer cluster of UX improvements — sticky query bar, keybinding fixes, search reset, page-URL param removal from session links, and home/end key fixes on the sessions query
Nov 24, 2025
Every sensor that comes online from this point forward runs GreyNoise's own Rust agent on the box by default — no opt-in, no separate provisioning path. The sensor service serves the agent bootstrap automatically and installs it on every newly-provisioned instance. The payoff of a multi-month program, opening the door to on-sensor enrichment, on-sensor detection, and deeper hardware-sensor experiences ahead.
GNQL field-mapping fixes for cities and sensor ASNs
GN API: GNQL field-mapping fixes for cities and sensor ASNs plus a source-field exclusion bug fix
Same-week tags for November KEV wave RCEs
Detection content — November KEV wave: same-week tags for Fortinet FortiWeb OS command-injection RCE (CVE-2025-58034) and Oracle Identity Manager takeover RCE (CVE-2025-61757), plus VulnCheck tags for Flowise auth-bypass RCE (CVE-2025-8943) and Metro Development Server RCE (CVE-2025-11953)
Webhook headers now encrypted at rest across Alerts and Feeds
Alerts and Feeds: webhook headers are now encrypted at rest across every delivery service
Nov 21, 2025
Choose the time interval on Session Explorer timeseries
Session Explorer: time-interval radio group on the timeseries with interval propagated across explore/graph/multi pages and the timeseries API endpoint
Session Explorer adds query tips and a redesigned Help drawer
Session Explorer: query-autocomplete tips section and a redesigned Help drawer with Fields / Query Patterns tabs
Session queries auto-normalize Lucene syntax server-side
Session Explorer: server-side Lucene query formatting helper (normalizes case, replaces `==` with `:`, escapes special characters) applied to all session endpoints that accept a query
Specify a custom Transporter image during setup
Visualizer: custom Transporter image setup — form in the Transporter setup component to specify a custom image, with the image endpoint updated server-side to support it
Transporter setup auto-selects your OS for instructions
Visualizer: user OS now stored in userStore so Transporter setup instructions auto-select the right OS across components
Nov 20, 2025
Recall timeseries stats endpoint live with clearer GNQL errors
Recall: timeseries stats endpoint live in the standalone service, with GNQL parser cleanup so API users see clean syntax-error messages
Reworked auth-required redirect flow in the Visualizer
Visualizer: auth-required redirect flow reworked — 401 now thrown when no redirect provided, /auth-required page removed, docs redirect and workspace-invite flows tightened
Nov 19, 2025
Fixed IP classification selection in the Feeds form
Visualizer: Feeds form classification dropdown fix where IP classification selection was misbehaving
Friendlier session column names in Session Explorer
Session Explorer: server-side field label/description map for friendlier column names (Src/Dest expansions, Cnt → Count, refreshed tag and metadata labels)
Profile-creation errors now surface inline in the form
Visualizer: Profile-creation errors now surfaced inline in the form instead of collapsed into a generic message; added unit tests for ProfileForm
Redesigned Query page top bar with CVE search in the sidebar
Visualizer: Query page top-bar redesign — query and action buttons in the top bar, CVE search moved to the sidebar, NEW badge added to the Blocklist button
Sensor selection clears after a mass action completes
Visualizer: clear sensor selection after a mass action completes so users don't accidentally re-apply it to the same set
Nov 18, 2025
Filter sensors by health status
Sensors can now be filtered by health status
Nov 17, 2025
Blocklist creation now enforces remaining capacity limits
Block: entitlement enforcement on blocklist creation — checks remaining capacity against the plan limit and blocks creation when zero
Retrohunt IP results are now scoped to a workspace
Retrohunt: workspace-scoped IP results endpoint, filterable by workspace, with the retrohunt-creation handler accepting a workspace parameter
RIOT V2 stats endpoint for data introspection
RIOT V2: stats endpoint on management and consumption services for RIOT data introspection
Nov 14, 2025
Dismissed Transporter banner now stays dismissed
Visualizer: Transporter banner dismissal now persisted in session settings so it stays dismissed
New Session Explorer combines session panels in one view
Session Explorer: new multi-view page combining several session panels with a compact display mode and a cached fetch helper to reduce calls
Same-week KEV tags for Triofox and FortiWeb flaws
Detection content: same-week KEV tags for Gladinet Triofox improper access control (CVE-2025-12480) and Fortinet FortiWeb auth bypass (CVE-2025-64446)
Sensor search on profile assignment returns the right sensors
Visualizer: sensor-search filtering on profile assignment now returns the right candidate sensors
Nov 13, 2025
Block user guide now includes a walkthrough video
Block: walkthrough video embedded in the public Block user-guide docs
Export full PCAP and raw packets from a session row
Session Explorer: session packet export — download buttons in the expanded session row for full PCAP and raw source/destination packets, with proper content-disposition filename
New tags for XWiki LFI and a VulnCheck batch
Detection content: new tag for XWiki Platform path-traversal LFI (CVE-2025-55748) plus a VulnCheck batch covering Burk ARC Solo, Seeyon OA cookie leak, Linksys E1700 command injection, Anheng Mingyu Audit SSRF, and others
Sensor health is now available through the API
GN API: sensor `health` field surfaced on the Sensor model so external API consumers can filter and read sensor health
Sensors list now prompts you to set up hardware profiles
Visualizer: Transporter CTA banner on the Sensors list directing users to set up hardware profiles
Nov 12, 2025
Hide the Sensors map and act on sensors from the table
Visualizer: hide-Sensors-map toggle with mass actions surfaced through the table when the map is hidden, and Sensor ID promoted to the primary column
Tokenized blocklist URLs now appear in your account page
Block: tokenized blocklist URLs surfaced in the Visualizer Account → Blocklists page, with non-tokenized URLs kept available alongside for integrations that need them
Nov 11, 2025
New detection coverage for Fortinet and N-able vulnerabilities
New detection coverage for Fortinet FortiSIEM file write, N-able N-central XXE, and N-able N-central authentication bypass
Nov 10, 2025
Blocklist downloads are gzip-compressed to avoid timeouts
Block: gzip compression on blocklist IP responses plus a buffered writer to protect against download timeouts
Long input values no longer break form fields
Component library: GnInput, GnDateInput, and GnTypeahead now handle long values gracefully instead of blowing out their containers
Recall timeseries truncates to one week instead of erroring
Recall: timeseries data now truncates to a one-week default range on entitlement breach instead of returning 403
Nov 7, 2025
Custom Tags is the final piece of Spacewar to land in the Visualizer. Spacewar researchers can now use Explore to find new and notable traffic, then create workspace-scoped tags to automatically track IPs sending similar traffic going forward — the same workflow GreyNoise's own detection team uses daily. With Custom Tags live, the complete Spacewar lifecycle is now available in product: Deploy Sensors → Create Profiles → Analyze Data → Create Tags → Compare to GOG.
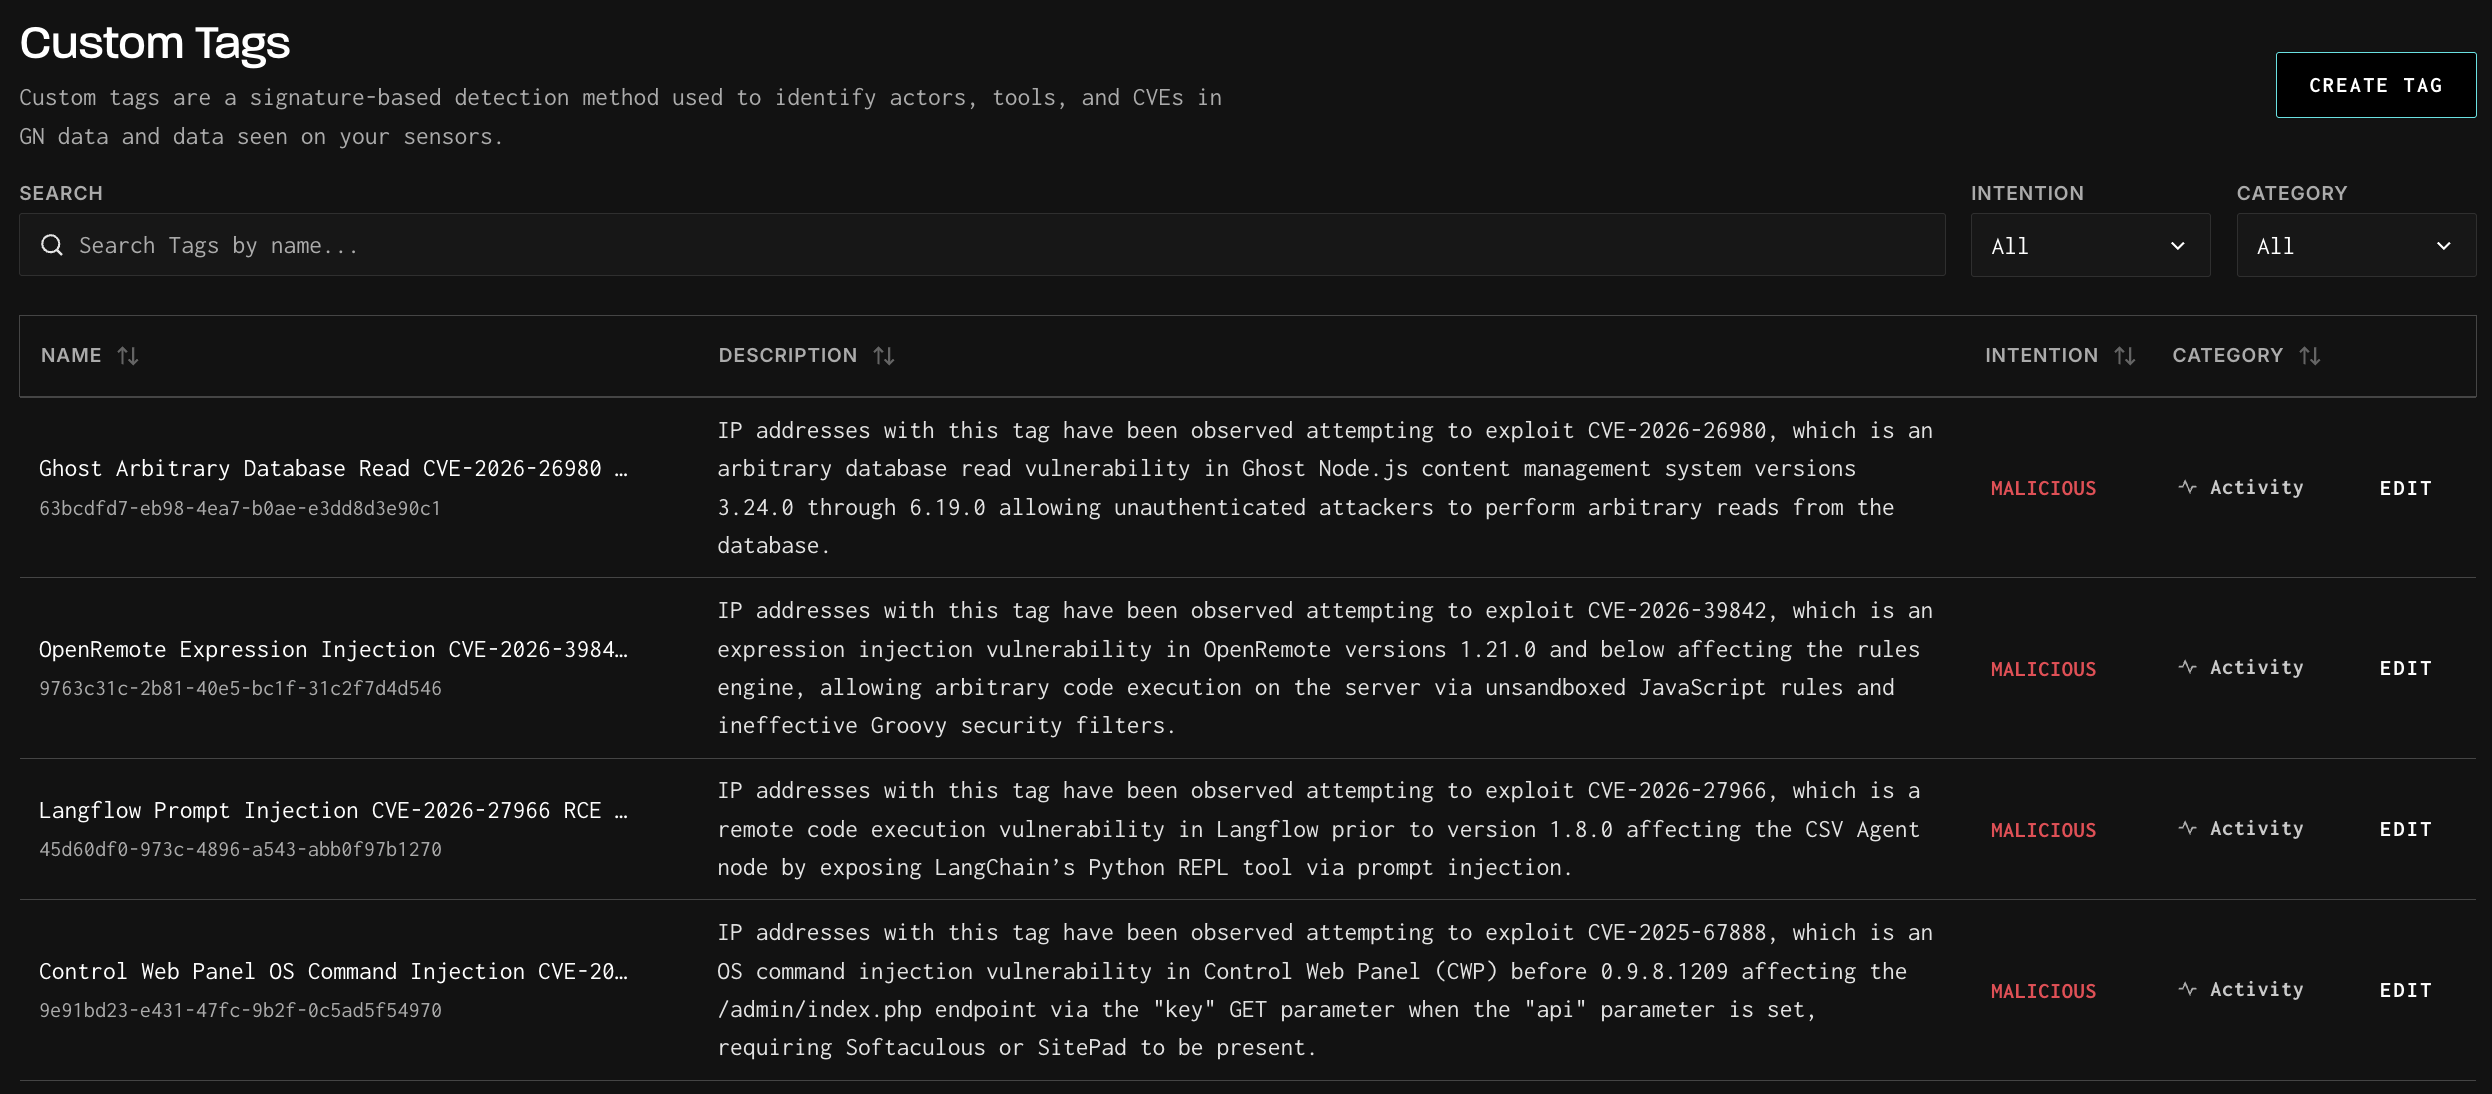
Add custom HTTP headers to alert webhooks
Alerts: custom HTTP webhook headers end-to-end — Visualizer UI for managing headers (auth tokens, custom identifiers) and matching backend storage in the alerts handler and repository
Cleaner profile cards with clearer ports and categories
Visualizer: Profile card / detail polish — categories only on the sensor page, protocols under the title, improved ports and categories display
Profiles now support multiple port types
Visualizer: ProfileForm now supports multiple port types per profile
Sensors auto-recover after cloud network resets
Sensor gateway: sensors now recover automatically from stale network state after a cloud-provider reset (reboots, transient network failures); rollout disabled by default and gated by config
Session Explorer adds a sortable counts graph view
Session Explorer: counts graph view with sorting and formatting, plus a loading state on the subfield selector
Transporter images now stream directly to you
Visualizer: Transporter image now streams directly to the user rather than returning a signed URL
Welcome page now highlights Sensors for eligible workspaces
Visualizer: Sensors card added to the signup welcome page for workspaces with sensors access
Nov 6, 2025
New Adobe Experience Manager SSRF and XML injection tags
Detection content: new Adobe Experience Manager tags for SSRF (CVE-2025-54249) and XML injection (CVE-2025-54251)
Recall timeseries fields filtered to your entitlements
Recall: timeseries response fields censored to the workspace's entitlements rather than returning 403
Session Explorer adds a force-directed connections graph
Session Explorer: force-directed connections graph view with in-component controls for maxNodes and minConnections
VulnCheck batch tags for Linksys, D-Link, and FOG flaws
Detection content: VulnCheck batch covering Belkin Linksys RE6500 (CVE-2020-35714), D-Link DNS-343 (CVE-2018-25120), FOG command injection (CVE-2024-39914), and others
Nov 4, 2025
Column header menu adds sort, filter, copy, and unique values
Session Explorer: column-header actions menu (sort, filter, copy, unique values) plus a unique-values drawer with search and copy
Session Explorer adds a treemap chart view
Session Explorer: treemap chart visualization for the session graph page with a graph-type switch and subfield selector
Nov 3, 2025
Added an interactive world map to the Sensors list page — country geographies, mass-action wiring, and a hide-map toggle that promotes Sensor ID to the primary column when the map is collapsed. Customers managing their deployments now see geographic distribution at a glance and can drive mass actions directly from the map. The first map-based visualization surface in the new Visualizer.
Create a blocklist directly from GNQL query results
Block: 'Create Blocklist' button on GNQL query results and a dedicated Blocklist Form drawer in the Visualizer — the in-app starting point for the Block product
Faster, more robust server-side caching in Block web
Block web: switched to Nuxt-native caching helpers for server-side hydration and a more robust cache implementation
Fetch blocklists via tokenized URLs without API key headers
Block: tokenized blocklist URLs end-to-end — pairs blocklist ID with API key into a tokenized URL so users no longer need to set API keys in request headers when fetching blocklists
New tags for SnowService and DelMia Apriso RCE CVEs
Detection content: new tags for SnowService API command-injection RCE (CVE-2024-11482) and DelMia Apriso code-injection RCE (CVE-2025-6204)
Oct 31, 2025
Higher rate-limit allowance for legacy-plan customers
Visualizer: rate-limit allowance increased for legacy-plan customers
Oct 30, 2025
RIOT V2 single- and multi-IP lookups now live
RIOT V2: single- and multi-IP lookup handler shipped — completes the V2 consumption pipeline
Sensor metadata now includes queryable country code
Sensor service: country_code added to sensor metadata, flattened for easy access, with a query param exposing it
Oct 29, 2025
Manage subscriptions, invoices, and cancellation in Block
Block: subscription details, invoice history, and end-to-end cancellation now live in the account UI — completes the self-serve subscription lifecycle
Oct 28, 2025
Check My IP teaser brings anonymous single-IP lookup
Visualizer: 'Check My IP' experiment — anonymous single-IP lookup as a teaser surface
CVE-2016-5674 tag extended to cover CVE-2025-1338
Workspace GNQL: CVE-2016-5674 tag extended to also cover CVE-2025-1338
Oct 27, 2025
Enterprise Platform customers can now create, manage, and deploy GNQL-powered IP blocklists directly from the Visualizer — bringing the same blocklist capability available in Block to the full depth of enterprise data. Customers with advanced data modules can use the complete GNQL field set they've purchased (JA4, raw_data.*, metadata.source_country, and more) to build precisely targeted blocklists like `metadata.source_country:Iran raw_data.http.method:POST last_seen:1d`. Blocklist quantity is tiered across Standard, Advanced, and Elite plans, and field availability maps to data module level — creating a clear upsell path for existing customers.
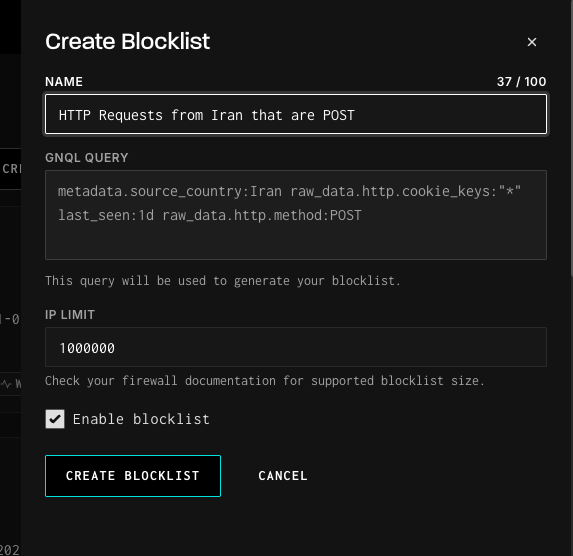
Blocklist IP cap removed and download size aligned
Block: removed the cap on number of IPs allowed during blocklist creation and aligned the download-size cap with the backend
GNQL search metering enforces configured per-plan limits
GN API: new GNQL search meter — customers without the feature get unlimited untracked searches; entitled customers are tracked and cut off at the configured limit
Manage workspace blocklists from a new account page
Enterprise Block: /account/blocklists page in the Visualizer lets workspace users enable/disable, delete, view queries, copy endpoint URLs, and download from their managed blocklists
Oct 24, 2025
Brand-new Session Explorer in the Visualizer lets analysts inspect honeypot and sensor session data directly in product. Includes a raw-data viewer with autocomplete and column selection, workspace scoping, shareable URL parameters, expanded session detail views, and a Time Series graph tab. The first customer-facing surface for raw-traffic investigation.
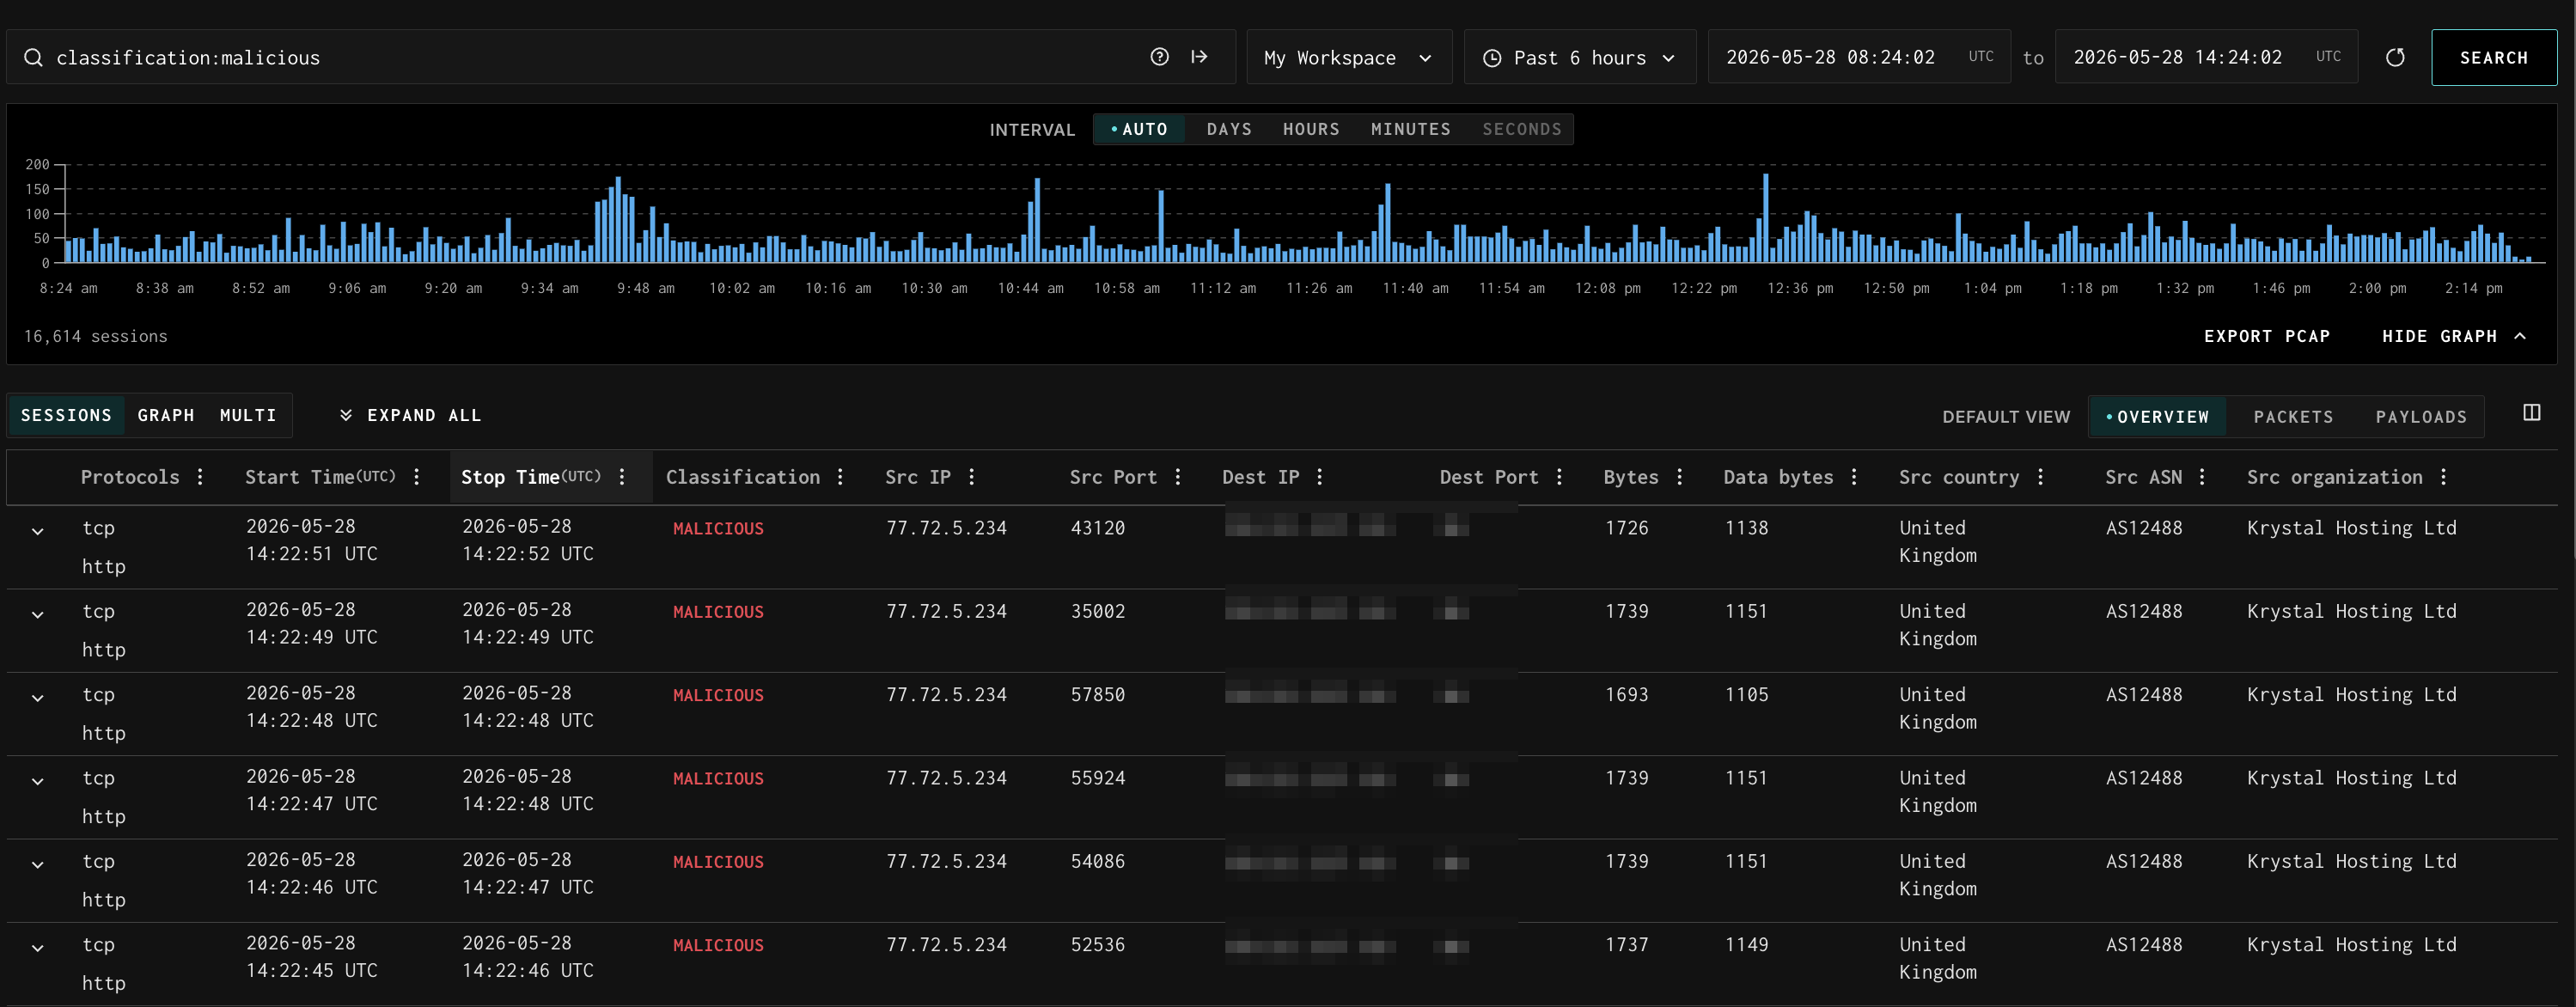
Block account page refreshed with workspace and billing surfaces
Block: Account page refreshed with the latest workspace and billing surfaces
Sensors can now capture outbound traffic
Sensor gateway: the outbound path landed end-to-end — sensors can now capture outbound traffic in addition to inbound
Trial-expiry emails now show the real expiry date
Block: trial-expiry email now reflects the actual expiry date instead of a hard-coded value
Oct 23, 2025
Blocklist queries now escape tag names correctly
Block: tag names in blocklist queries now use proper escapes instead of quotes, matching the backend's expectations
CVE-2022-1040 tag gains request-body matching for higher fidelity
Detection: CVE-2022-1040 tag extended with request-body matching for higher fidelity
New scanner tag: giftedvisitor
New tag: 'giftedvisitor' scanner
Oct 22, 2025
Block download APIs support redirect=false for clients that can't follow 30x
Block: download APIs now support redirect=false for clients (firewalls, scripts) that can't follow 30x responses
Block 'Download IPs' no longer truncates or garbles CSV
Block: CSV-data unmarshaling fixed for the 'Download IPs' button so downloads aren't truncated or garbled
Block stats bar shows 'false' instead of 'unknown'
Block: stats bar now correctly displays 'false' instead of 'unknown' (boolean-logic fix)
Cleaner sensor-persona display and update flow
Visualizer: polished sensor-persona display and the update flow around it
Faster Block providers endpoint
Block: providers endpoint performance fix
Feeds honor entitlements and auto-disable un-entitled event types
Feeds: entitlement checks added across the CVE status-change, CVE activity-spike, and IP classification-change event types — the UI disables un-entitled event types and auto-disables feeds whose entitlement was removed
GNQL response IPs now count toward your Search IP limit
GN API: GNQL response IPs now count toward the Search IP Limit meter
In-product setup instructions for the Transporter sensor
Visualizer: in-product setup instructions for the Transporter sensor component
Regenerated API keys work immediately without re-login
Block: regenerating an API key now updates the user session so the new key works immediately without re-login
Total IP count is now readable in Block light mode
Block: light-mode UI darkened slightly so total-IP-count text is readable
Oct 21, 2025
Clearer end-of-trial messaging and entitlement updates
Block: end-of-trial behavior reworked with clearer messaging and entitlement updates at trial end
First-time users always land provisioned after signup
Block: trial provisioning refactored to a POST on the signup page with an access-denied fallback, ensuring first-time users always end up provisioned
Oct 17, 2025
Copy a blocklist URL with API key in one click
Block: 'copy URL with API key' affordance on the blocklist UI
Create hardware profiles directly in the Visualizer
Visualizer: Create Profile flow — users with the sensors entitlement can create hardware profiles directly, folding the existing 'request a profile' flow into the new creation experience
New silent tag for an unusual honeypot crawler
New silent (non-emitting) tag for an unusual crawler observed in honeypot traffic, plus minor edits to neighboring tags
October detection wave adds same-week tags for major CVEs
Detection content — October wave: ~25 Nuclei-template bulk PRs, three priority-queue batches, multiple VulnCheck bulk drops, same-week tags for Cisco ASA CVE-2025-20333, Fortra GoAnywhere CVE-2025-10035, Oracle EBS CVE-2025-61882, Watchtowr's CVE-2025-36604, CVE-2025-59528, CVE-2025-58434, and CVE-2025-54381; Bruteforce tag family reclassified to malicious
Oct 16, 2025
Full Block billing automation pipeline ships: a Stripe payment event now automatically becomes a customer entitlement change with no human in the loop. The foundation under Block's self-serve revenue motion.
CVE Spike Feed now saves filter-option changes
CVE Spike Feed: UI now persists filter-option changes (previously discarded on save)
Sensor create and delete now emit entitlement and metering events
Sensor service: create and delete operations now produce entitlement and metering events so usage is tracked against customer plans
Oct 15, 2025
Brought up a new Sensor Health service from scratch over October. The foundation for surfacing sensor health to customers in the Visualizer — operators with deployed sensors will be able to see, in product, whether their sensors are healthy and producing signal.
Fixed an edge-case multi-IP query failure in Block
Block: edge-case multi-IP query failure resolved
Workspaces can update contact details and change their plan
Block API / Entitlement Service: workspaces can now update their contact details (PUT) and modify their plan behind a clean handler layer
Oct 14, 2025
Refreshed Profile Library layout in the Visualizer
Visualizer: Profile Library layout refreshed
Tag Activity gains IP-runtime field for proper CIDR filtering
Tag Activity: query gains an IP-runtime field, enabling proper CIDR filtering including BOGON range exclusion
Oct 11, 2025
Block query builder keeps the sidebar and query section in view
Block: sidebar and top query section now always visible in the query builder so users keep context as they iterate
Oct 10, 2025
Customers can now be alerted when the count of IPs matching a GNQL query over a time window crosses a configurable threshold — a long-requested capability for catching emerging exploitation spikes the moment they begin. Includes the alert delivery plumbing, monitoring configuration, and CSV-format support on the underlying endpoint. Pairs with the Time Series API to give customers both the historical data and the alerting layer on top.
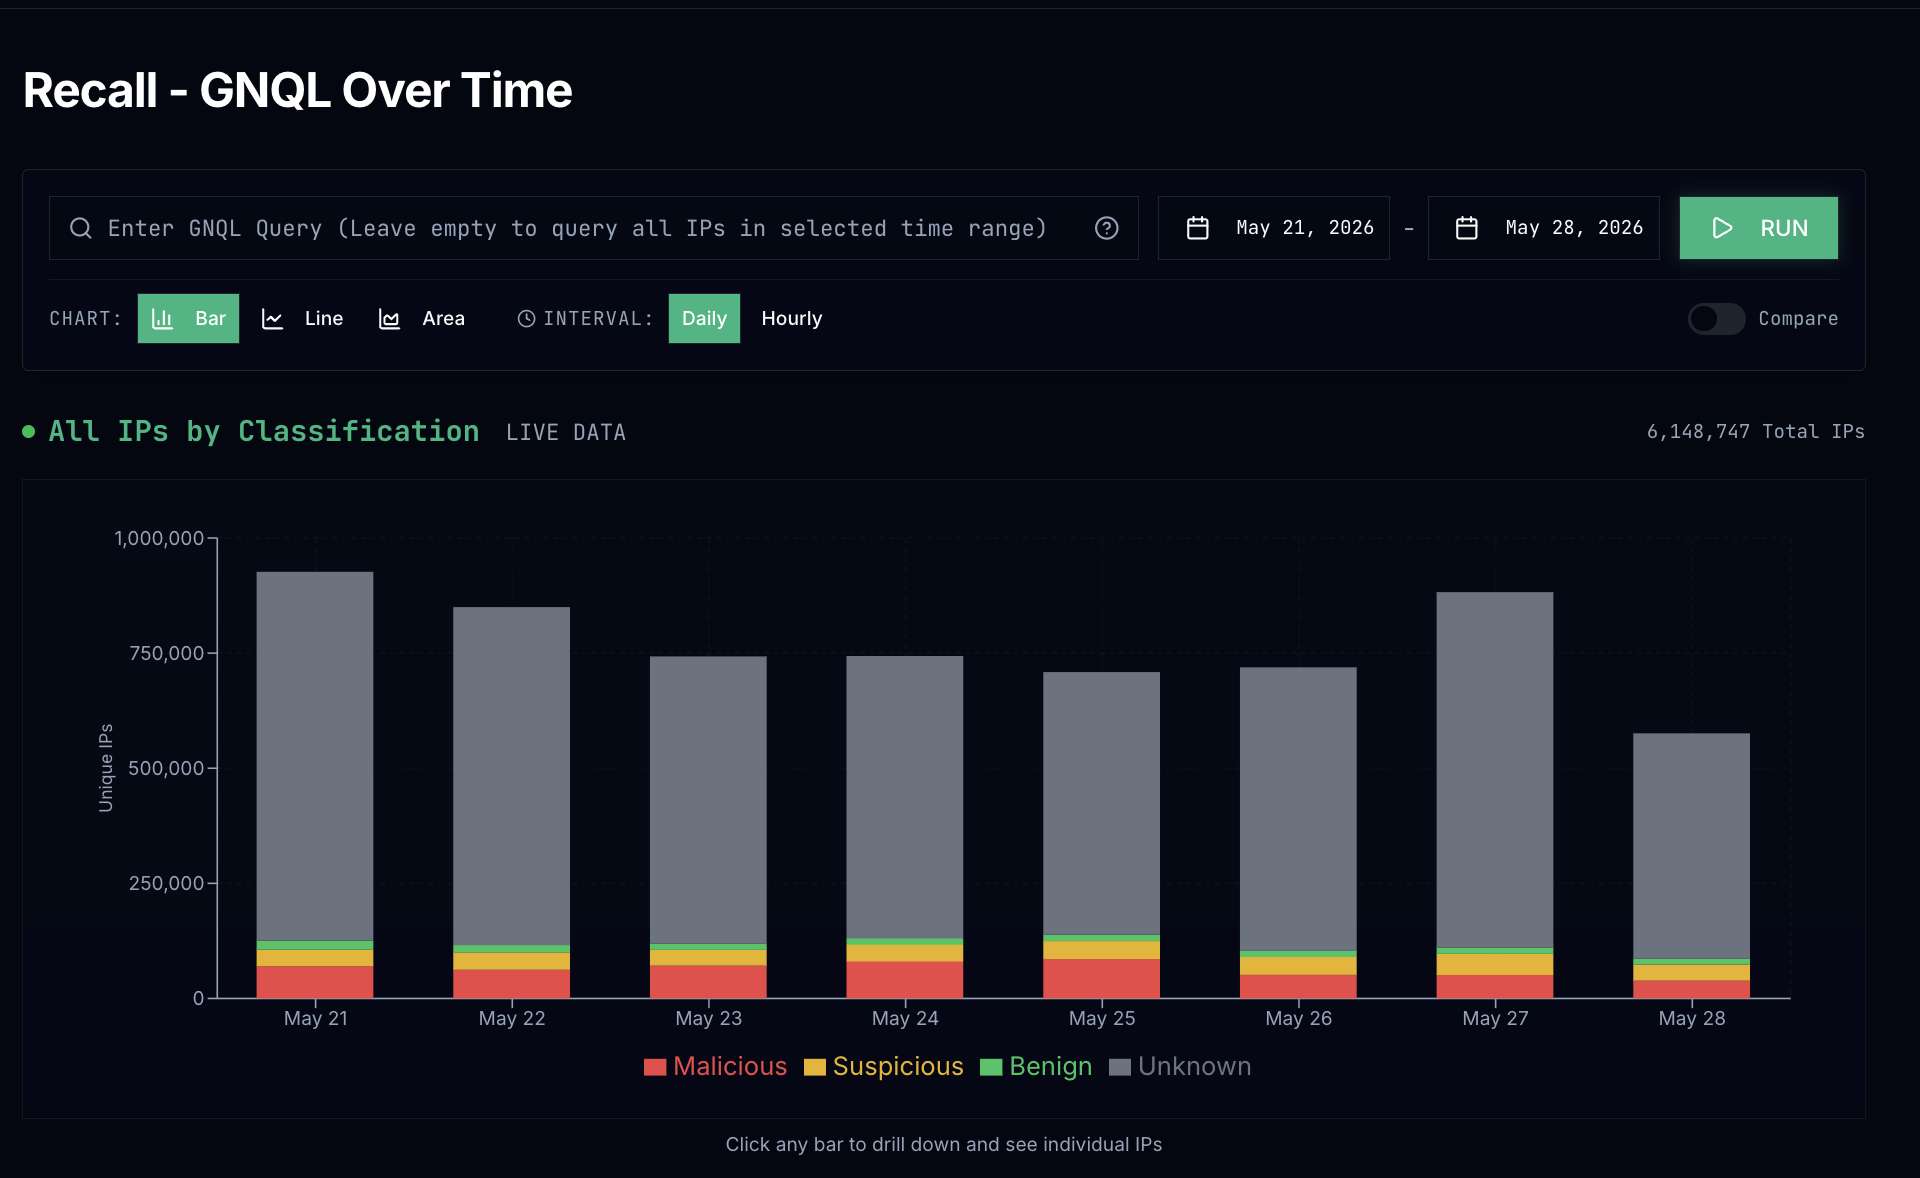
Block query builder simplifies to a single-column layout
Block: query builder collapses to a single column, removes the show/hide stats-bar toggle on desktop, plus dropdown styling and stats-bar visual cleanup
Change a sensor's public IP directly from the Visualizer
Visualizer: customers can now change a sensor's public IP address directly from the UI, bringing the sensor back online faster after an IP change
New RDP Botnet and Mirai Botnet Block templates
New Block templates: RDP Botnet and Mirai Botnet
Sensor bootstrap drops a distro and blocks conflicting network managers
Sensor bootstrap: narrowed the supported distributions and now refuses to install when a conflicting network manager is detected
Timeline filtering now uses real IP fields, fixing bad matches
Visualizer Timelines: filtering now uses real IP fields instead of stringified IPs, fixing several incorrect-match cases
Oct 9, 2025
Block hides advanced query controls when viewing a template
Block: advanced query-builder controls hidden when viewing a template, keeping the surface focused
Oct 8, 2025
Time Series drops records with empty first_seen and last_seen
Time Series: records with empty first_seen / last_seen are now filtered out so results are sane
Workspaces admin shows a proper name for expired invites
Visualizer admin: workspaces UI was rendering a raw JSON object as the workspace name for expired invites; fixed the fallback in nested table rendering
Oct 7, 2025
Added AWS provider entries to the providers data set
AWS provider entries added to the providers data set
Clearer template-click behavior in Block
Block: template-click behavior reworked for clearer affordances
Expanded Block docs for setup, blocklists, and templates
Block: comprehensive docs sweep covering setup, blocklists, and template usage
Oct 6, 2025
New Block users start from searchable pre-built templates
Block: onboarding overhaul — new users land in a searchable, sortable list of pre-built blocklist templates (trending first), signup collects name, job title, and EULA in one step, and new accounts are provisioned onto a dedicated Block plan from day one
Updated Visualizer navigation for sensor and profile management
Visualizer: navigation and page layout updated for the sensor, persona, and profile management pages
Oct 3, 2025
Block populates the Actor field and adds 'Add Another' everywhere
Block: query builder now populates the Actor field from the data backend, and 'Add Another' is available on every field type
Block query builder uses a single scroll bar for long lists
Block: query builder reworked to a single outer scroll bar instead of many nested ones — better feel on long template lists
Filter Block queries by last-seen recent activity
Block: last-seen classification field added to the query builder for include/exclude by recent activity
Fixed false positives in the Weston tag
Detection: Weston tag false-positive fixes
Pass an API key in the URL when downloading blocklists
Block: customers can now pass an API key in the URL when downloading blocklists, unblocking firewalls that don't support custom headers (docs updated)
Raw-data viewer now queries sessions, previewing Session Explorer
Visualizer: raw-data viewer now queries sessions — first end-user-visible surface of the new Session Explorer experience
Tightened CVE-2021-21974 tag to remove a false positive
Detection: tightened CVE-2021-21974 tag to remove a recurring false positive
Oct 2, 2025
Block GNQL responses now list plan-restricted fields
Block: GNQL responses now include an explicit message listing which fields were restricted for the user's plan, so users see exactly which fields were dropped and can contact sales
Time Series API now available for customers
Time Series API: customer-facing endpoint live — handler, pagination with LIMIT/OFFSET, RFC3339 timestamps, dual cve and cves params, a stats aggregation endpoint, a CTE-based unique-count fix that spans the whole window
Oct 1, 2025
Block account creation syncs name and email into entitlement records
Block account creation now syncs the user's name and email into the entitlements service, so customer data is populated on entitlement records from day one
Block query builder cleanup: per-field controls and CIDR Block rename
Block: 'Add Another' on every query-builder field, removed input defaults and debounce, stale-state on the stats sidebar, dropped auto-empty field on canvas drag, 'IP Address' renamed to 'CIDR Block', and 'Buy Now' opens in a new tab
New Grafana enumeration tag and CVE detection rule
Detection: new tag covering Grafana endpoint enumeration plus a specific Grafana CVE rule
New Palo Alto Block template
New Block template: Palo Alto, expanding the customer-ready template library
Sep 30, 2025
New tag flags Commvault enumeration scanners (CVE-2025-57790)
Same-week tag: CVE-2025-57790 — flags scanners trying to enumerate Commvault servers
Run raw GNQL queries with time-range presets and shortcuts
Visualizer: raw-data view query input — GNQL text, time-range picker with presets, expand/collapse, keyboard shortcuts
Visualizer adds a new top navigation with access-gated Sensors
Visualizer: new top navigation, with the Sensors section conditionally visible based on user access
Sep 29, 2025
Added per-classification last_seen timestamps to GNQL v3 — last_seen_malicious, last_seen_suspicious, and last_seen_benign — so customers can independently age out classifications when building queries, blocklists, and alerts (e.g. "show me IPs that have been malicious in the last 7 days, ignoring older benign hits"). Timestamps are minute-precision for privacy and respect each customer's data-reach entitlement. A long-requested capability that materially sharpens hunting and blocklist workflows.
GreyNoise Block (block.greynoise.io) is a new self-service blocklist product that lets security and network admins turn GreyNoise data into active network defenses — no procurement, no enterprise contract. Build precise IP blocklists with a drag-and-drop GNQL query builder, start immediately from GreyNoise-curated templates (including same-week templates for emerging vulnerabilities), and subscribe via credit card. Blocklists deliver directly into firewalls, WAFs, and proxies. Opens GreyNoise operationally to mid-market teams that were previously priced out, and is the first net-new revenue product the company has shipped in over a year.
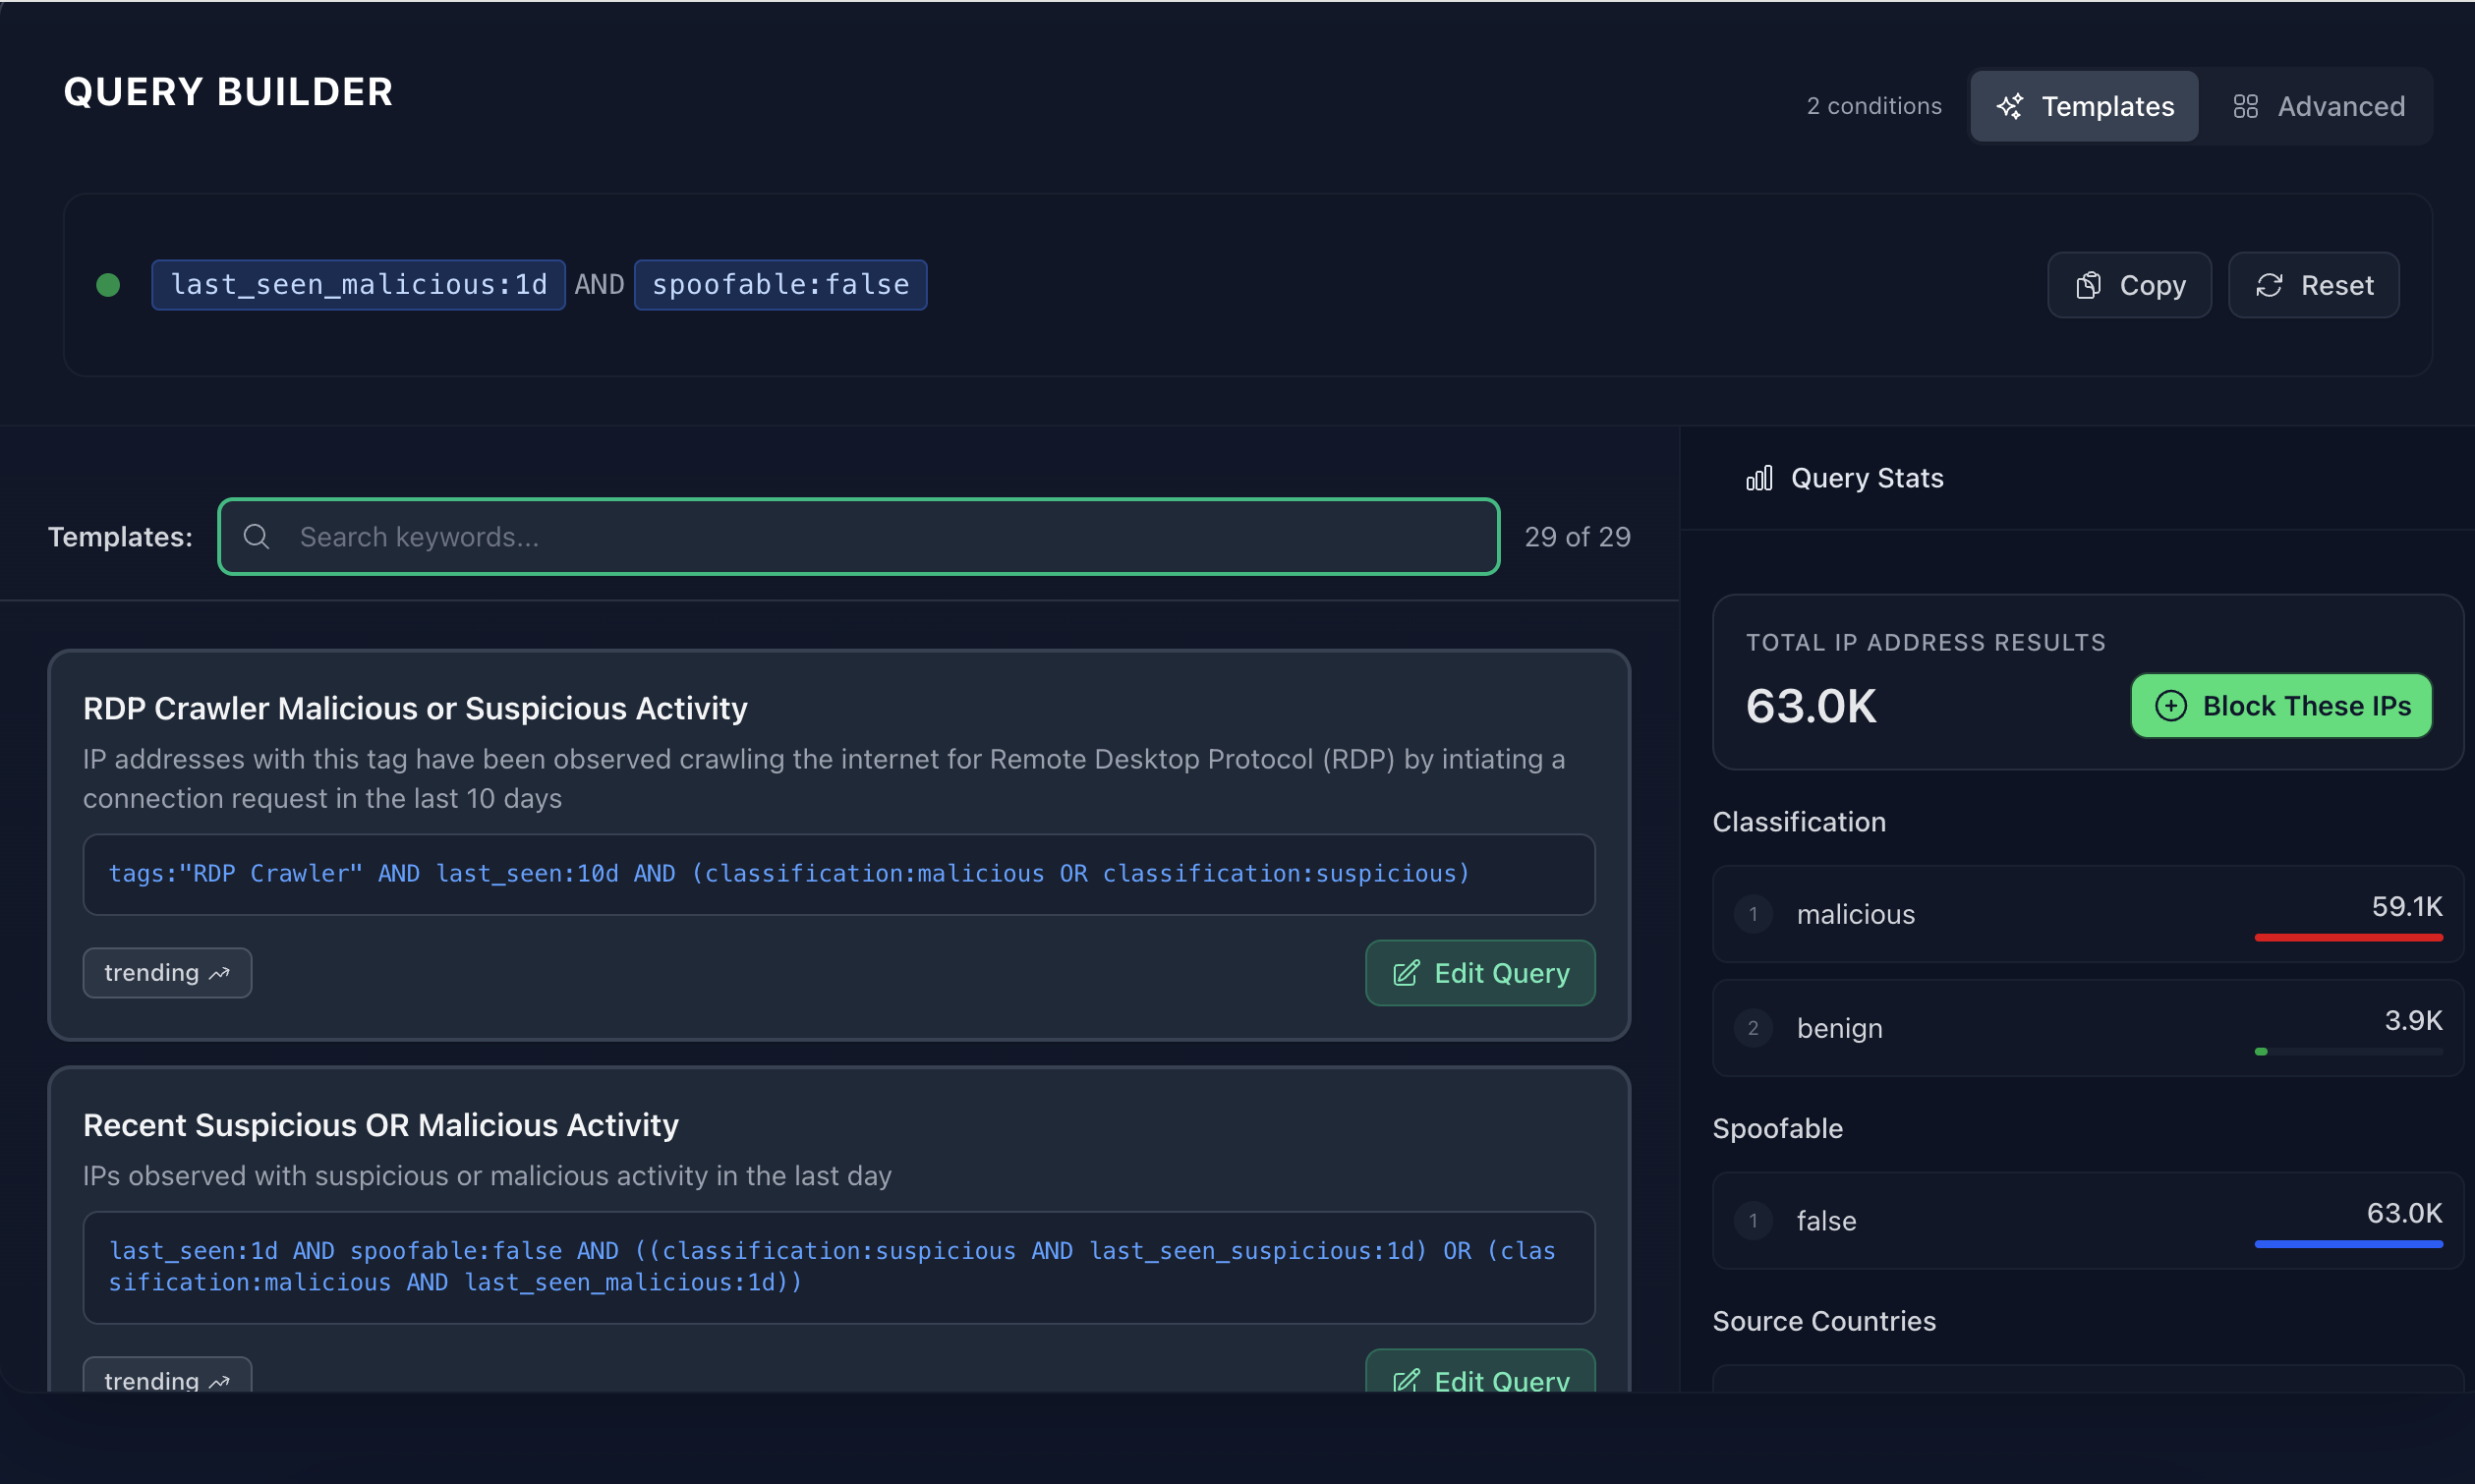
Block shows a provisioning page then routes you to Query Builder
Block: provisioning loading page while entitlements finish loading after signup, then redirect to the Query Builder
Fixed the Logsign RCE detection tag
Detection: small fix to the Logsign RCE tag
New tag for CVE-2025-6205
New tag: CVE-2025-6205
Trigger an on-demand blocklist refresh
Block: manual refresh endpoint — trigger a blocklist refresh outside the scheduled cadence
Workspace invitations no longer missed during signup
Visualizer: workspace invitations now retrieved before signup completes, fixing a flow where invites would be missed
Sep 26, 2025
New tag for Cisco Crawler activity
New tag: Cisco Crawler activity
Sep 23, 2025
Expired-plan Buy Now button routes to purchase
Block: Buy Now button on the expired-plan path wired through to the marketing site for conversion
Sep 22, 2025
Major foundation drop for historic time-series queries on GreyNoise data. Hourly snapshots and a new Timeseries service return per-datetime matched records. The substrate for long-lookback analytics — customers can now ask 'how has activity matching this query changed over the past 90 days?'
Sep 19, 2025
New Block users start with a 1-day blocklist lookback
Block: default blocklist lookback shortened to 1 day so new users start on a sensible default
Block classification colors aligned with the Visualizer
Block: classification color palette aligned with the Visualizer for cross-product consistency
Roughly 2,800 new Nuclei-derived tags across many CVEs
Four large drops across CVE-2010/2014/2015/2017/2018/2021/2022/2023/2024 ranges — roughly 2,800 tags generated via our tag-authoring pipeline
Trial subscriptions now provision correctly
Entitlement Service: trial subscriptions now include the required billing period so they provision correctly
Sep 18, 2025
~1,570 new CVE tags across two drops
Two drops spanning CVE-2017-2024 — one ~800-tag drop and a second ~770-tag drop
Roughly 1,600 new Nuclei-derived tags across many CVEs
Three large drops across CVE-2017/2020/2022/2024 ranges — roughly 1,600 tags, with manual edits to dedupe references and tighten over-generic XSS payloads
Threat map experiment added to the Visualizer
Visualizer: Threat map experiment added behind the experiments framework
Sep 17, 2025
Block opens directly on the Query Builder
Block: Query Builder replaces the initial landing page, making query construction the default first surface
Block refreshes shared-query blocklists together in one pass
Block: refresh logic now refreshes all blocklists sharing a query hash in one pass, deduping work and fixing updated_at semantics
New detection tag for CVE-2025-2907
New tag: CVE-2025-2907 (Tychesoftwares) — triage-queue-driven
Source Country in Block now has autocomplete
Block: Source Country input replaced with an autocomplete menu for faster value entry
Trial customers see time-remaining banner in Block
Block: trial-time-remaining banner on the top nav for trial customers
VulnCheck tags now carry a reference source for rule synthesis
VulnCheck reference field standardization: reference:source added to all VulnCheck tags (~100 files) so downstream rule synthesis points at the right authority
Sep 16, 2025
GreyNoise ships across three surfaces of the Falcon platform at once. In Next-Gen SIEM, the GreyNoise Foundry App auto-imports a daily indicator file; analysts use match() to surface classification, observed activity, and exploited CVEs inline with event data — no external pivot. In Fusion SOAR, GreyNoise enrichment drives automated playbook decisions: alert on malicious IPs, prioritize CVE remediation by exploitation evidence, and route with higher confidence using GreyNoise's benign classifications. In Charlotte AI Agentic Response, GreyNoise participates as an active automated collaborator on the investigation canvas — claiming question nodes, posting answers about whether an IP is mass-scanner noise or targeted threat infrastructure, and triggering Charlotte AI's next round of reasoning.
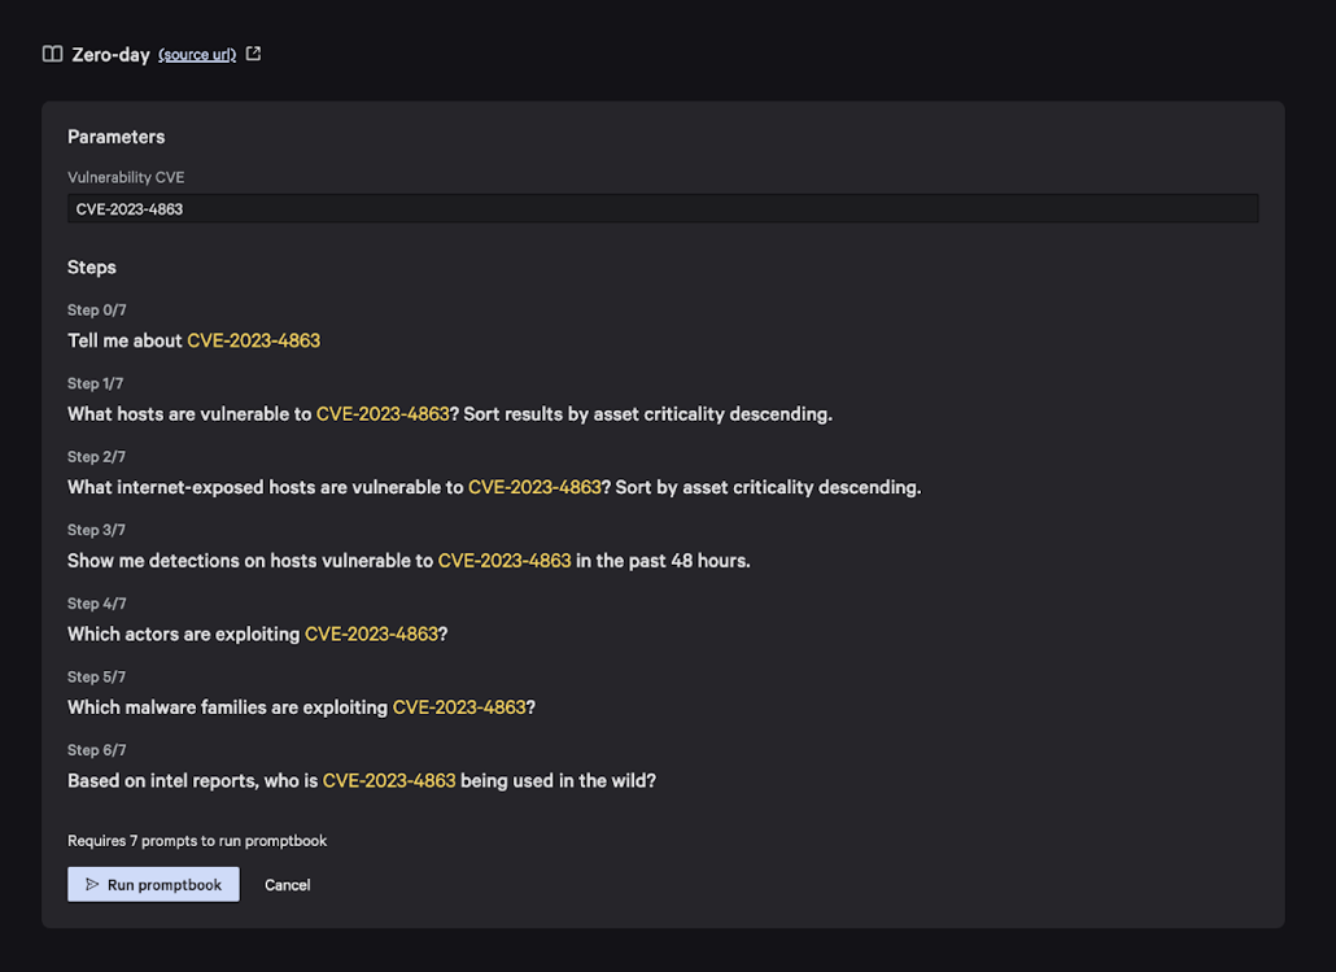
Backfill tags for CVE-2023-50224, CVE-2023-22463, and a SPON file-read
Backfill tags: CVE-2023-50224, CVE-2023-22463, plus a SPON IP file-read tag
Edit existing blocklists, including nested groups, in Block
Block: edit existing blocklists after creation, including nested-group editing
Sep 15, 2025
Block ships public documentation at block.greynoise.io/docs
Block: public documentation site shipped at block.greynoise.io/docs, with markdown styling polish
Fetch a single blocklist by ID via the Block API
Block: GET endpoint to fetch a single blocklist by ID
Name your blocklists in Block
Block: name field on blocklists end-to-end (API, service, UI) so customers can label their blocklists
Sep 12, 2025
Block blocklist service now scales horizontally to 1M IPs
Block: the blocklist service now scales horizontally, letting parallel workers build blocklists of up to 1M IPs
Block warns when a blocklist exceeds the plan IP limit
Block: warning coloring and tooltips when a blocklist's IP count exceeds the plan limit
Blocklist readiness now visible via last_request
Block: blocklist status surfaced via last_request — empty means pending refresh, populated means ready
Blocklist results table drops last_seen and spoofable columns
Block: stripped last_seen and spoofable from the blocklist results table to declutter the customer view
Capped-plan blocklists stop collecting once the IP cap is hit
Block: blocklist worker stops collecting once the IP cap is reached, materially cutting query work for capped plans
Clear all query conditions with one button in Block
Block: clear-canvas button on the query builder to wipe all conditions
New detection tag for CVE-2018-11336
New tag: CVE-2018-11336 — not in NIST but seen in the wild and listed by FortiGuard
Sep 11, 2025
Block enforces enabled-blocklist limits at creation time
Block: rechecks enabled-blocklist count against the customer's entitlement at creation time, closing a race where users could exceed plan limits
Feed creation flow gets a refreshed design
Viz: Feed creation flow re-styled per the new design
New tags for blue.php scanner and generic SQL injection
New tags: blue.php scanner and a research-surfaced generic SQL-injection-over-HTTP pattern
Per-blocklist data-reach lookback enforced by entitlement
Block: data-reach (last_seen lookback) enforcement per blocklist based on the customer's entitlement
Per-blocklist IP limits enforced by customer entitlement
Block: per-blocklist IP-limit enforcement driven by the customer's entitlement (default unlimited)
Regenerate your Block API key from the UI
Block: API key recycle — backend handler and UI for regenerating a Block API key
Search menu now links out to GNQL reference docs
Viz: search menu dropdown now links out to GNQL reference docs
Thousands of new Nuclei-derived detections begin rolling out
Initial bulk drop: first major drop of Nuclei-template-derived tags — kicks off a multi-week program that produced thousands of new GNQL-queryable detections
View the IP list for an individual blocklist
Block: IP-list viewer for an individual blocklist
Sep 10, 2025
Block UI now supports light and dark mode
Block: light/dark mode parity in the UI
Blocklist UI shows a meaningful state while service warms up
Block: 503 propagation when the underlying blocklist service is still warming up, so the UI can show a meaningful state
Copy a blocklist URL directly from each row
Block: per-row copy-URL button on the Blocklist page so customers can quickly grab a blocklist URL
GNQL last_seen paging is now consistent
GNQL v3: stabilized last_seen ordering (was only second-precision, causing inconsistent paging)
New tag for FreePBX SQL injection activity
New tags: FreePBX SQL injection activity
One-click template to protect Fortinet appliances
Block: one-click 'Fortinet last_seen:7d' template for protecting Fortinet appliances
RIOT adds HTML source scraping for select services
RIOT V2: HTML-based source scraper implementation for certain RIOT services
Start blocklists from pre-built query templates
Block: pre-built query templates — Query Templates tab with four starter templates, plus a GNQL parser that converts the template's query back into a visual condition tree
Sep 9, 2025
Block API moves to a versioned /v1 path
Block API: path prefix renamed from /api to /v1 in preparation for sitting on api.block.greynoise.io
Blocklists are now scoped to a workspace
Block API: blocklists are now scoped to a workspace rather than an individual user
Sep 8, 2025
Download blocklists from the new Block API endpoint
Block: blocklist download endpoint shipped in the Block API; copy/download URL now points at the Block API instead of GNQL
New tag for CVE-2025-34143
New tag: CVE-2025-34143
Refreshed IP list for the Nokia Deepfield benign tag
Updated IP list for the Nokia Deepfield benign tag
Tag chart y-axis no longer dips below one
Visualizer: tag chart y-axis steps never go below 1, fixing a small visual oddity on low-activity tags
Triage Intelligence module now renders by default
Visualizer: Triage Intelligence Module is now the default when intel modules render, fixing a customer-confusion on-call ticket
Sep 5, 2025
Feeds gains a new CVE Activity Spike event type that fires when a CVE sees a meaningful surge of exploitation activity — configurable minimum percentage change and minimum IP count let customers cut through the noise (e.g. a single Nuclei scan won't trigger). The first feed type built directly from customer feedback, closing the loop between the existing CVE status-change feed and real surge detection.
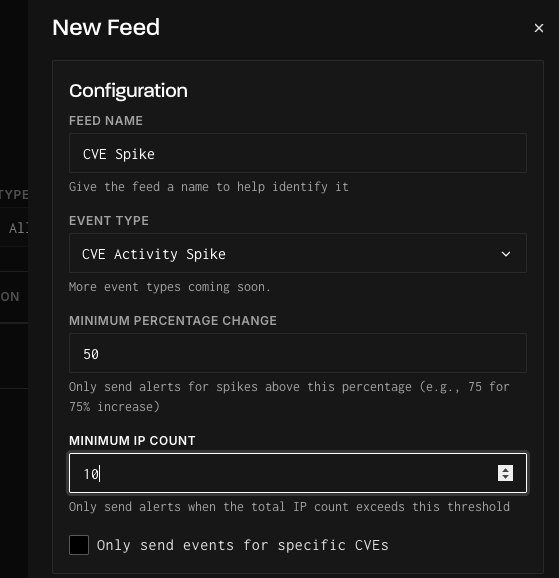
Shipped the GreyNoise Model Context Protocol server as an opt-in integration on the Visualizer Experiments page, making GreyNoise data directly addressable from any MCP-aware AI tool — Claude Desktop, Cursor, and the broader agent ecosystem. Customers can wire up an agent to query IPs, pull tag context, and pivot through GNQL without ever opening the Visualizer. The first GreyNoise-shipped channel for getting our signal into the tools security teams are actually using day-to-day — and a foundation we'll build on as agent-based workflows replace tab-based ones across SOC operations.
Create blocklists end-to-end with live data
Block: create-blocklist flow wired end-to-end
Create hardware-profile sensors from the Visualizer
Hardware-profile sensors can now be created from the Visualizer
New actor tag for the Stony Brook / UBC research project
Actor tag for the Stony Brook / UBC academic research project hitting GreyNoise sensors
See query stats at a glance in Block
Block: query stats panel with loading states and a header toggle
Sep 4, 2025
Block adds welcome and account settings pages
Block: Welcome and Account pages — first-run prompt plus user/workspace settings
Manage all your blocklists from a new landing page
Block: Blocklist landing page where users see and manage their blocklists
New tag for TP-Link CWMP buffer overflow
New tag: TP-Link CWMP buffer overflow
RIOT adds diff and intersect operations on IP lists
RIOT V2: diff and intersect set-operations on IP lists for rule filtering
Sharper rules for the 'not exploitable' CVE banner
Visualizer: tightened logic for when the 'not exploitable' banner appears on CVE detail pages
Sep 3, 2025
Add custom headers to AlertOps webhook destinations
AlertOps: webhook destinations now support user-supplied custom headers, matching other destinations
CVE Analysis now detects every CVE mentioned in text
Visualizer: CVE Analysis now scans for all mentioned CVEs in the text (was only picking up the first)
Fixed HASSH-based tag detection logic
Detection: fixed HASSH-based tag logic that was failing CI; verified against CHINANET SSH bruteforcer fixtures
New feeds work without per-feed receiver config
Feeds receiver: accepts all root-path POSTs so new feeds do not require explicit per-feed config changes
New tags for Mercurial and GNU Mailman crawlers
New tags: Mercurial Crawler, GNU Mailman Crawler
RIOT V2 ships its first production services and rules
RIOT V2: first production drop of the V2 rewrite — services and rules imported into the V2 management API via Terraform
Subscribe to CVE Activity Spike events in Feeds
Visualizer: Feeds now surfaces CVE Activity Spike events so customers can subscribe to spike notifications
Tagging coverage added for recently-disclosed CVEs
VulnCheck weekly bulk drops (early Sept): multiple VulnCheck bulk merges producing tagging coverage for recently-disclosed CVEs
Update and delete your blocklists via the Block API
Block: update and delete blocklist endpoints in the Block API
Sep 2, 2025
First wave of PCAP-anomaly tags
Detection content (wave 1): first batch of ~40 PCAP-anomaly-derived tags built with our tag-authoring tooling and Nuclei templates, including AI-assisted names and descriptions
Rotated the public PGP key in security.txt
Disclosure: rotated the public PGP key in security.txt (previous key expired 2025-09-01)
Aug 29, 2025
Rebuilt the platform Blocklist service on a managed-service architecture for enterprise customers. Workspace-owned, with materialized blocklist storage, an async GNQL resolver, and full create/read/update/delete plus a download endpoint. The substrate for enterprise customers to turn any GNQL query into a live, subscribable blocklist that plugs into a firewall, proxy, or SIEM pipeline.
A substantial month for Retrohunt converted the feature from a working pipeline into a productized capability. New: a query analysis endpoint that previews retrohunt results without running them — so analysts know whether a hunt is worth the compute before they spend it. Plus per-tier entitlement enforcement on time range and max files, workspace-scoped query filtering, automatic retrohunt when a new tag is authored (closing the loop between content authoring and historical coverage), session metadata grouping for first-packet ordering, and search aggregations for performance.
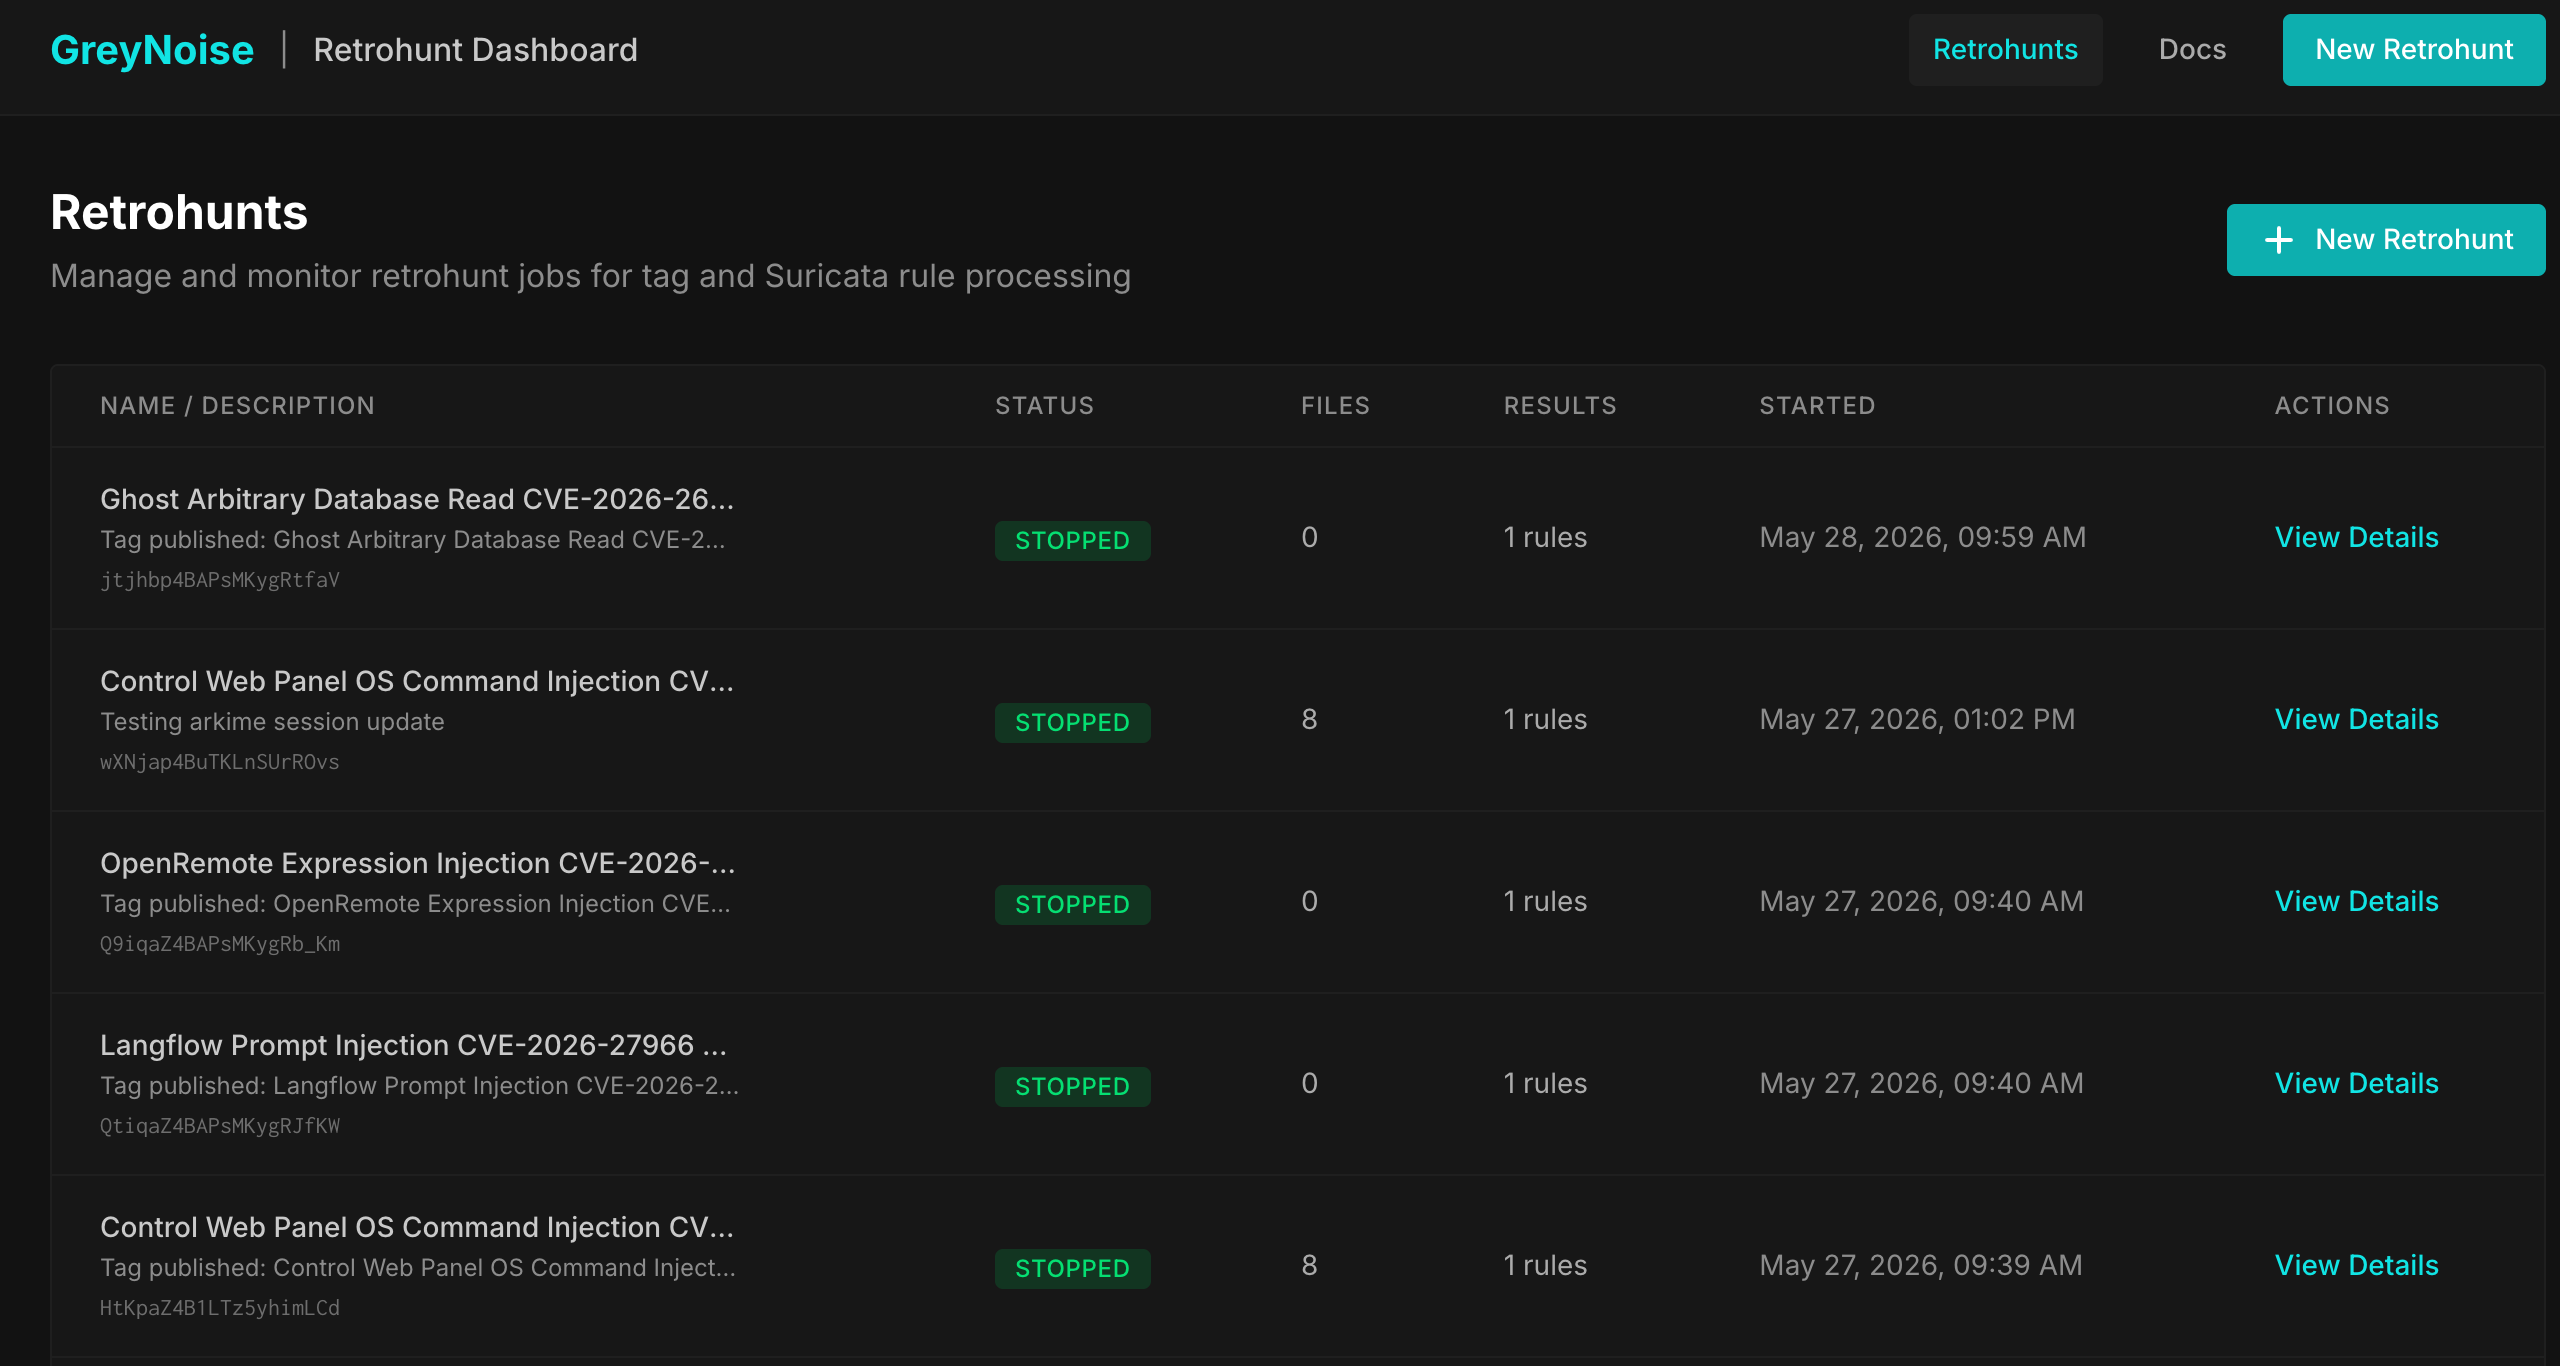
Backfilled detection coverage for historical CVEs
Historical CVE coverage: backfilled tags for CVE-2016-15044, CVE-2013-1965, CVE-2021-35336, CVE-2024-46450, CVE-2024-32640, CVE-2001-0500, plus a tightened CVE-2017-6884 (Zyxel) tag scoped to specific exploit paths
New CVE Activity Spike event fires on rapid CVE surges
Feeds: new CVE Activity Spike event type — fires when a CVE sees a meaningful surge in scanning IPs within an hour
Aug 28, 2025
Disabled unsupported sort on the Sensors current-profile column
Viz: Sensors table sort disabled on the 'current profile' column (sorting it returned an empty table because the API doesn't support it)
GNQL query export now uses the v3 API
Viz: GNQL query export now goes through the v3 API
New tag for CVE-2025-8356
New tag: CVE-2025-8356
Aug 27, 2025
First machine-generated detection tag shipped to production
First machine-generated detection tag shipped to production — produced by an expert system that mimics analyst tag authoring, a meaningful milestone for tag content velocity
Netscaler ADC and Gateway tag shipped at disclosure
Same-week tag: CVE-2025-7776 — Netscaler ADC and Netscaler Gateway, shipped the same week as public disclosure
New tags for CHCNAV GNSS backdoor and backlog items
Tag batch (Aug 26 queue): CHCNAV P5E GNSS API credential leak / backdoor (CVE-2022-30622) plus backlog detections
Updated copy on the CVE activity view
Viz: CVE activity view copy update
Aug 26, 2025
Dry-run RIOT V2 rules before committing them
RIOT V2: rule dry-run endpoint — test rules without committing them, useful for rule authoring and validation
Aug 25, 2025
Two coordinated pieces shipped that together make custom certificates a first-class sensor-profile capability — driven by an inbound enterprise deal that required deploying their own certificates to GreyNoise sensors. The sensor agent gained custom-certificate support via a profile config change, and a new Certificate Service was stood up to manage the certificates that get assigned to profiles, with a Go client and full CI. Closes a recurring enterprise objection.
New tag detects web-check unauthed RCE (CVE-2025-32778)
New VulnCheck-sourced tag: CVE-2025-32778 (lissy93/web-check unauthed RCE)
New tags for Robomongo crawler and Citrix ADC Gateway
Tag batch (2025-W33): Robomongo Crawler, Citrix ADC Gateway login panel, and others
Visualizer pages now get canonical URLs for indexing
Viz: canonical URLs assigned to Viz pages so Google indexes them as distinct pages rather than collapsing to the index page
Aug 22, 2025
New tag for CVE-2025-57788
New tag: CVE-2025-57788
Redesigned charts return after a hydration fix
Viz: ChartJS-based chart redesign reshipped after a hydration fix (initial rollout caused hydration-related 500s on direct page loads and was reverted)
Aug 21, 2025
Customers can now export GNQL query results as CSV directly from the v3 API by passing a `format` query parameter, with docs updates and a compression fix for empty responses. Removes the long-standing manual workaround of scripting against JSON responses to produce a CSV.
Alerts catch empty bulk-data files before they ship
Bulk data: error-detection logging plus size monitoring and an alert when the most recent bulk file lands under 1 MB
New tag detects ICTBroadcast command injection (CVE-2025-2611)
Same-week tag: CVE-2025-2611 — ICTBroadcast login command injection (initial coverage plus refined attempt-path detection)
New tags for suspicious-PATCH RCE, path traversal, and more
Tag batch (Aug 21): suspicious-PATCH potential-RCE, WEB-INF path traversal, ICTBroadcast follow-ups, and additional backlog detections
Aug 20, 2025
GreyNoise for Splunk SOAR is updated to SDK v3.0.1, adding webhook support, CVE lookups, and updated IP lookups aligned to the latest API. Security teams running Splunk SOAR automation workflows can now monitor GNQL queries and threats via webhook, pull CVE exploitation context inline, and get the most current GreyNoise enrichment on every IP lookup — without leaving their SOAR playbook.
Aug 18, 2025
New tag detects FortiSIEM pre-auth command injection (CVE-2025-25256)
Same-week tag: CVE-2025-25256 — FortiSIEM pre-auth command injection
New tags for Ivanti Connect Secure login attempts and bruteforce
New tags: Ivanti Connect Secure login attempts and Ivanti Connect Secure bruteforce
New tags for MapSVG SQL injection and WordPress login bruteforce
Tag batch (Aug 18): MapSVG WordPress plugin SQL injection and WordPress login bruteforce detection
Old tag slugs now redirect to their new URLs
Viz: tag detail page now redirects users from old tag slugs to the new slug via the public tag lookup endpoint
Refreshed Qualys scanner attribution in RIOT
RIOT: Qualys IP and domain list refreshed for benign-scanner attribution
Tag detail pages handle long reference lists cleanly
Viz: Tag Detail references section handles a much larger number of references without breaking layout
Aug 15, 2025
First Terraform-native integration for the platform. Operators can now manage GreyNoise resources as code, starting with RIOT V2 service resources. Moves GreyNoise toward an infrastructure-as-code management story and makes it materially easier for security-engineering teams to provision, version, and review GreyNoise configuration alongside the rest of their stack.
New paginated CVE, product, and vendor search endpoints
API: paginated CVE search plus product/vendor search handlers — foundation for richer CVE and vendor browse experiences
Aug 14, 2025
New tags for Dahua camera CVEs and backlog detections
Tag batch (Aug 13): Dahua Hero C1 Smart Camera CVE-2025-31700 and CVE-2025-31701, plus several backlog detections
Updated Qualys tag with the latest scanner IPs
Qualys tag: updated with the published list of Qualys scanner IPs for better attribution
Aug 13, 2025
New tag for CVE-2025-51482
New VulnCheck-sourced tag: CVE-2025-51482
RIOT V2 services list endpoint now supports filtering
RIOT V2: services list endpoint now supports a filtering parameter
Aug 12, 2025
New tag detects WarHawk C2 attempts
New tag: WarHawk C2 attempts
Removed the deprecated CVE Sky experiment
Viz: deprecated CVE Sky experiment removed from the experiments page
Tag-based alerts show a tag badge instead of a raw UUID
Alerts: tag-based alerts now show the alert name with a tag badge in the subtitle instead of the raw tag UUID
Tag search now jumps to a pre-filtered Tags Directory
Viz: tag-dataset search modal now offers a 'See all results' jump into the Tags Directory pre-filtered with the search term
Aug 11, 2025
New tag for CVE-2025-54309
New VulnCheck-sourced tag: CVE-2025-54309
New tags for Portainer crawler, LFI, and backlog items
Tag batch (2025-W32): Portainer crawler, ag_proc0_9fd0_9 LFI, and a set of backlog detection requests
Aug 8, 2025
New tag detects XWiki LiveData REST SQL injection (CVE-2025-32429)
Same-week tag: CVE-2025-32429 — XWiki LiveData REST SQL injection (covers both checker and exploit-attempt paths)
New tag for WordPress XML-RPC method enumeration and backlog items
Bulk triage batch (Aug 6–8): WordPress XML-RPC method enumeration and other backlog items
Aug 6, 2025
Fix duplicate alert receipts and alert-tag associations
Alerts: duplicate-alert receipt fix and alerts-tag-association fix
Free-tier access opened on the /v3/ip endpoint
API: free-tier access opened on the /v3/ip endpoint — legacy free-tier and offering middleware gating removed; access and rate-limiting now flow through the entitlements service and handler-level checks
New tag for Exchange Server Autodiscover scanning
New tag: Exchange Server Autodiscover service scanner
Aug 5, 2025
Same-week tag for Cisco ISE RCE (CVE-2025-20337)
Same-week tag: CVE-2025-20337 — Cisco ISE command injection and container-escape RCE
Aug 4, 2025
New tag for OpenWrt LuCI interface crawlers
New tag: LuCI Crawler (crawlers targeting the OpenWrt LuCI interface)
Weekly VulnCheck detection rule batch added
Tag batch (VulnCheck rules, 2025-W31): weekly batch of VulnCheck-sourced detection rules
Aug 1, 2025
New tag for Showdoc file-upload exploit attempts
New tag: Showdoc file-upload exploit attempt
New tags covering CVE-2025-46811
New tags covering CVE-2025-46811
Jul 31, 2025
Deployed the HTTP enrichment pipeline v2 to production with IP scrubbing across every URI field and always-on dedupe on writes. Strips PII before URIs are published and collapses the cardinality explosion caused by mass scanners hitting the same URL from many different IPs. Cleaner data, lower storage cost, and a privacy-safe surface for the web-paths corpus that powers Threat Hunting.
Clearer error when a GNQL query has no destination sensor
Viz: clearer error messaging when a GNQL query has no destination sensor
Jul 30, 2025
Fix Retrohunt result rows to match tag IDs
Retrohunt: result rows and tag IDs now match
More accurate CVE-to-product mapping from NVD CPE data
CVE Service: internal CVE records enriched with NVD-sourced CPE lists — better CVE-to-product mapping accuracy
New tag for WordPress WPBookit file upload (CVE-2025-6058)
New tag: WordPress WPBookit plugin file upload (CVE-2025-6058)
Sort GNQL search results by most recent activity
GNQL: sortable last_seen v2 timestamp field — customers can sort search results by most recent activity
Tuned IP timeline section display
Viz: IP timeline section display tuning
Jul 29, 2025
Auto-provision API keys for SSO-created users
Auth: API keys auto-provisioned when a user is created via SSO — removes a manual onboarding step
Fixed Single-Destination flag classification
Corrected how the Single-Destination flag is calculated
Fix Visualizer API key passing in bulk CVE analysis
Bulk CVE Analysis: Viz API key now flows through the request context — was previously always failing the check
Hide workspace switcher for single-workspace users
Viz: 'change workspace' affordance hidden for users with only one workspace
Improved rate-limit error logging for 429 debugging
Viz: rate-limit error-page logging improved for 429 debugging
New tag for Delta InfraSuite Device Master RCE (CVE-2023-1133)
Research tag: Delta Electronics InfraSuite Device Master unauthenticated .NET deserialization RCE (CVE-2023-1133)
New tag for Qdrant vector-DB directory traversal (CVE-2024-3584)
New tag: Qdrant vector-DB directory traversal (CVE-2024-3584)
Same-month tag for AMI MegaRAC SPX auth bypass (CVE-2024-54085)
Same-month tag: AMI MegaRAC SPX baseboard-management authentication bypass (CVE-2024-54085)
Jul 28, 2025
CVE and tags endpoints added to the public OpenAPI spec
Bulk CVE Analysis: CVE and tags endpoints added to the public OpenAPI spec, deprecated endpoints removed, staging docs promoted to production
Deduplicated CPE strings to reduce vulnerability data noise
CVE Service: CPE-string dedup by part/vendor/product — less noise in vulnerability data
VulnCheck source attribution now visible in the catalog
VulnCheck source attribution backfilled across the affected rules — provenance now visible in the catalog
Jul 25, 2025
New CVE Analysis page in the Visualizer at /cves/analysis — paste or upload a list of CVEs and get back GreyNoise's exploitation-activity context in one shot, with entitlement-aware file-size limits. Mirrors the existing IP Analysis flow, for CVEs.
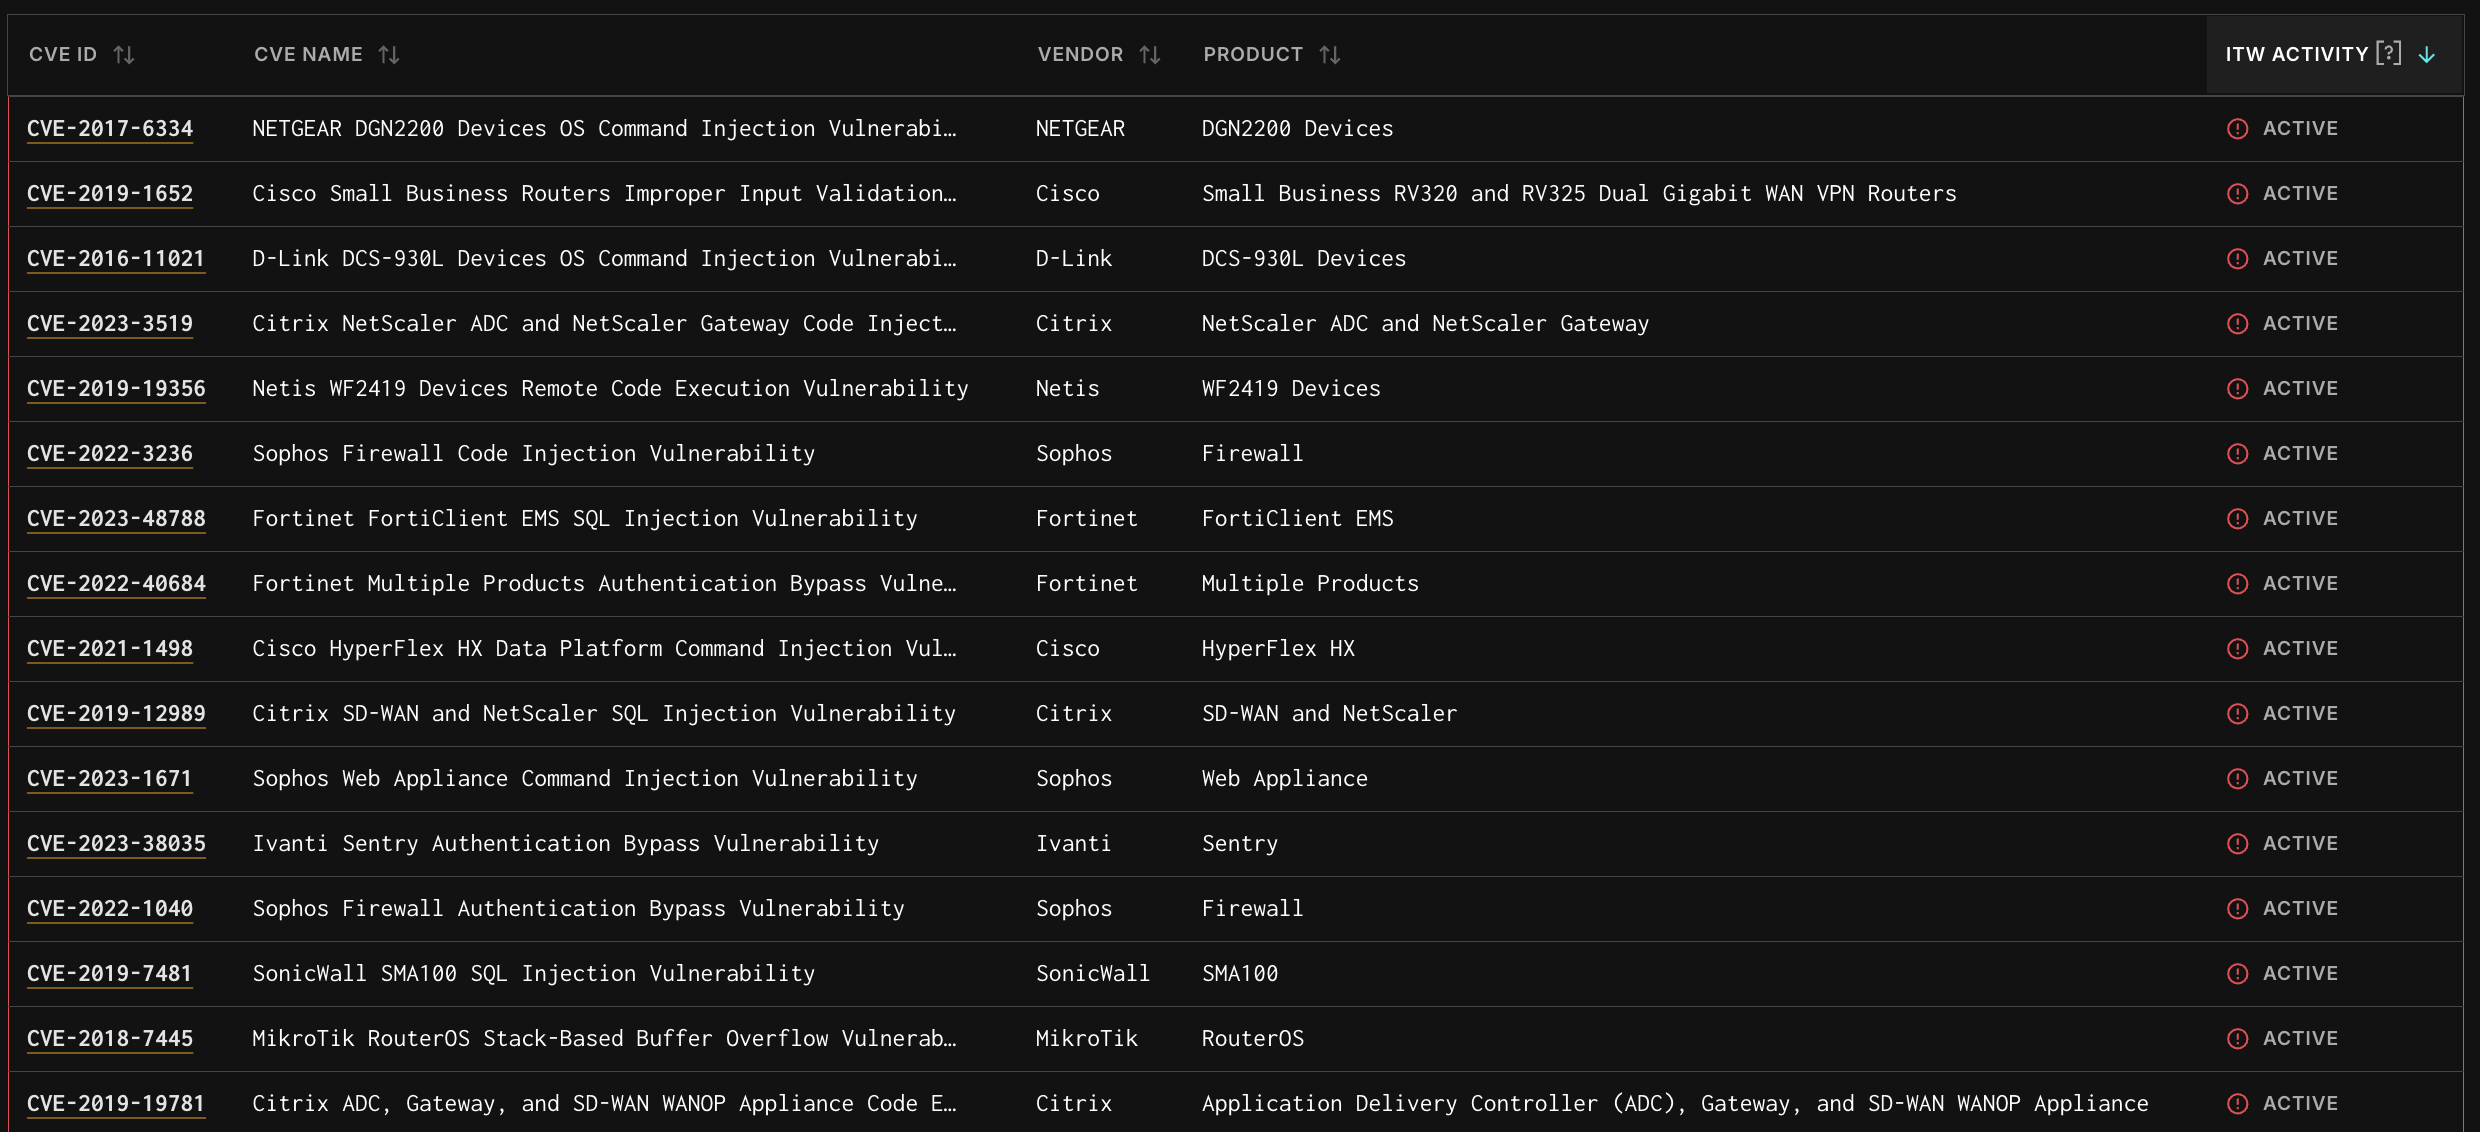
Customer-visible detection for MCP and SSE endpoint scanning
MCP and SSE endpoint scanning tag: silent flag removed — first customer-visible detection coverage for AI tooling endpoints
Fix redirect loop forcing Viz admins to clear cookies
Auth Layer: redirect-loop fix — closes the oncall report where Viz Admin users had to delete cookies frequently to regain access
More lenient PDF parsing for uploaded CVE analyses
CVE Service: more lenient PDF parsing on customer-uploaded analyses
New tag for Alcatel AP1361D command injection (CVE-2025-52688)
Bulk triage: Alcatel AP1361D web-login command injection (CVE-2025-52688) and related items
Single-IP search and CVE/IP analysis forms refined
Viz: single-IP search regex improved + CVE/IP analysis form refinements
Jul 24, 2025
IP timeline restores classification default and full date range
IP timeline (v3): the default field is 'classification' again and the date-range truncation is gone
New tags for Panabit, Avocent PDU, and TOS CVEs
Detection tag batch: Panabit Panalog LibRes PHP command exec, Avocent power-management PDU default creds, TOS-related CVEs
Jul 23, 2025
Broader CVE coverage from VulnCheck's cpe-vulnerable index
CVE Service: VulnCheck client now pulls from the cpe-vulnerable index — expands vulnerability coverage
Jul 22, 2025
New tag for Google Compute Engine metadata-access scanners
New tag: Google Compute Engine metadata-access scanner
New tag for mooSocial mooStore RCE (CVE-2023-4174)
New tag: mooSocial mooStore RCE (CVE-2023-4174)
Jul 21, 2025
Turned on rate limiting for free-tier users with entitlement-aware backoff and graceful error handling in ReportUsage. The Visualizer ships a dedicated authenticated rate-limit page when users hit a 429, and the experience was reworked off cookie-based tracking onto a clean error page. The largest pricing-and-packaging milestone of the month — closes the loop between tier entitlements and actual usage enforcement.
Rate-limit hits now show a clean error page
Viz: rate-limit experience reworked off cookie-based tracking onto a clean error page
Same-day tag for SharePoint ToolShell RCE chain (CVE-2025-53770)
Same-day tag: 'ToolShell' — in-the-wild Microsoft SharePoint pre-auth RCE chain (CVE-2025-53770) — plus follow-on implant-check tag for spinstall0.aspx web shells
Tag fixes for Docker, EGroupware RCE, and PHPUnit
Detection tag batch: Docker scanner rule fix, EGroupware spellchecker PHP command-injection RCE, PHPUnit RCE accuracy improvement
Jul 18, 2025
IP page now supports the metadata.domain GNQL facet
Viz: metadata.domain GNQL facet supported on the IP page — fixes an oncall report
Refreshed public API documentation
Viz: public API documentation refreshed
Same-week tag for Ivanti EPMM RCE with retrohunt backfill
Same-week tag: Ivanti EPMM RCE (CVE-2025-4428) — a retrohunt enables backfill across stored traffic
Tag fixes for EJS SSTI, Cacti Weathermap, Eir D1000, and Yonyou NC
Detection tag batch: session-query fixes across EJS SSTI and others, Cacti Weathermap arbitrary file write, plus Eir D1000 TR-064 CVE-2016-10372, Yonyou NC NCMessageServlet deserialization RCE
Tag timeline now sources created date from one source of truth
Tag Timeline: created-date sourced from tagManager (single source of truth), events sorted chronologically, 'GreyNoise Created Tag' event named explicitly
Jul 17, 2025
Akamai added as a trust-level-1 RIOT provider
RIOT: Akamai added as a trust-level-1 provider with Edge DNS/DHCP resources
Dedicated rate-limit page shown on 429 responses
Viz: dedicated authenticated rate-limit page exposed on 429 responses — part of the free-tier rate-limiting rollout
Larger analysis upload limits for paid tiers
Viz: analysis-upload file size now entitlement-checked — paid tiers get larger upload windows
Jul 16, 2025
New tags now auto-trigger a historical retrohunt
Retrohunt: Tag Service auto-triggers a retrohunt when a new tag lands — closes the loop between content authoring and historical coverage
Same-day tag for Cisco ISE deserialization (CVE-2025-20281)
Same-day tag: Cisco ISE Java deserialization (CVE-2025-20281) + ENV scanner rule refresh
Tag fixes for PHP CGI RCE and PDR Labs actor rules
Detection tag fixes: PHP CGI RCE rule and PDR Labs actor rule
Tag IP export copy clarifies it always covers the last 24 hours
Viz: Tag IP export copy clarifies that exports always cover the most recent 24 hours regardless of selected time range
Jul 15, 2025
Extended rule coverage for the AWS Configuration Scanner tag
Extended rule coverage on the AWS Configuration Scanner tag
New tag for Ollama API endpoint crawling
Silent tag: Ollama API endpoint crawling — emerging risk as LLM-serving endpoints get exposed to the internet
One upstream event can now fan out to multiple feed events
A single upstream event now fans out to multiple Feed events (e.g. a New IP also triggers an IP classification change) — foundation for multi-feed coverage
Jul 14, 2025
New tag for ASUS auth-bypass exploit chain (CVE-2025-2492)
Silent tag: ASUS auth-bypass exploit chain (CVE-2025-2492)
Tag updates for Brother printers, Realtek worm, Azure OMI, and Zimbra
Detection tag batch: Brother Printer crawler, URI computer-architecture-string (malware-dropper pattern), VulnCheck updates for Realtek miniigd UPnP worm (CVE-2014-8361) and Azure OMI RCE, Zimbra Collaboration Suite XXE tightened so Metasploit's module is reliably detected
Jul 11, 2025
Hello World scraper botnet tag promoted to suspicious
Hello World scraper botnet tag promoted to suspicious classification based on observed behavior
New Sitecore crawler tag and redundant-field cleanup
New Sitecore crawler detection tag + redundant-field cleanup across several existing tags
Same-week tag for FortiWeb pre-auth SQLi RCE (CVE-2025-25257)
Same-week tag: Fortinet FortiWeb pre-auth SQL-injection RCE (CVE-2025-25257) — based on the WatchTowr public PoC
Jul 10, 2025
Feeds charts and sparklines restored in the Visualizer
Viz: Feeds charts and sparklines restored on the Feeds experience
New detection tags for CData, Cisco IOS, ScriptCase and Wanhu RCEs
Detection tag batch: CData Connect Java directory traversal (CVE-2024-31849), Cisco IOS unauthorized command-execution RCE, D-Link UPnP exploits, ScriptCase pre-auth RCE (CVE-2025-47227) and Wanhu OA RCE
New tag detects the Hello World scraper botnet
New tag: JA4-fingerprint detection for the Hello World scraper botnet
Jul 9, 2025
Same-day tag for SonicWall SMA1000 deserialization (CVE-2025-23006)
Same-day tag: SonicWall SMA1000 Java deserialization (CVE-2025-23006)
Jul 8, 2025
New tags for Pterodactyl Panel and Sitecore XP RCEs
Bulk VulnCheck research drop: Pterodactyl Panel RCE (CVE-2025-49132), Sitecore XP authenticated PowerShell and UploadPage2 RCEs (CVE-2025-34510/34511)
Retrohunted IPs now appear in customer search results
Retrohunt: replayed IPs now flow into GNQL sync runs — retrohunted data shows up in customer search results
Same-week tag for Wing FTP unauthenticated RCE (CVE-2025-47812)
Same-week tag: Wing FTP Server LoginOK.html unauthenticated RCE (CVE-2025-47812)
Jul 7, 2025
New tags for Apache Axis, HongJing HCM and IBM MQSeries
Tag-authoring sprint, June 2025, part 1: tag batch closing out June (Apache Axis version check, HongJing HCM SQLi, IBM MQSeries web console login)
Same-week tag for CitrixBleed 2 (CVE-2025-5777)
Same-week tag: 'CitrixBleed 2' — Citrix NetScaler ADC/Gateway memory-disclosure (CVE-2025-5777), a high-profile KEV CVE
Jun 27, 2025
Tag and CVE activity charts now span 90 days
Viz: 90-day windows on tag activity and CVE tag activity charts
Jun 26, 2025
The autotagger pipeline produced its first end-to-end detection tag shipped to customers: coverage for CVE-2024-48072, written entirely by the AI tagging workflow. A new dedicated folder marks the start of a separate publishing surface for autotagger-sourced content. Notable as the first customer-visible artifact from a research-and-tagging pipeline that compresses the path from CVE disclosure to live detection coverage.
Deliver Feeds to Slack
Feeds: Slack as a delivery destination
Filter feeds by IP and CVE
Feeds: IP-level and CVE-level filtering on feed configurations
Refreshed X-server connection and Censys actor tags
Tag updates: X-server connection and Censys actor refreshed
Track delivery activity per feed
Feeds: per-feed delivery activity tracking
Jun 24, 2025
Added end-to-end concurrency to the Feeds delivery service so one slow customer webhook can no longer back up the whole pipeline. Header handling was consolidated per client and the outbound payload reshaped from a batched envelope to a single event per request. The pipeline now scales horizontally with destination count rather than serializing on the slowest endpoint.
Create an alert straight from the No-Results page
Viz: 'Create alert' button on the No-Results page — GNQL query pre-populated
New tag for nginx directory traversal
Detection content: nginx directory traversal tag
Same-month tag for Roundcube deserialization (CVE-2025-49113)
Same-month tag: Roundcube PHP object deserialization (CVE-2025-49113)
Jun 23, 2025
New tag for vBulletin template-engine flaw (CVE-2025-48828)
New tag: vBulletin template-engine vulnerability (CVE-2025-48828)
Jun 20, 2025
Page through all retrohunt results
Retrohunt: pagination on session queries — no more implicit cap on retrohunt result browsing
Retrohunt jobs now persist executed queries for retry and audit
Retrohunt: executed queries persisted on retrohunt jobs for retry and audit
Jun 18, 2025
Cleaner outbound headers and IP-classification-change events in Feeds
Feeds: cleaner outbound header format and IP-classification-change events in the FeedForm UI
New tag for Rockwell Automation (CVE-2023-2915)
Research tag: Rockwell Automation CVE-2023-2915
New tag for WireGuard handshake traffic
New tag: WireGuard handshake traffic
New tags for SQLi, DLL POST, Citrix and WordPress exploit attempts
Tag-authoring sprint, June 2025, part 2: SQLi, DLL POST, Citrix-environment, WordPress-admin exploit attempts
Test-webhook output trimmed to a concise result
Feeds: test-webhook output now returns a concise result instead of verbose response details
Jun 17, 2025
Migrated the Feeds delivery service from a serverless runtime to long-running containers. Eliminates cold starts and concurrency caps, and sets the stage for the in-memory entitlements cache and concurrency overhaul that landed later in the month. Customers see steadier delivery latencies and the platform team gets straightforward horizontal scaling.
Build GNQL queries by click-and-drag in Labs
Viz: GNQL Builder lands as a Labs experiment — click-and-drag GNQL query assembly
New tags for SharePoint XSS, Shadowserver and research tags
Detection tag batch (3): SharePoint XSS silent tag, Shadowserver actor refresh, goformQosClas research tag
Jun 16, 2025
Four customer-facing additions to Retrohunt: retrohunt jobs can now run against multiple detection tags at once (instead of one tag per job, with all matching tags recorded per file); an Autorun flag lets retrohunts auto-execute and auto-replay without manual approval; session queries now run asynchronously, with retrohunts returning immediately as QUERYING and transitioning to PENDING and RUNNING as work progresses; and time-range filters can now be applied directly to retrohunt jobs. A much tighter analyst workflow on historical traffic.
New tags for Netgear traversal and research POCs
Detection tag batch: Netgear directory traversal + research POC batch (Jun 12 queue)
Same-month tag for Infoblox NetMRI RCE (CVE-2025-32813)
Same-month tag: Infoblox NetMRI unauthenticated RCE (CVE-2025-32813)
Jun 13, 2025
Added field-exclusion capability to GNQL searches, with the new /v3/gnql/metadata endpoint as the first consumer. Callers can now request only the fields they care about, which means smaller response payloads, faster queries on large batches, and a way to tune response sizes against plan limits. Heavily tested to protect the existing /v3/gnql contract.
Retrohunt rule hits now surface source IPs in the API
Retrohunt: source IPs that hit retrohunt rules now surfaced in the API response
Six new detection tags for default logins, scanners, and proxies
Detection tag batch (6): Trilithic Viewpoint default-login, plupload scanner, Psiphon proxy, generic PHP DebugBar exposure, CVE-2021-26292, CVE typo fixes on two existing tags
Test a feed before saving it in the Visualizer
Viz Feeds UI: 'Test feed' affordance added, redundant chart hidden
Jun 12, 2025
Visualizer tokens now refresh before expiry to cut auth errors
Viz auth: tokens now refreshed before expiry — eliminates a class of auth-edge errors
Jun 11, 2025
Landed the Form Field Refresh design-system project: every form component across the Visualizer was refactored and restyled against the shared design system. Closes out a multi-month design-system push and gives every customer-facing surface a consistent input model.
Data License Agreement link added to the Sensors tab
Sensors tab: Data License Agreement link added alongside the EULA
Feed configuration now reflects your entitlements
Feeds: entitlement awareness wired into feed configuration
New same-week tag for CVE-2025-5086
Same-week tag: CVE-2025-5086
New tag for FlowiseAI unauthenticated API-key overwrite
Same-month tag: FlowiseAI unauthenticated API-key overwrite — early coverage for AI tooling vulns
Seven new detection tags for recon and info-disclosure activity
Detection tag batch (7): Firebase recon scanner, Postgres pg_hba.conf info-disclosure, Kyocera DoS activity, VICIdial recon, DWR test-page scanning, plus a nuclei-templates import
Jun 10, 2025
Five new detection tags including in-the-wild CVE exploitation
Detection tag batch (5): Ruijie NBR file upload, Weaver E-cology RCE, in-the-wild fake CVE-2023-42115 payload, CVE-2024-38473 exploitation, bulk research drop (Jun 9 queue)
Search suggestions now show the full facet list
Viz: search suggestions now show the full facet list rather than a truncated default
ValueChip clicks now wrap OR queries in parentheses to keep semantics correct
Viz: ValueChip clicks now wrap existing OR queries in parentheses to keep semantics correct
Jun 9, 2025
Eight new detection tags for scanners and CVE exploitation
Detection tag batch (8): Apollo login scanner, CVE-2023-2227, CVE-2022-35653, CVE-2015-2280, CVE-2023-4542, Fortinac actor refresh, Geoserver scanner refresh, exploratory Metasploit-module-conversion batch
New tag for Cisco-product Log4j scanner traffic
New tag: Cisco-product Log4j scanner traffic
New tag for Shenzhen Huashi telecom gateway RCE attempts
New tag: Shenzhen Huashi telecom gateway RCE attempts
Jun 6, 2025
Feed webhooks split into CVE-status and IP-classification routes
Feeds: webhook routes split into /cve-status-change and /ip-classification-change for separate tracking
Four new detection tags and tag fixes for recent CVEs
Detection tag batch (4): CVE-2025-47916, E-cology BSH-servlet tag fix, Moxa MXView CVE-2017-7455, Clinic's PMS CVE-2025-3096, command injection, Metasploit-conversion experiment
New same-week tag for CVE-2025-34027
Same-week tag: CVE-2025-34027
New tag for Infinitt PACS medical-imaging vulnerability
New tag: Infinitt PACS (medical-imaging) system vulnerability
Jun 5, 2025
Five new detection tags and CVE tag fixes
Detection tag batch (5): CVE-2011-4804, CVE-2024-12209, silent CVE-2023-0563, fixes to CVE-2019-7238 and HPE Edgeline authentication-bypass tags
Test a feed webhook before going live
Feeds: in-product 'test webhook' endpoint for validating destinations before going live
Jun 4, 2025
New silent tag for CVE-2024-12856 on Four-Faith routers
Silent tag: CVE-2024-12856 (Four-Faith routers)
New silent tag for MCP and SSE scanning against AI tooling
Silent tag: MCP (Model Context Protocol) and SSE scanning — first visibility on a new traffic shape against AI tooling
New silent tag for WordPress user-enumeration scanning
Silent tag: WordPress user-enumeration scanning
Jun 3, 2025
RIOT v2 management API OpenAPI docs now published
RIOT v2: management API OpenAPI docs published — first public-shape contract
Search regex now handles defanged IP literals
Viz: search regex now handles defanged IP literals (e.g. 1[.]2[.]3[.]4) — fewer copy-paste foot-guns for analysts
Jun 2, 2025
Re-architected the PCAP aggregator service so it is no longer pinned to a single machine. Capacity now scales horizontally — a foundational unlock for sustained growth in packet-capture customers and traffic volume.
EULA acknowledgement copy added to sensor deployment
Sensor deployment UI: EULA acknowledgement copy added
Four new detection tags including WordPress SQL injection
Detection tag batch (4): two WordPress SQL-injection vulnerabilities, CVE-2022-0666, CVE-2019-17444
New tag for CVE-2023-38950 ZKTeco path traversal
New tag: CVE-2023-38950 (ZKTeco path traversal)
Updated tag for CVE-2025-4632 on Samsung MagicInfo
Tag update: CVE-2025-4632 (Samsung MagicInfo)
May 30, 2025
New tags from the VulnCheck bulk detection drop
New tags: VulnCheck bulk detection drop
Same-day tag for actively exploited Cisco IOS XE RCE
Same-day tag: Cisco IOS XE Wireless Controller RCE (CVE-2025-20188) — actively exploited
May 29, 2025
Free-user navigation restored with upgrade prompts
Viz: free-user nav restored with upsell prompts and a clear upgrade path
May 28, 2025
The PCAP aggregator can now recover mid-flight state from disk after a restart, eliminating data loss during deployments or unexpected interruptions. Closes out a month of sustained reliability work.
Silent tags no longer appear in public tag endpoints
Silent tags filtered from all public tag endpoints — cleaner data surface
Verified users no longer see a stale unverified state
Fixed: email-verified users no longer see a stale unverified state
May 27, 2025
Feeds delivers near-real-time, event-driven notifications about critical threat activity directly to customer workflows. Advanced and Elite customers subscribe to curated event streams — IP Classification Change, CVE Status Change, and CVE Activity Spike — delivered via webhook so they land directly in SOAR platforms and automation pipelines. Instead of polling the API and knowing what to look for, security teams can automatically block newly malicious IPs the moment they're detected, prioritize patching when a CVE moves into active exploitation, or trigger a playbook when exploitation volume spikes. From first sensor packet to actionable signal in under 30 seconds.
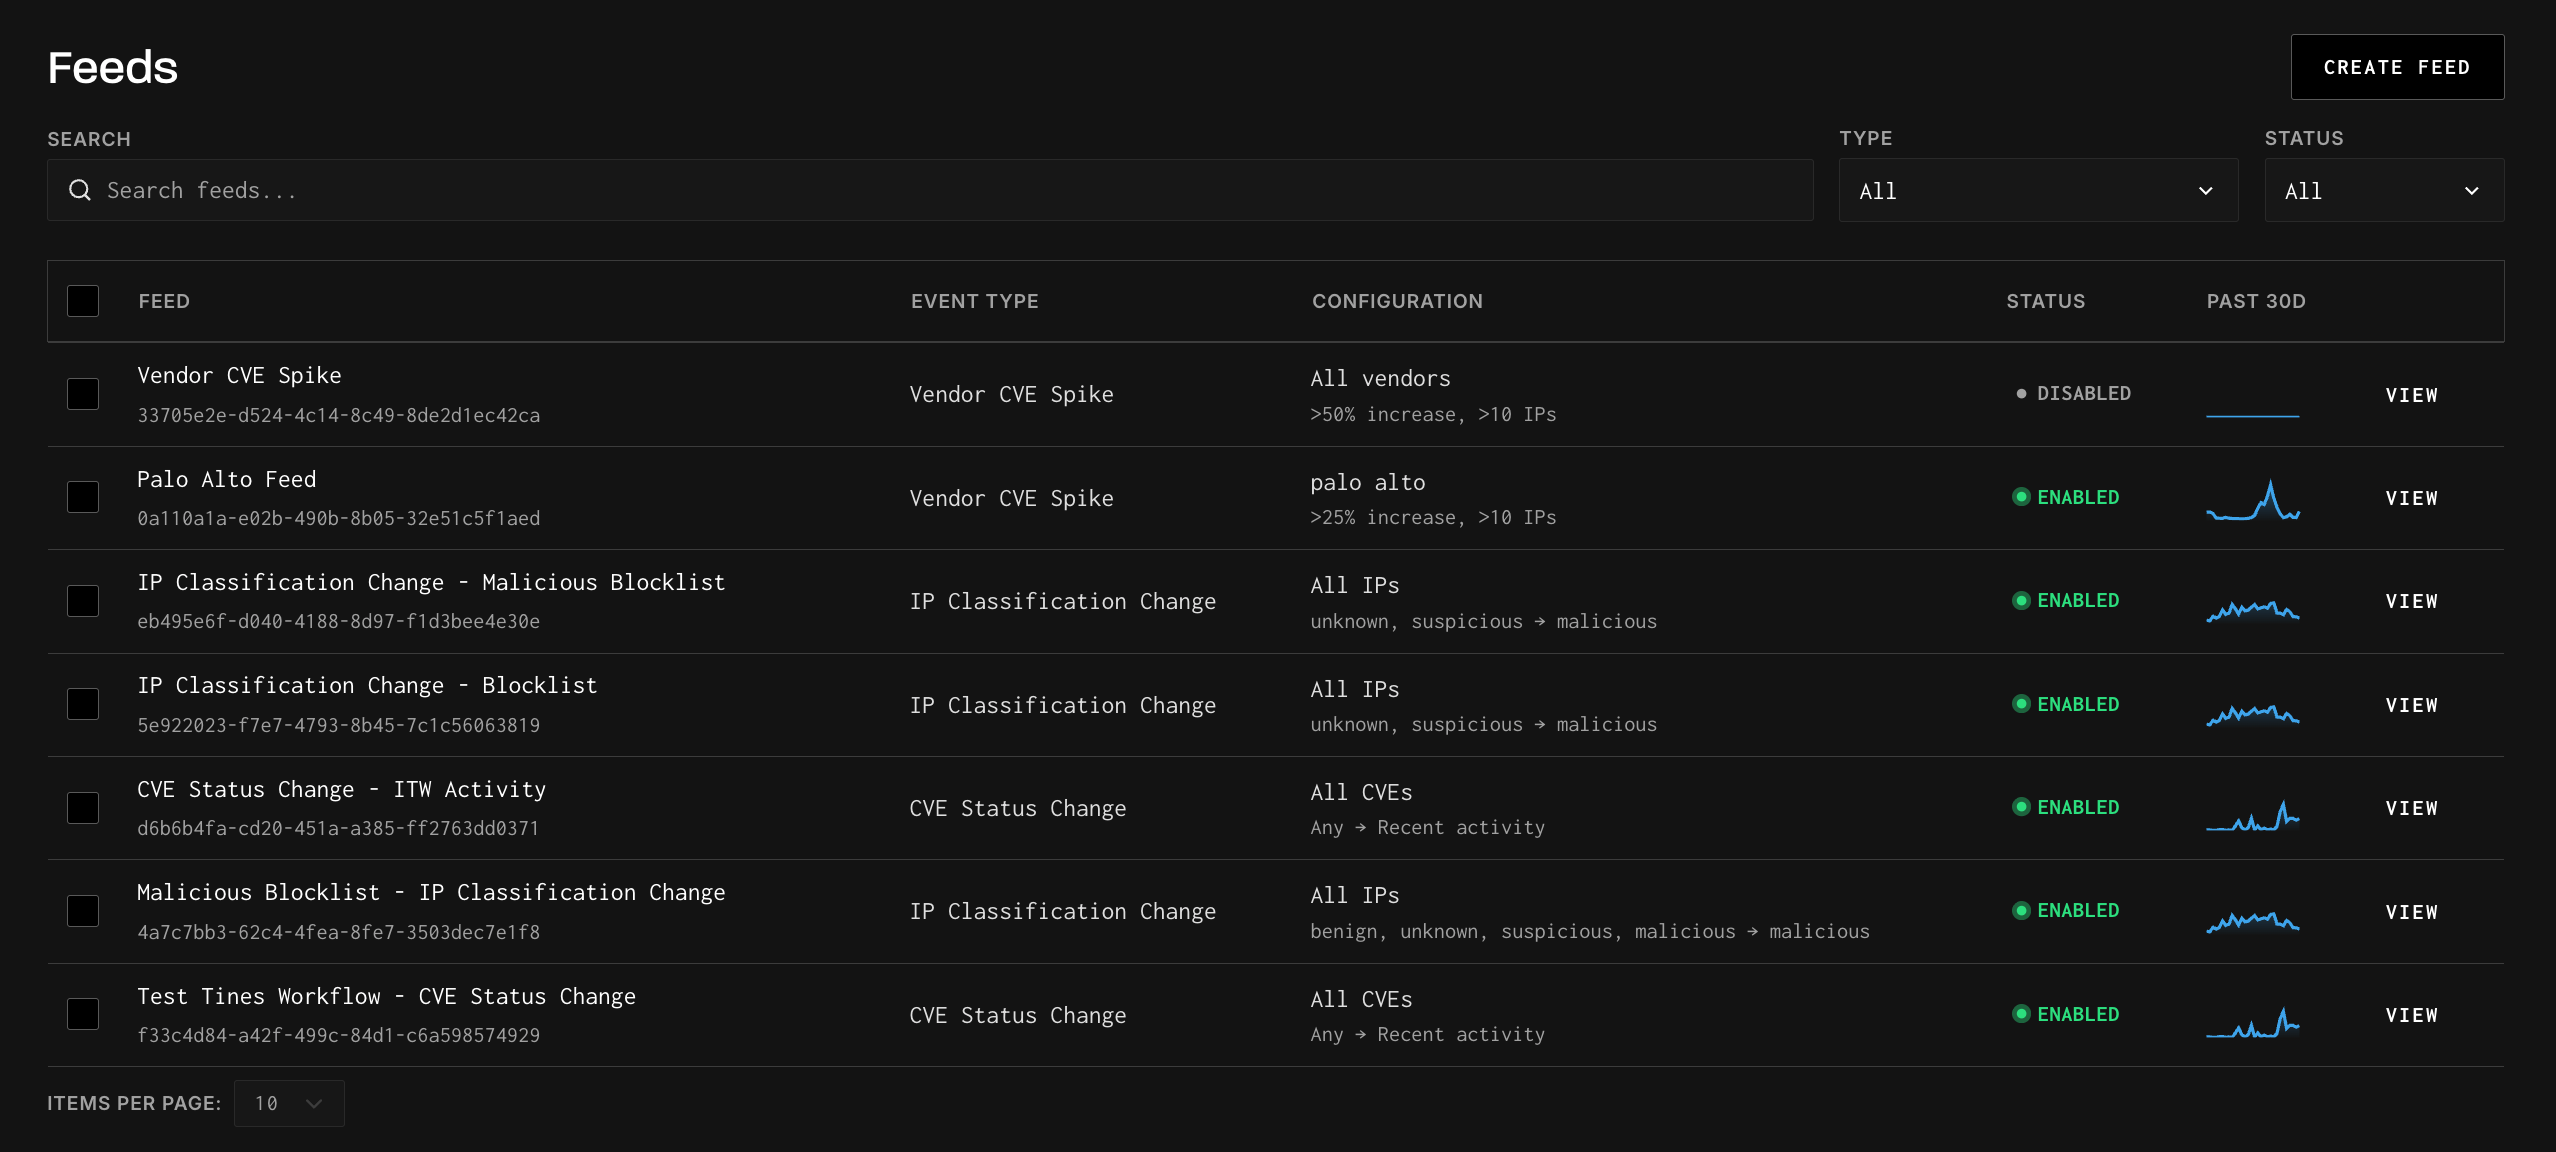
May 23, 2025
New tags for Synology, SonicWall GMS, and Nortek exploits
New tags: Synology DiskStation null-byte exploit, SonicWall GMS XMLRPC unauth RCE, Nortek device RCE
Visualizer now respects rate-limit responses without retrying
Fixed: Viz now respects rate-limit responses — no silent query retries
May 22, 2025
Same-week tag for Fortinet RCE (CVE-2025-32756)
Same-week tag: Fortinet RCE (CVE-2025-32756)
May 21, 2025
Analysis stats percentage calculation corrected
Fixed: Analysis stats percentage calculation corrected
Customers alerted ahead of navigation simplification
'Analysis is moving' alerts — customers notified ahead of nav simplification
May 20, 2025
Per-endpoint rate limiting is now active across all major API surfaces — GNQL, `/v3/ip`, analyze, RIOT, and tags-search. Entitled customers operate under higher limits; free-tier and unauthenticated users have appropriate caps. Designed to protect service quality and reinforce plan differentiation.
May 19, 2025
JA4 TLS fingerprints are now published into the GNQL search index and surfaced in the Visualizer's IP Summary and pivot facets. Analysts can query and pivot on JA4 values alongside existing JA3 and HASSH fingerprints — adding another dimension for identifying and tracking scanner infrastructure.
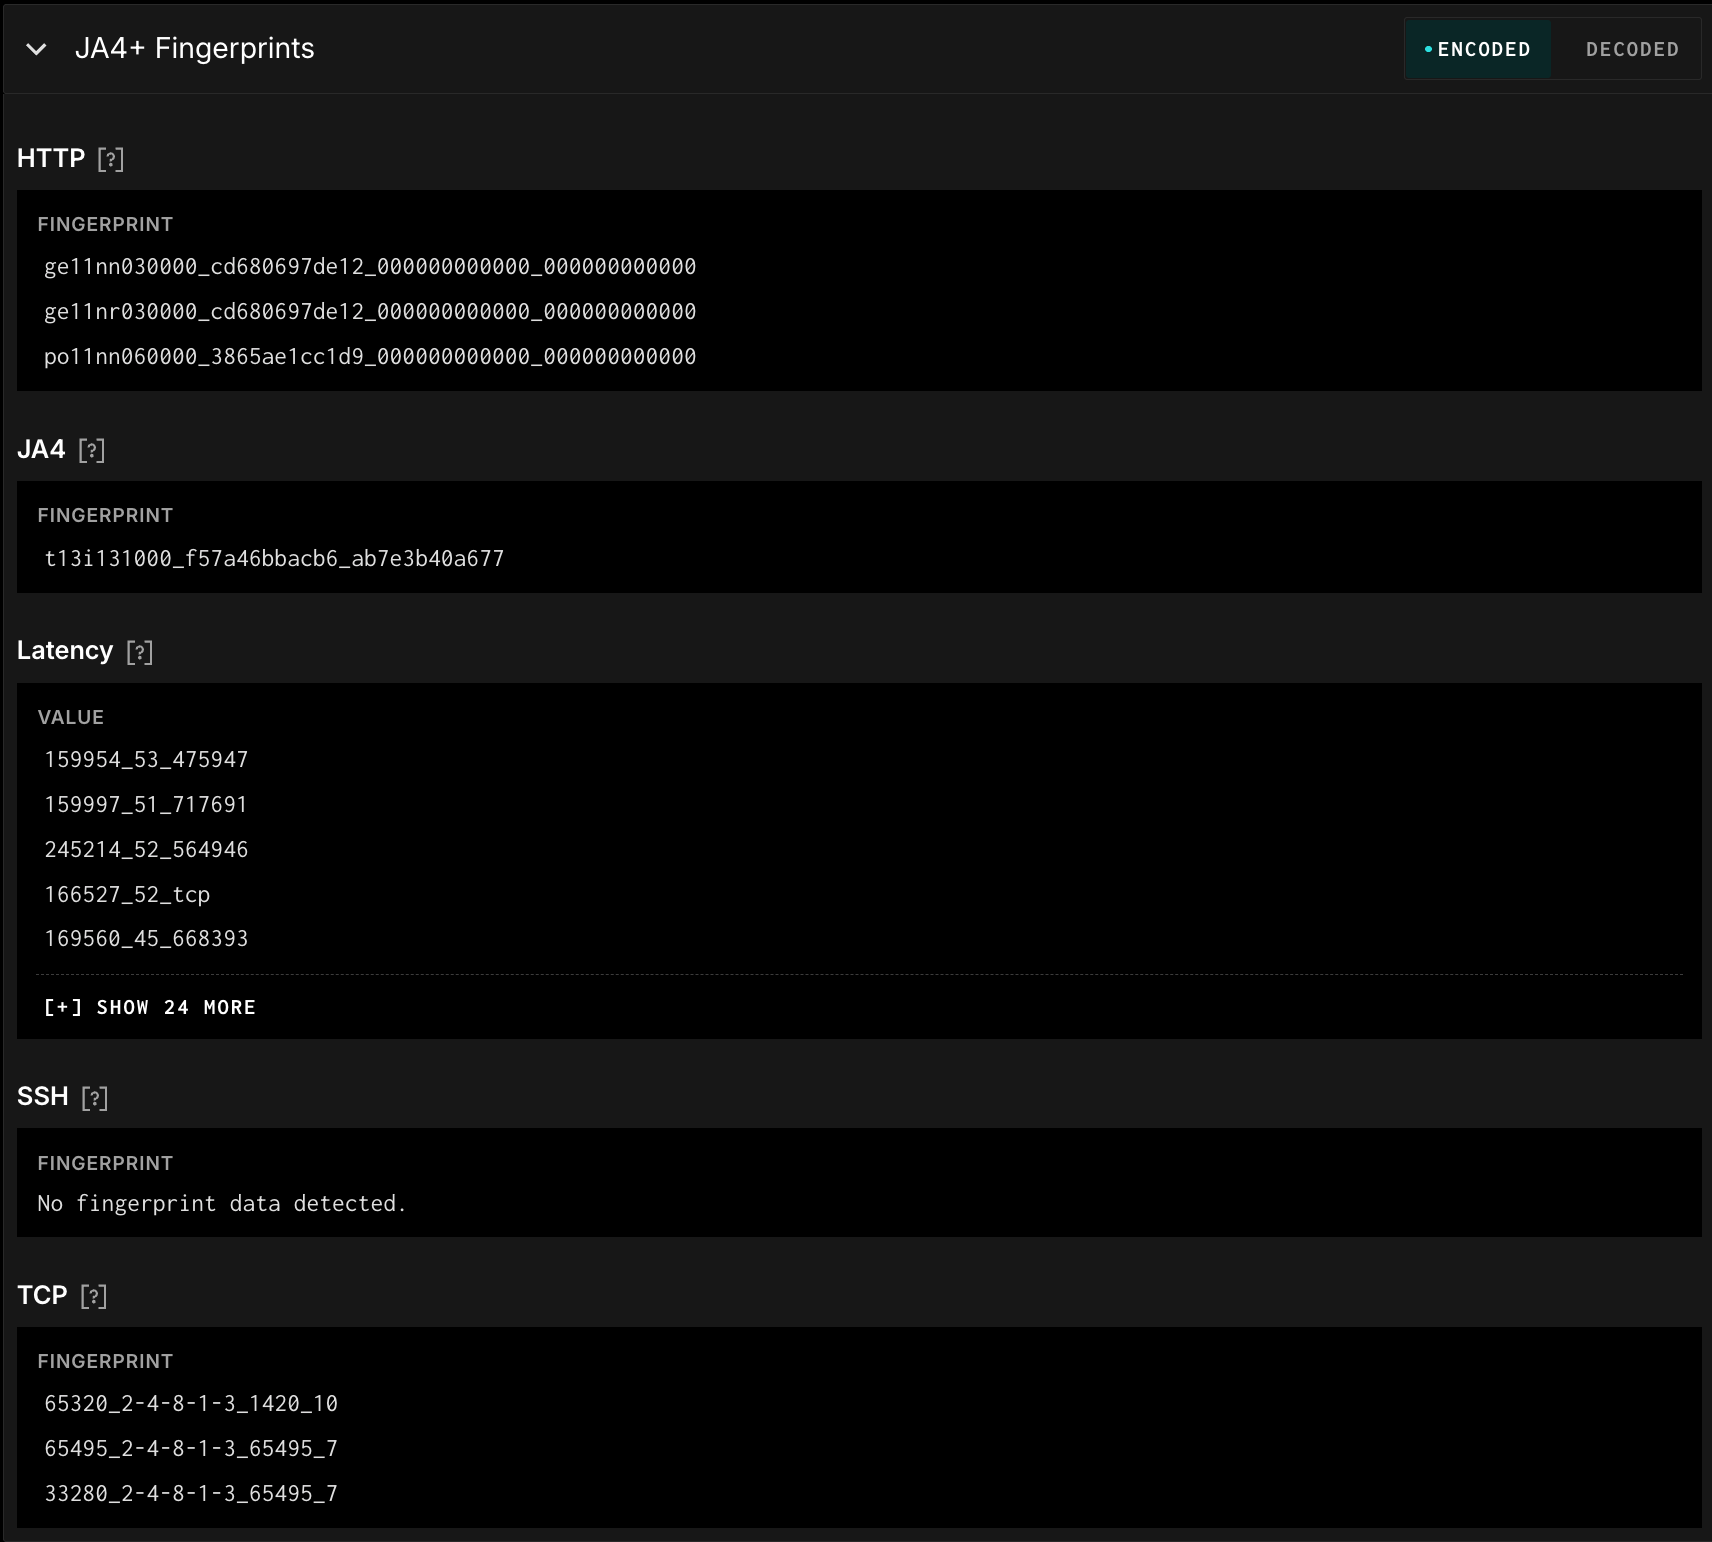
New tag detects $IFS bash RCE payload obfuscation
New tag: $IFS bash RCE payload obfuscation detection
May 16, 2025
New tag detects DICOM medical-imaging port scanners
New tag: DICOM protocol scanner (medical-imaging ports)
Same-week tag for Ivanti EPMM RCE (CVE-2025-4428)
Same-week tag: Ivanti Endpoint Manager Mobile RCE (CVE-2025-4428)
May 15, 2025
Free-tier enforcement is now active across GNQL search, bulk IP, tags, and RIOT. Customers at or over their tier limit see contextual upgrade prompts. The first time the product actively steers users toward the right plan tier.
New tags for D-Link D-View and GeoVision injection
New tags: D-Link D-View (CVE-2023-5074), GeoVision command injection (CVE-2024-11120), plus a bulk research batch
Saved GNQL queries no longer return bad-query errors
Fixed: GNQL regression — customer-saved queries no longer return bad-query errors
Workspace invite flow now auto-provisions with cleaner onboarding
Workspace invite flow reworked — new auto-provisioning with cleaner onboarding steps
May 13, 2025
Wired entitlement checks across every major search surface — GNQL, CVE search, Tags Search, Trends, Analysis, and Bulk IP — backed by a consolidated billing integration. Gives the product team direct control over which capabilities are available at each plan tier, with consistent enforcement across all entry points.
New tag detects SysAid pre-auth RCE chain (CVE-2025-2775)
New tag: SysAid on-prem pre-auth RCE chain (CVE-2025-2775)
May 12, 2025
Feeds emit IP classification change events with old and new state
Feeds emit an IP classification-change event carrying the old and new state on every change
May 9, 2025
Feeds track continuous per-IP state changes over time
Feeds now track continuous per-IP state — Actor, Classification, Spoofable, and First/Last Seen
May 8, 2025
Corrected sensor install instructions in onboarding
Fixed: sensor install instructions corrected in Viz onboarding
SSO login no longer fails on malformed group data
Fixed: SSO login no longer fails when encountering malformed group data
May 7, 2025
New tag detects FoxCMS command injection RCE (CVE-2025-29306)
New tag: FoxCMS command injection RCE (CVE-2025-29306)
May 6, 2025
IP Timeline fields no longer render empty for some customers
Fixed: IP Timeline fields no longer silently empty for some customers
New tag detects Hikvision security management RCE
New tag: Hikvision integrated security management RCE
May 2, 2025
IP Details page hardened against malformed input
Fixed: IP Details page hardened against malformed or non-IP input
SSO users without a workspace are now handled gracefully
Fixed: SSO users without a workspace assignment are now handled gracefully
May 1, 2025
New tags for Craft CMS RCE and Landray OA RCE
New tags: Craft CMS RCE (CVE-2025-32432), Landray OA RCE, CVE-2024-7151, priority-queue batch (12 CMS tags)
Apr 30, 2025
New tags from the VulnCheck bulk detection drop
New tags: VulnCheck bulk detection drop
Apr 29, 2025
Refreshed workspace navigation
Workspace navigation refreshed
Apr 28, 2025
Rebuilt the PCAP aggregator for reliability and cost: migrated from in-memory to file-based storage with explicit flush-to-disk guarantees, introduced ordered chunk retention with automatic cleanup of aged data, and rightsized the underlying storage — cutting cost while improving data durability for packet-capture customers.
Same-week tag for SAP NetWeaver zero-day (CVE-2025-31324)
Same-week tag: SAP NetWeaver Visual Composer zero-day (CVE-2025-31324, CVSS 10.0)
Apr 25, 2025
New tags for Adobe Experience Manager bypass
New tags: Adobe Experience Manager bypass and CVE-2024-30620
Apr 24, 2025
IP Details cleaned up by removing stale fields
IP Details cleaned up — stale and redundant fields removed
New Labs experiment: WatchGOG
New Labs experiment: WatchGOG
New tag detects CVE-2025-34028
New tag: CVE-2025-34028
Apr 23, 2025
Clearer API error messages and updated auth package
Auth package updated and API error messages improved
New tag detects Langflow activity
New tag: Langflow
Apr 22, 2025
New tag detects BPFDoor controller activity
New tag: BPFDoor controller activity (Chinese-linked APT backdoor)
Apr 21, 2025
Long-running API requests no longer time out at the load balancer
Fixed: long-running API requests no longer time out at the load balancer
New tag detects Netgear NMS300 file upload (CVE-2023-38098)
New tag: Netgear NMS300 arbitrary file upload (CVE-2023-38098)
Apr 18, 2025
New tag detects Gladinet CentreStack hard-coded key (CVE-2025-30406)
New tag: Gladinet CentreStack hard-coded key (CVE-2025-30406, CISA KEV)
New tags detect CVE-2025-22960 and CVE-2025-22961
New tags: CVE-2025-22960 and CVE-2025-22961
Apr 17, 2025
Faster Visualizer load times via optimized blocklist and unauthenticated calls
Visualizer load time improved — blocklist and unauthenticated calls optimized
Search and filter Labs experiments to find them faster
Labs search and filtering — find experiments faster
SSO now accepts only vetted identity providers
SSO provider allowlist hardened — only vetted identity providers accepted
Apr 16, 2025
New tag detects Apache Camel CVE-2025-27637
New tag: Apache Camel CVE-2025-27637
Per-page settings now persist across sessions
Visualizer: per-page settings now persist across sessions
Apr 15, 2025
Billing entitlements now work when corporate networks block scripts
Fixed: billing entitlements now work even when client-side scripts are blocked on corporate networks
New tags detect Arcadyan TLV, ZendTo, and Kentico
New tags: Arcadyan TLV, ZendTo, Kentico (2)
Plan page restored and API key page refreshed
Plan page restored and API key page refreshed
RIOT dataset refreshed with current Qualys scanner IPs
RIOT dataset: Qualys scanner IPs refreshed
Apr 14, 2025
V3 consolidates five separate V2 IP endpoints into one streamlined endpoint. Noise and RIOT intelligence are returned together in a single response — no more double lookups to check whether an IP is a known scanner. ~25 new enrichment fields added (including JA4), fast and full response modes for lightweight vs. full-context workflows, and entitlement-aware responses that surface clear upgrade prompts when a customer queries a field above their plan tier.
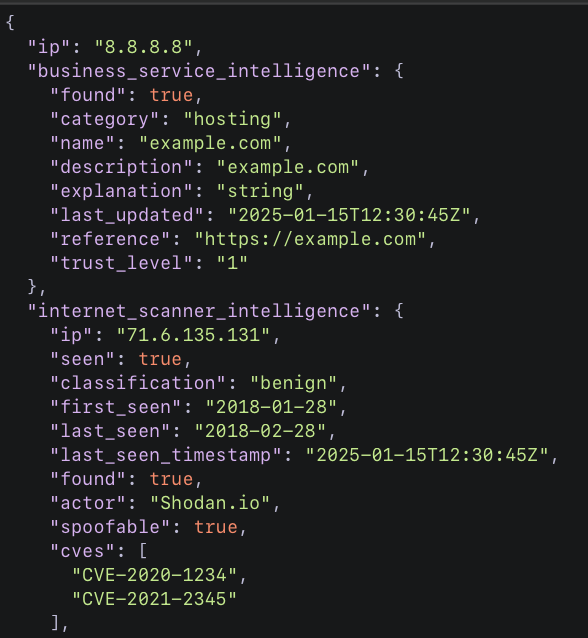
Apr 11, 2025
New tag detects D-Link/TRENDnet gena.cgi buffer overflow
New tag: D-Link/TRENDnet gena.cgi buffer overflow
Standardized Visualizer page layouts for a consistent experience
Visualizer page layouts standardized for a consistent experience
Apr 10, 2025
Detection report outputs now use secure pre-signed URLs
Detection reports: outputs now use secure pre-signed URLs
Apr 9, 2025
New tag detects HTTP Referrer header probing
New tag: HTTP Referrer header probing
PCAP date picker now works in Firefox
Fixed: PCAP date picker now works in Firefox (customer-reported)
Apr 8, 2025
New Labs experiment: Technology Tags heatmap
New Labs experiment: Technology Tags heatmap
New tag detects CasaOS login bruteforce attempts
New tag: casaOS login bruteforce detection
New tags detect Vite file disclosure (CVE-2025-30208) and Royal Elementor file access
New tags: Vite arbitrary file disclosure (CVE-2025-30208), WordPress Royal Elementor arbitrary file
Apr 7, 2025
SSO is now fully wired into production end-to-end. Enterprise customers authenticate via their identity provider, with workspace access automatically assigned from group membership. Backed by a new SSO service, the Auth0 management API, and an event-driven pipeline — built on the self-service SSO foundation shipped in March. The SSO feature flag has been removed, making SSO broadly available to enterprise accounts.
New tags added from Nuclei templates
New tags: 2 Nuclei template-sourced detections
Apr 4, 2025
New tags detect CVE-2024-46938 and Umbraco SSRF
New tags: CVE-2024-46938, Umbraco SSRF
Same-day tag detects Ivanti Connect Secure RCE (CVE-2025-22457)
Same-day tag: Ivanti Connect Secure RCE (CVE-2025-22457)
Apr 3, 2025
Status page migrated to Incident.io
Status page migrated to Incident.io
Apr 2, 2025
New workspaces no longer carry a 'Personal:' name prefix
New accounts: workspace name no longer prefixed 'Personal:'
vBulletin tag and CVE-2023-27997 detection refined
Detection tuning: VBULLETIN tag updated, CVE-2023-27997 match fix
Apr 1, 2025
Closed out the SQL→Suricata conversion program that ran from January through April, retiring 25+ legacy detection rules in the final batch. Every GreyNoise detection tag now runs on the modern Suricata-based detection engine — faster, more maintainable, and easier to extend with new CVE coverage.
New tag detects ManageEngine Desktop Central deserialization RCE
New tag: ManageEngine Desktop Central deserialization RCE
New tag detects NAKIVO Backup & Replication activity
New tag: NAKIVO Backup & Replication
Mar 31, 2025
The month the new data pipeline stopped running alongside the legacy system and fully took over. All IP enrichment data now flows exclusively through the new pipeline, with new transforms for tags, destination metadata, web paths, and user-agents. This is the infrastructure milestone that makes every new enrichment field — RDNS, HASSH, JA3 fingerprints, source ports — reliably available at production scale.
Mar 28, 2025
New tag detects CVE-2019-9874
New tag: CVE-2019-9874
Mar 27, 2025
Introduced a Labs section in the Visualizer where experimental capabilities are made available to customers ahead of general release. Includes dedicated navigation, entitlement gating, and the first wave of experiments — giving engaged users a reason to explore the product edge and giving the team a structured path to validate new features.
New tag detects CVE-2018-20334
New tag: CVE-2018-20334
Mar 25, 2025
Same-week tag detects IngressNightmare ingress-nginx RCE
Same-week tag: IngressNightmare — Kubernetes ingress-nginx critical RCE (CVE-2025-1974)
Same-week tag detects Next.js middleware bypass
Same-week tag: Next.js authorization middleware bypass (CVE-2025-29927)
Mar 24, 2025
The IP Timeline replaces the old Summary tab as the first thing analysts see when they open any IP in the Visualizer. With reorganized activity tabs and plan-tier access gating, the most data-rich view is now front and center — reinforcing the value of deeper plan tiers every time an analyst investigates an IP.
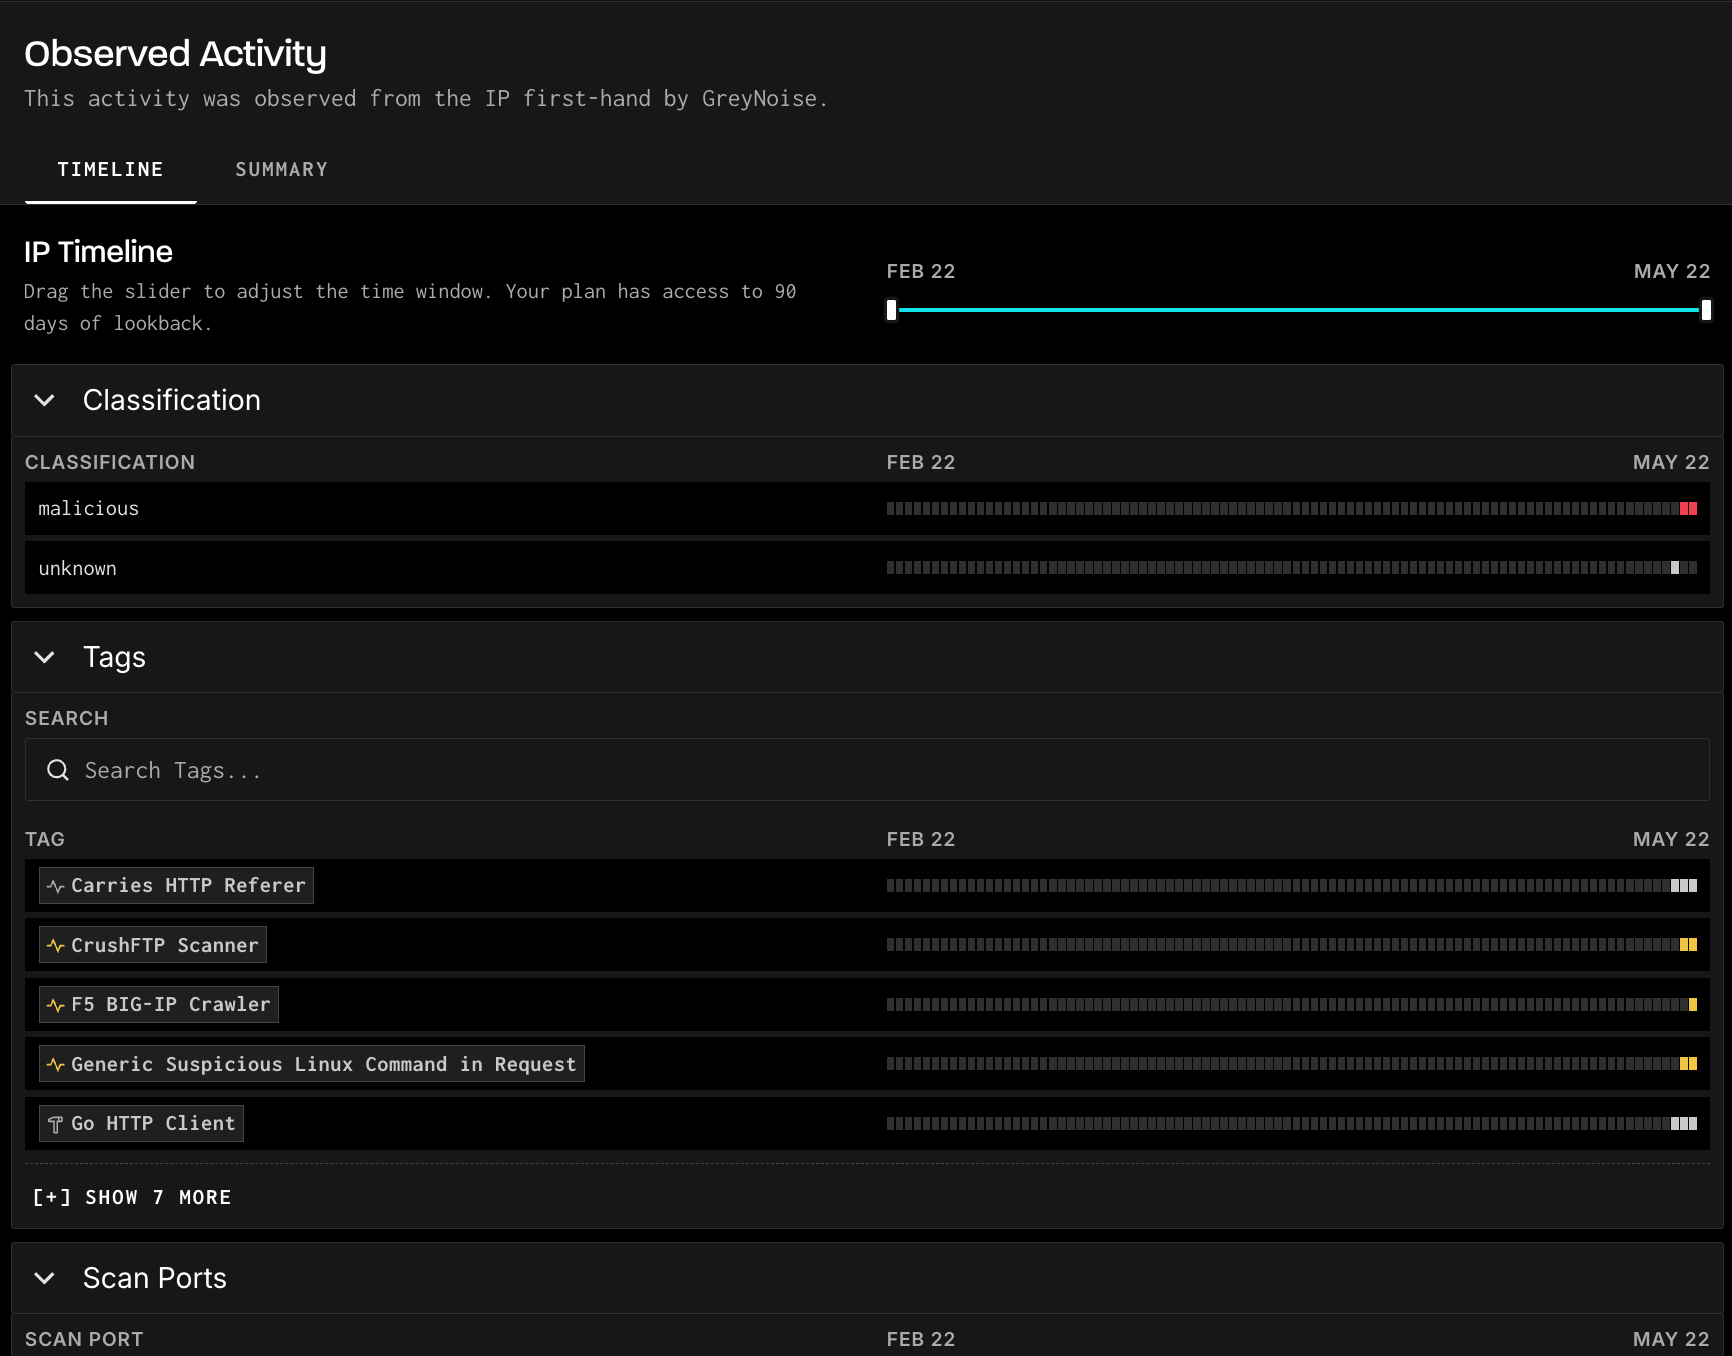
New tag detects Netatalk buffer overflow
New tag: Netatalk stack buffer overflow (CVE-2022-23125)
New tag detects Sitecore XP deserialization RCE
New tag: Sitecore XP deserialization RCE (CVE-2025-27218)
New tags add same-day coverage for 5 Tenda router CVEs
New tags: Tenda router vulnerability cluster — 5 CVEs, same-day coverage
Mar 20, 2025
Plan-based access gates wired across IP Timeline, Destination Country data, API pages, and Labs features. On the API side, HASSH + JA3 fingerprints, CVE correlation, and source-port analysis are now plan-gated — giving direct levers to monetize data depth and enforce tier differentiation across the product surface.
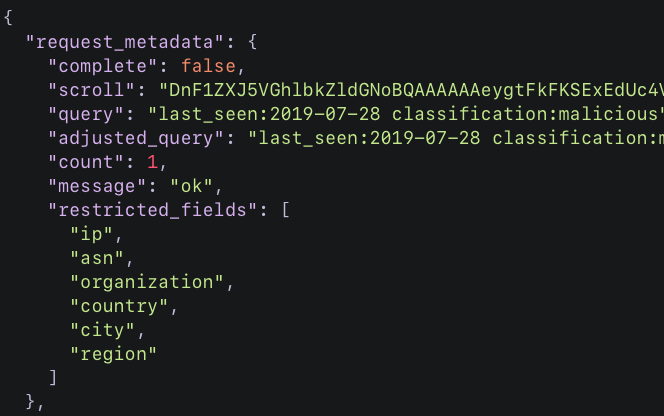
Mar 18, 2025
New tag detects Apache Tomcat partial PUT RCE
New tag: Apache Tomcat partial PUT RCE (CVE-2025-24813)
New tag detects CVE-2024-3408
New tag: CVE-2024-3408
Mar 14, 2025
New tags detect GLPI SQL injection and RCE
New tags: GLPI SQL injection and RCE
New tags detect Zyxel device information leaks
New tags: Zyxel device information-leak detections
Mar 13, 2025
Shipped the backend foundation for per-sensor profile customization: new backend storage and an admin endpoint that let operators assign custom profiles to individual sensors. The first building block toward a bring-your-own-profile capability for enterprise customers who want to tailor how GreyNoise appears on the internet.
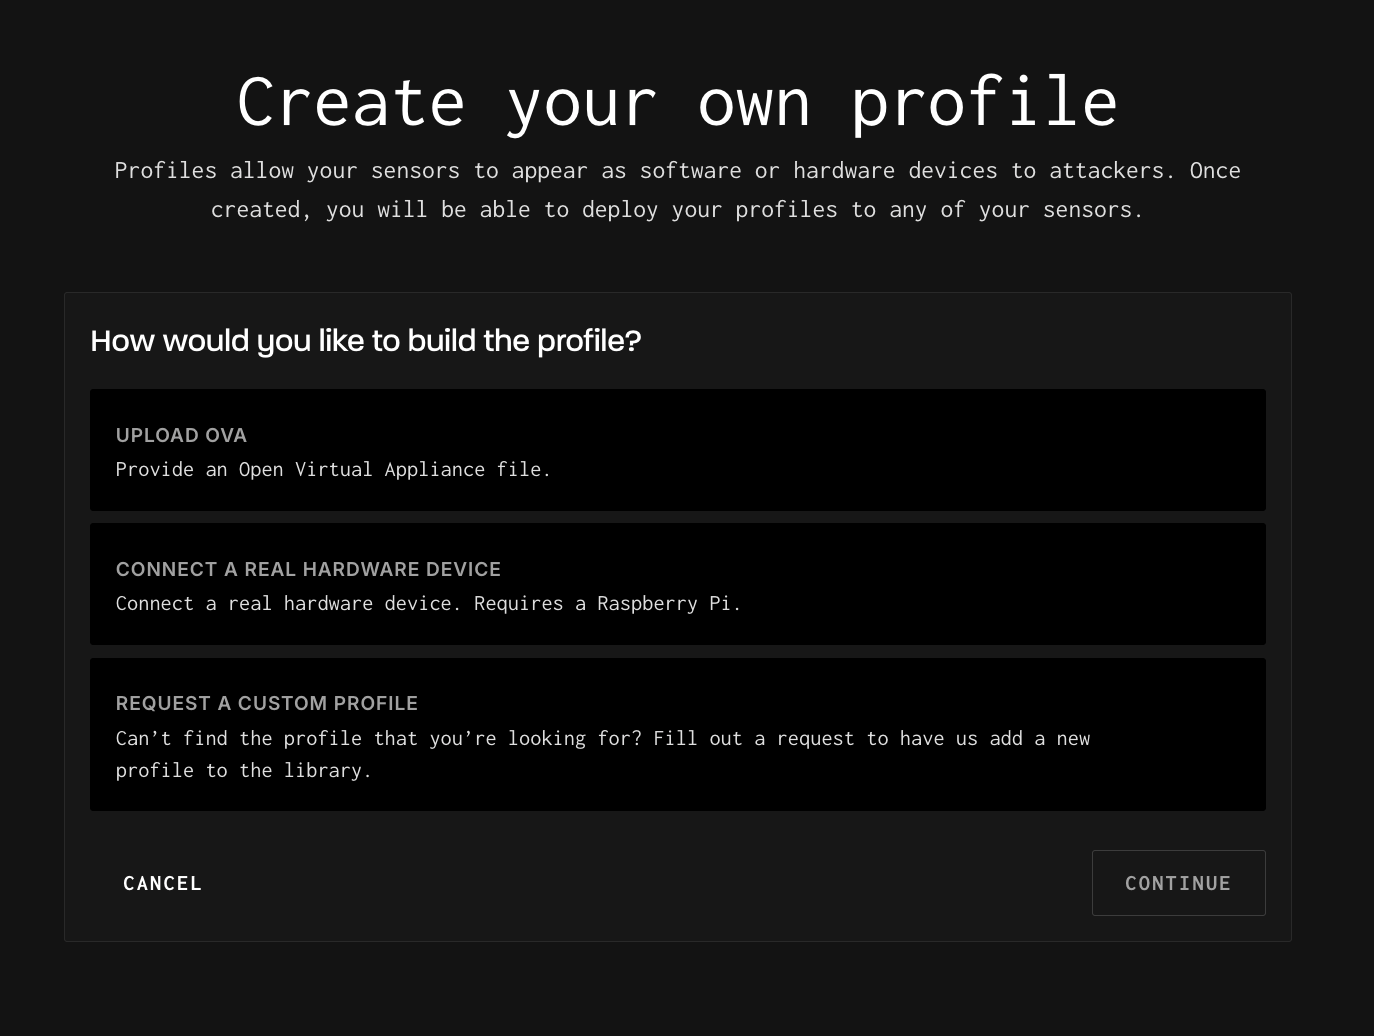
Mar 12, 2025
New tag detects CVE-2018-12998
New tag: CVE-2018-12998
Mar 7, 2025
New tag detects Cisco RV-series command injection
New tag: Cisco RV-series command injection
New tags detect CVE-2024-21793 and CVE-2024-26026
New tags: CVE-2024-21793 and CVE-2024-26026
Mar 5, 2025
New GNQL endpoint replaces the legacy IP-details path and is wired into the API. The customer-visible front of the enrichment-pipeline rollout — new schema, new fields, new entitlements, new UI.
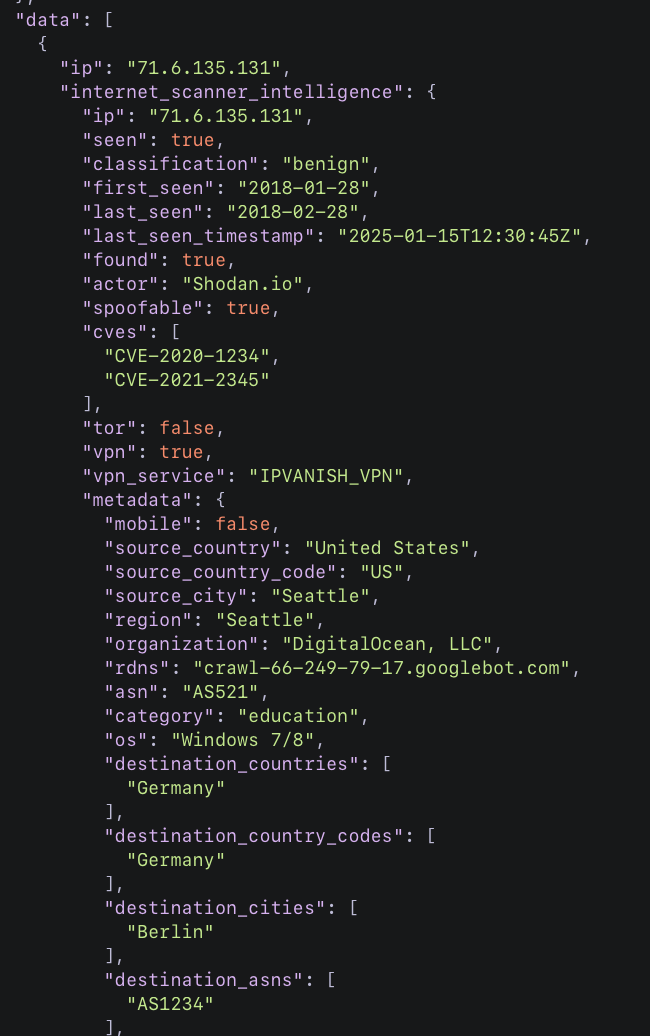
New tag detects iceshrimp/calckey SQL injection
New tag: iceshrimp/calckey SQL injection
New tag detects WeGIA path traversal
New tag: WeGIA path traversal
Mar 3, 2025
New tag for Joomla! local file inclusion
New tag: Joomla! local file inclusion
Feb 28, 2025
Launched a new v3 IP Details API exposing a richer set of fields: RDNS Validated, RDNS Parent, Domain, and source ports — all gated by plan tier so customers see deeper context as they upgrade. Backed by a dedicated service layer and updated across the Visualizer, this is the customer-facing payoff of the new data pipeline.
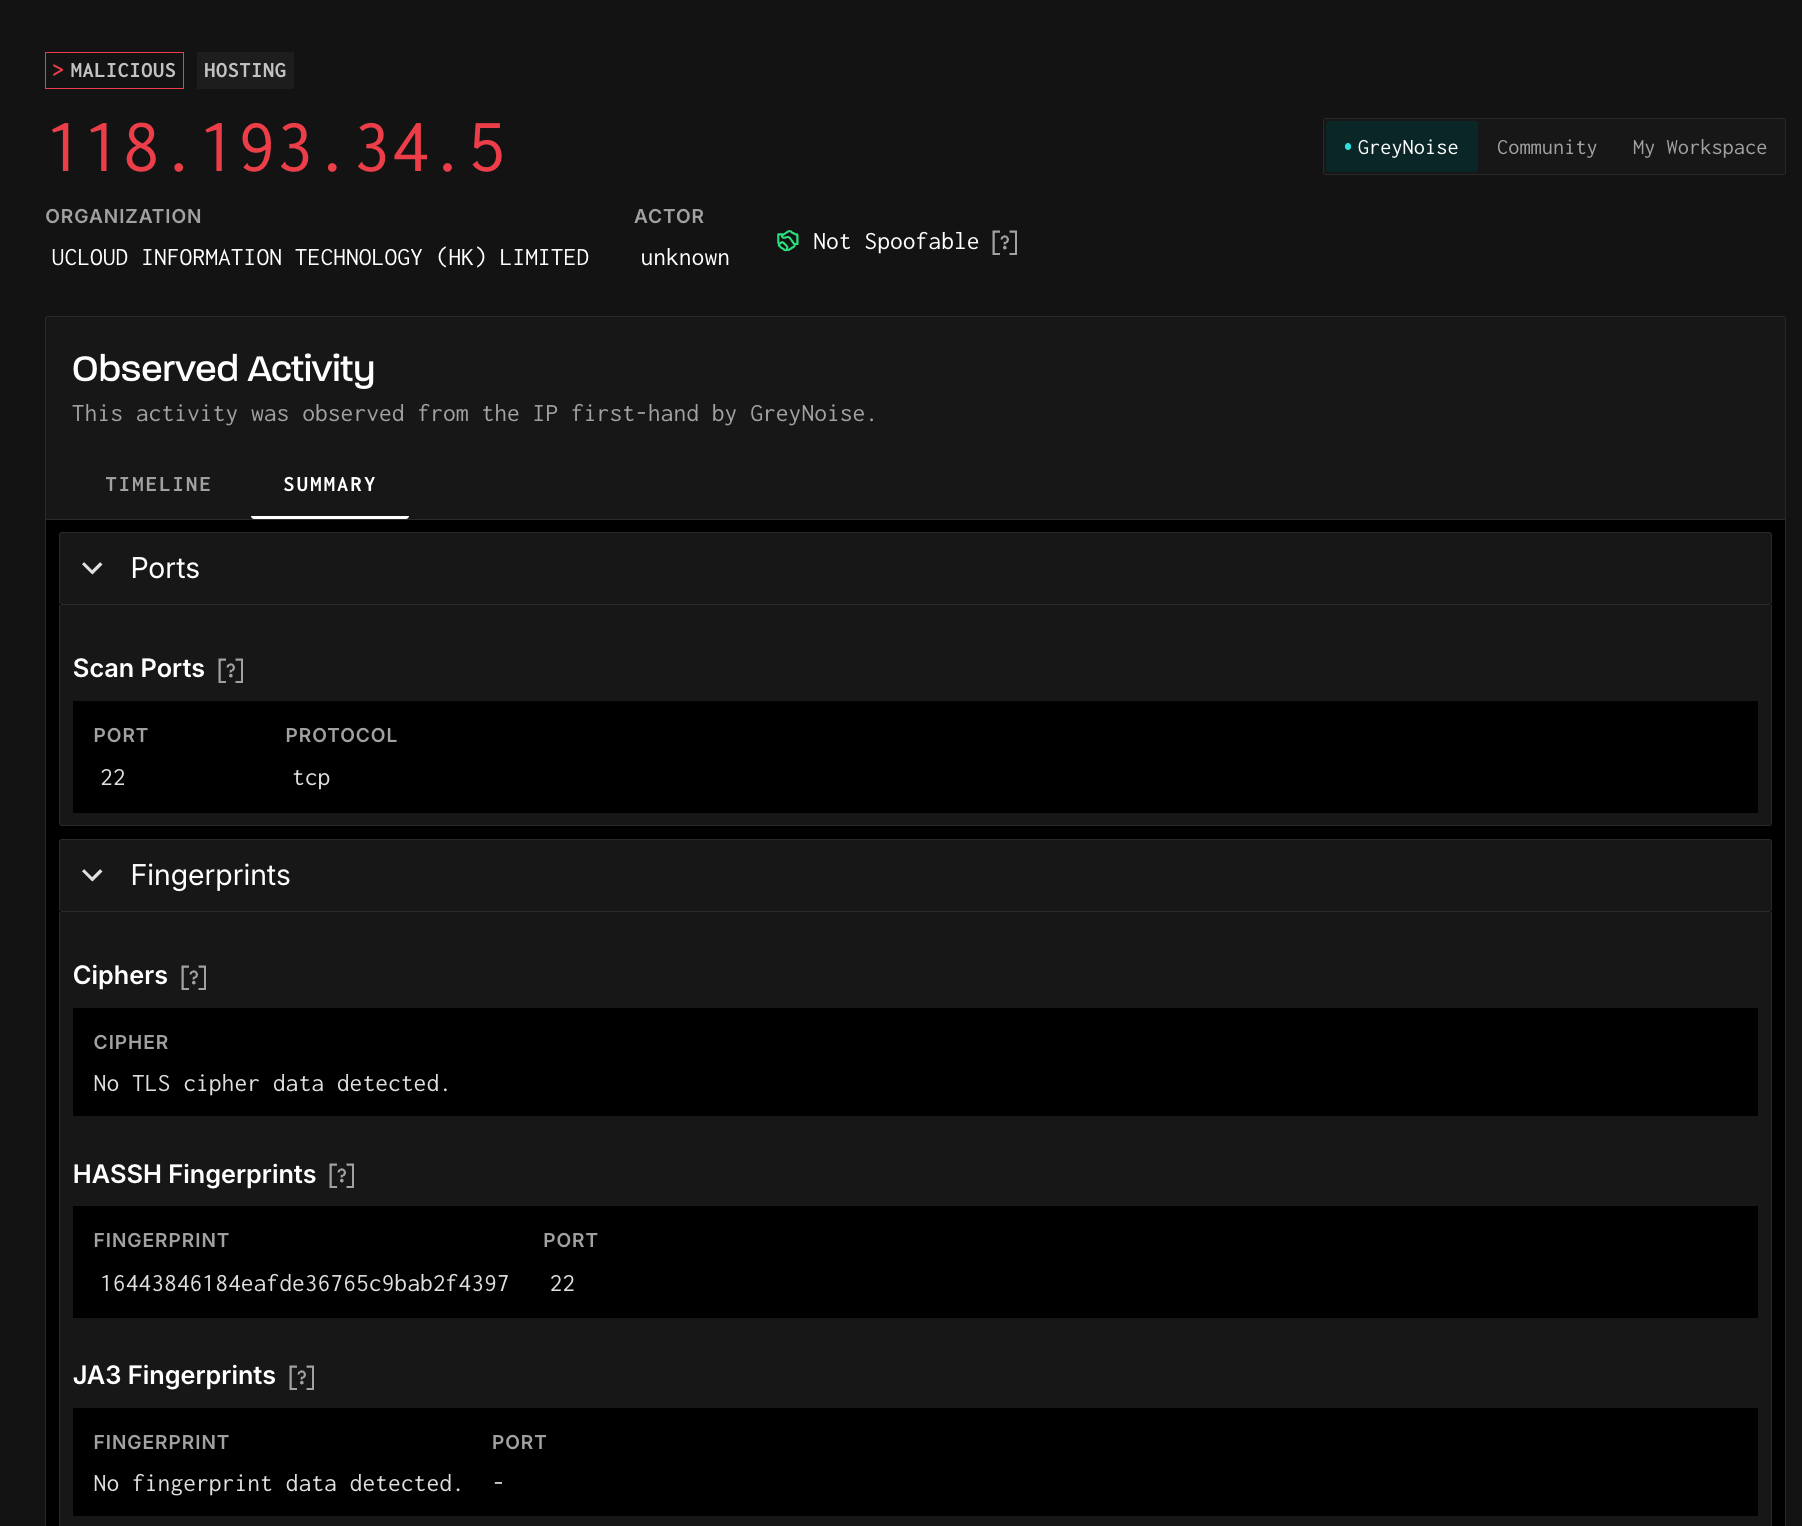
New tag for generic SAML authentication probing
New tag: Generic SAML authentication probing
New tag for Modat actor detection
New tag: Modat actor detection
Feb 27, 2025
Closed out a multi-quarter migration to the new sensor fleet. The legacy sensor infrastructure was fully decommissioned — every sensor is now running on the new stack. Includes new tooling for managing sensors at scale and streaming metrics for real-time fleet visibility.
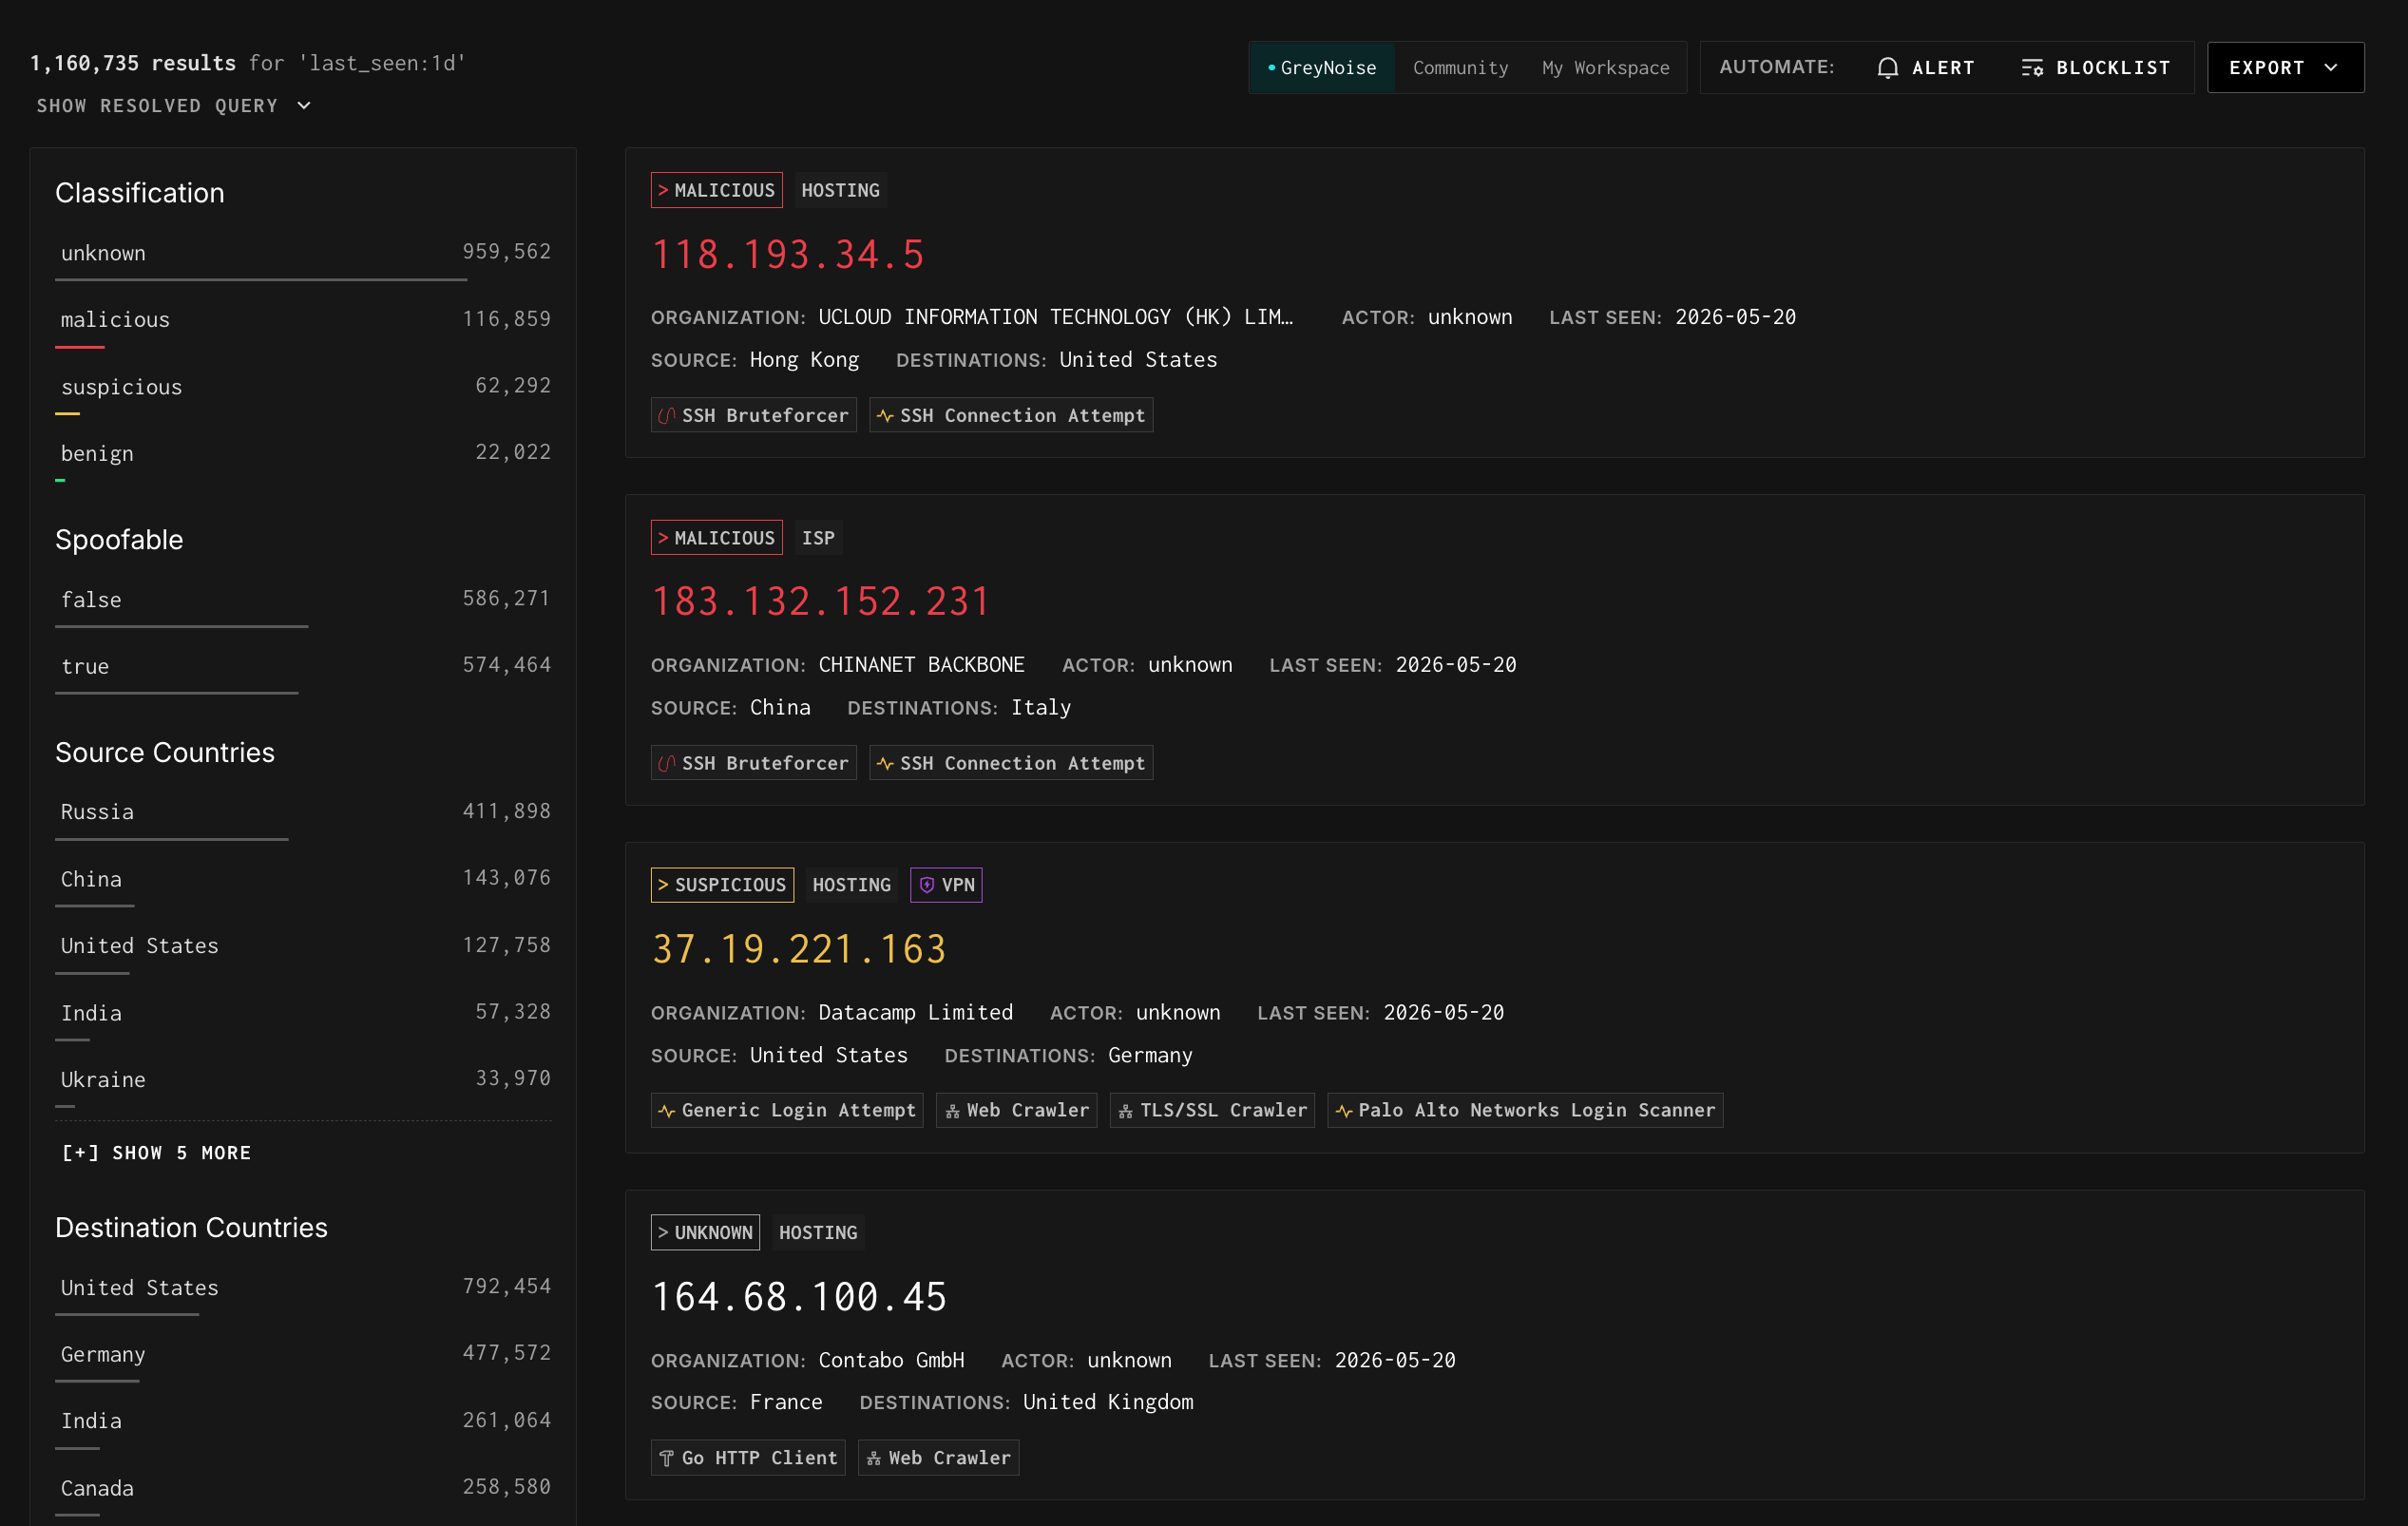
New tag for OPC DA handshake scanner
New tag: OPC DA handshake scanner (ICS protocol detection)
Feb 26, 2025
New tag for Adobe ColdFusion BlazeDS deserialization
New tag: Adobe ColdFusion BlazeDS deserialization (CVE-2017-3066, CISA KEV)
New tag for CVE-2025-25343
New tag: CVE-2025-25343
New tag for MITRE Caldera dynamic-agent RCE
New tag: MITRE Caldera dynamic-agent RCE (CVE-2025-27364)
Feb 25, 2025
Source ports are now a queryable field in GNQL for Threat Hunting customers, powered by the new data pipeline. Gives analysts a new dimension to hunt laterally-moving threats and correlate scan behavior across port ranges.
Zero-downtime deploys end Visualizer interruptions on release
Zero-downtime deploys — eliminated Visualizer interruption on every release
Feb 24, 2025
IP timeline API error regression fixed
Fixed: IP timeline API error regression (customer-reported)
Feb 21, 2025
CVE data now refreshes fully every hour
CVE data freshness restored — hourly full refresh
New tag for Zyxel NAS RCE
New tag: Zyxel NAS RCE (CVE-2024-29974)
Semicolons in IP queries no longer break search
Fixed: semicolons in IP queries no longer break search
Visualizer dates now display in UTC by default
Visualizer dates now display in UTC by default
Feb 20, 2025
New tag for Apache Superset authentication bypass
New tag: Apache Superset authentication bypass (CVE-2023-27524)
Feb 19, 2025
New tag for BeyondTrust PRA/RS unauthenticated RCE
New tag: BeyondTrust PRA/RS unauthenticated RCE (CVE-2024-12356, CISA KEV)
Feb 14, 2025
Legacy alerts removed in favor of Alerts v2
Legacy alerts removed — fully replaced by Alerts v2
New tags for Apache Storm, Pyspider, and FUXA exploits
New tags: Apache Storm API access, Pyspider debug endpoint, FUXA command execution
New tags for Roxy Fileman, Planon, and Trend Micro exploits
New tags: Roxy Fileman file upload, Planon XSS, Trend Micro file-delete exploit
Feb 13, 2025
New tags for Apache Tomcat and RDP bruteforce activity
New tags: Apache Tomcat bruteforce and RDP bruteforce detections
Same-day tag for Palo Alto PAN-OS authentication bypass
Same-day tag: Palo Alto PAN-OS authentication bypass (CVE-2025-0108)
Feb 12, 2025
New tags for Build Your Own Botnet and GIGI WIFI exploits
New tags: Build Your Own Botnet web UI RCE (CVE-2024-45256), CVE-2024-46506, GIGI WIFI RFI
New tags for QNAP NAS and Rudder Server SQL injection RCE
New tags: QNAP NAS (CVE-2022-23121) and Rudder Server SQL injection RCE (CVE-2023-30625)
Feb 10, 2025
New tag for Citrix ADC/Gateway directory traversal RCE
New tag: Citrix ADC/Gateway directory traversal RCE (CVE-2024-7097)
Feb 4, 2025
RIOT Cloudflare entry corrected
RIOT dataset: Cloudflare entry corrected
Jan 31, 2025
Built a ground-up data pipeline to replace the legacy ingestion path, with the first three data transformers (SSH, TLS, HTTP) deployed to production. New streaming and search clients, cloud infrastructure, and integration test coverage. The foundation enabling faster queries, extended historical lookback, and the sensor migration program.
New tag for SonicWall SSL-VPN auth bypass
New tag: SonicWall SSL-VPN auth bypass (CVE-2024-53704)
New tag for XML External Entity HTTP attacks
New tag: XML External Entity (XXE) HTTP attack pattern
Six CVEs added for the TOTOLINK router family
New tag: TOTOLINK router family — 6 CVEs covered
Jan 30, 2025
Press ⌘K (macOS) to open the search bar and instantly look up IPs, CVEs, or tags. Arrow-key navigation and dynamic filter suggestions make it easier to construct queries in real time, and analysts can now bulk search IPs directly from the search bar — no more switching to the Analysis tab. Cleaner access gating and file upload support round out the overhaul.
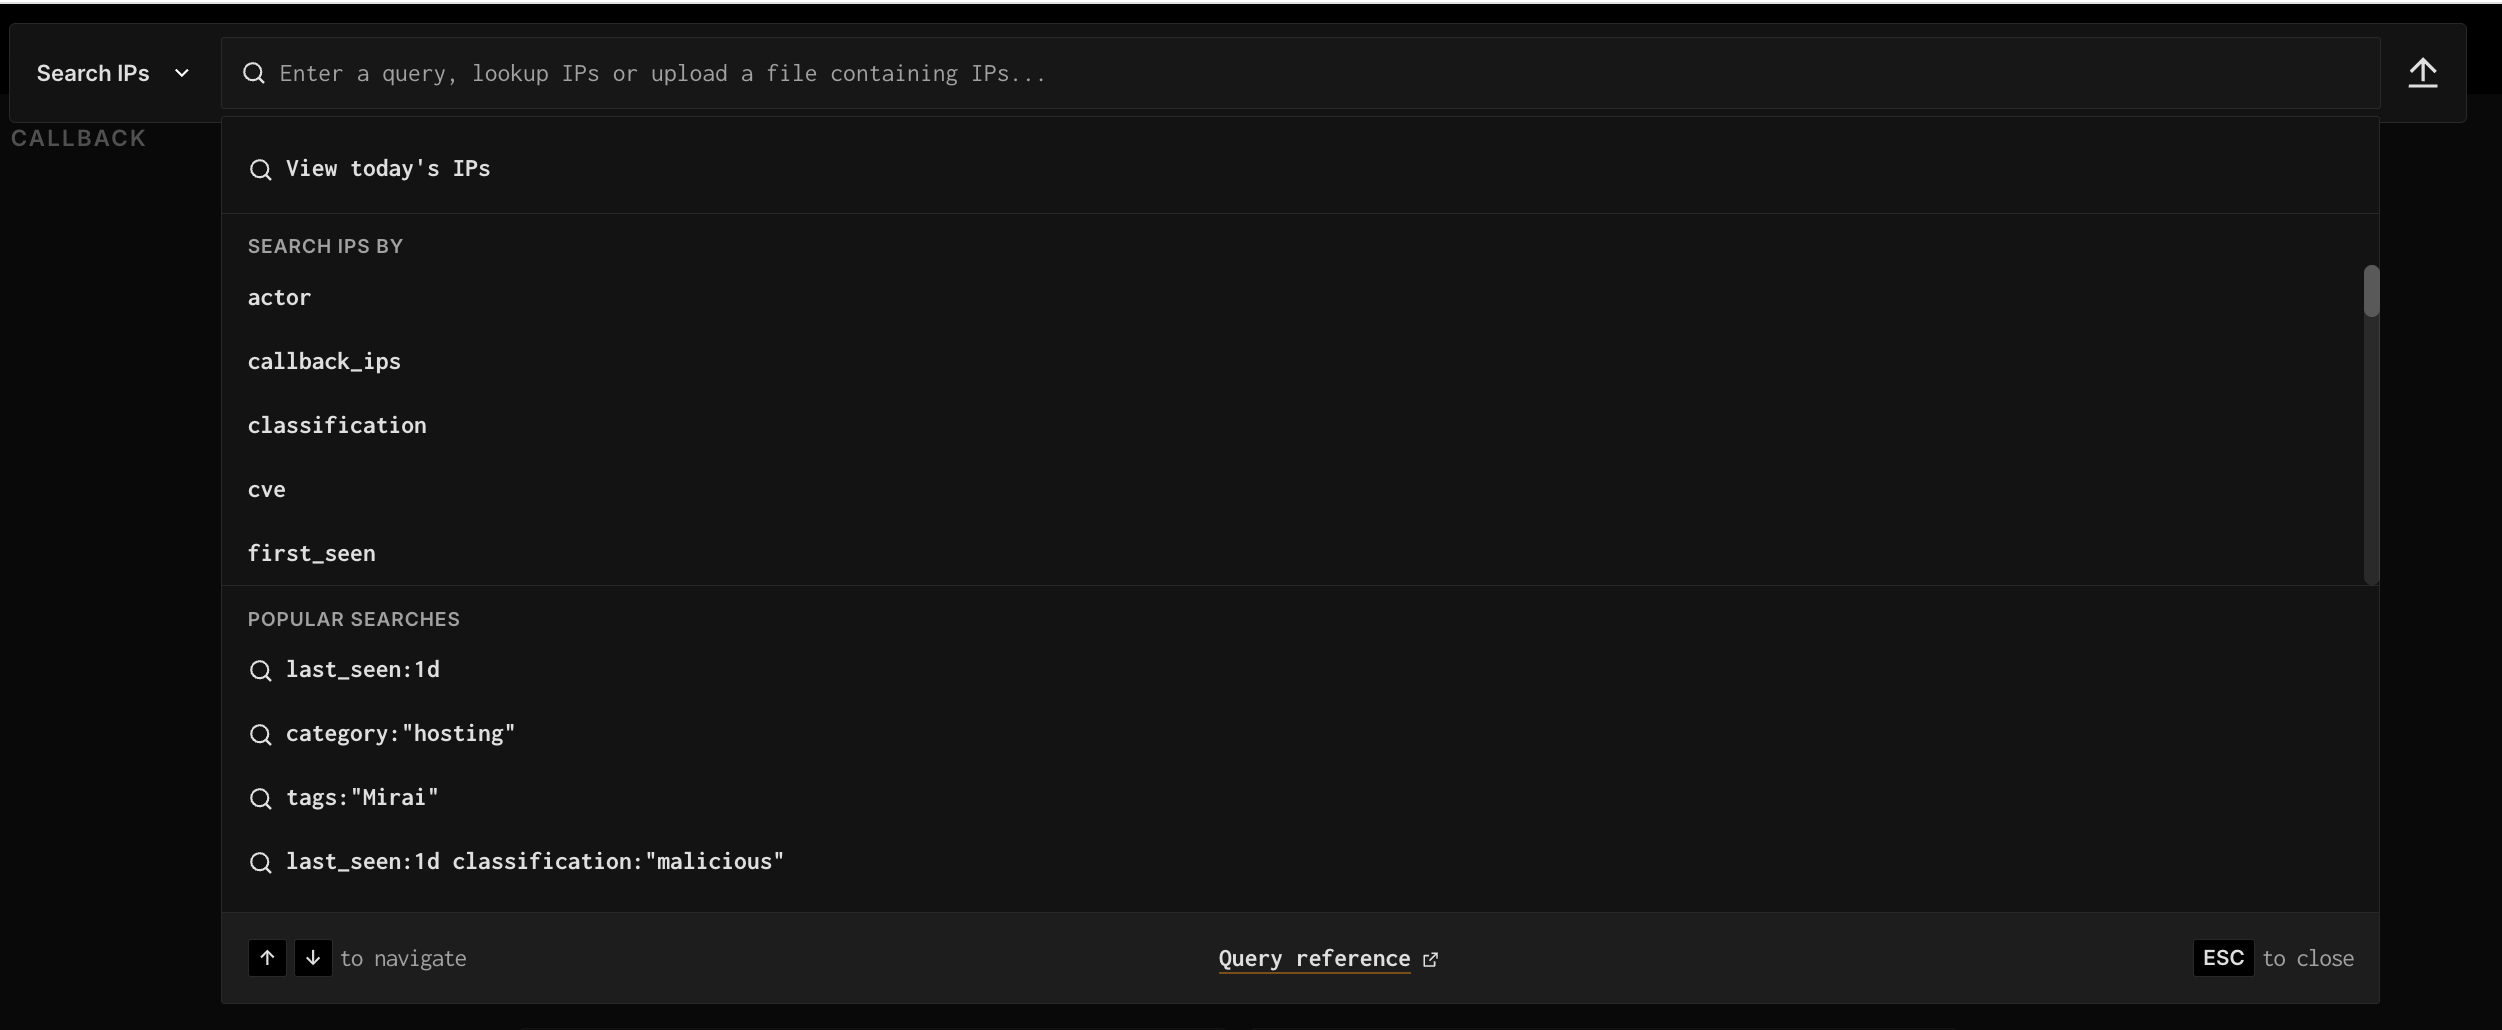
New tag for Microsoft SCCM SQL injection
New tag: Microsoft SCCM SQL injection
New tag for WordPress Contact Form 7 XSS
New tag: WordPress Contact Form 7 XSS (widely-installed plugin)
Jan 29, 2025
Launched plan-gated access to extended historical data across GNQL queries, analysis views, tag activity charts, the IP timeline, and query alerts. Users who reach their tier limit see contextual upgrade prompts — a direct monetization touchpoint tied to data depth.
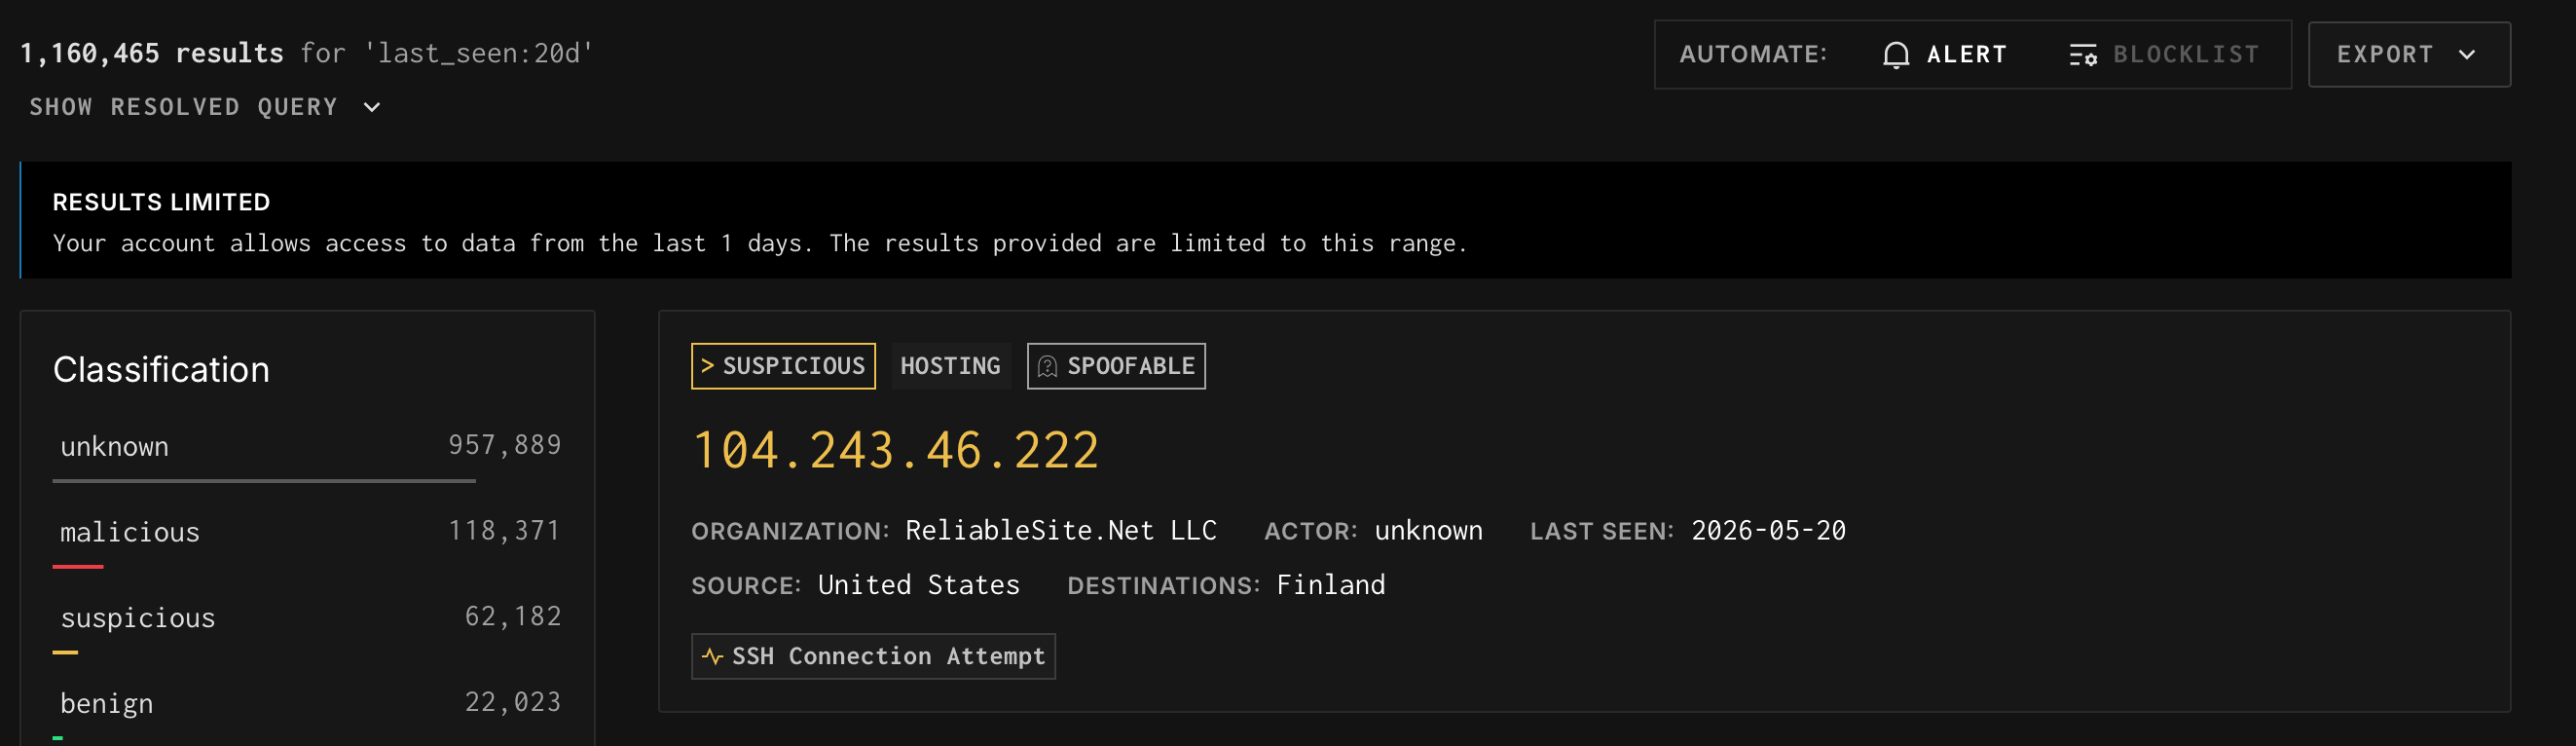
New tag for SimpleHelp remote-support path traversal (CVE-2024-57727)
New tag: SimpleHelp remote-support path traversal (CVE-2024-57727)
Same-day tag for Palo Alto PAN-OS command injection (CVE-2025-0107)
Same-day tag: Palo Alto PAN-OS command injection (CVE-2025-0107)
Jan 28, 2025
GreyNoise Alerts notify analysts whenever a query they care about matches new activity in the internet scanner dataset. Search by IP, CVE, tag, ASN, port, or any GNQL field — and get notified hourly, daily, or weekly via email or webhook. This release replaced the legacy alert system end-to-end with a new backend pipeline, a redesigned creation flow, and query alerts tied to historic data reach.
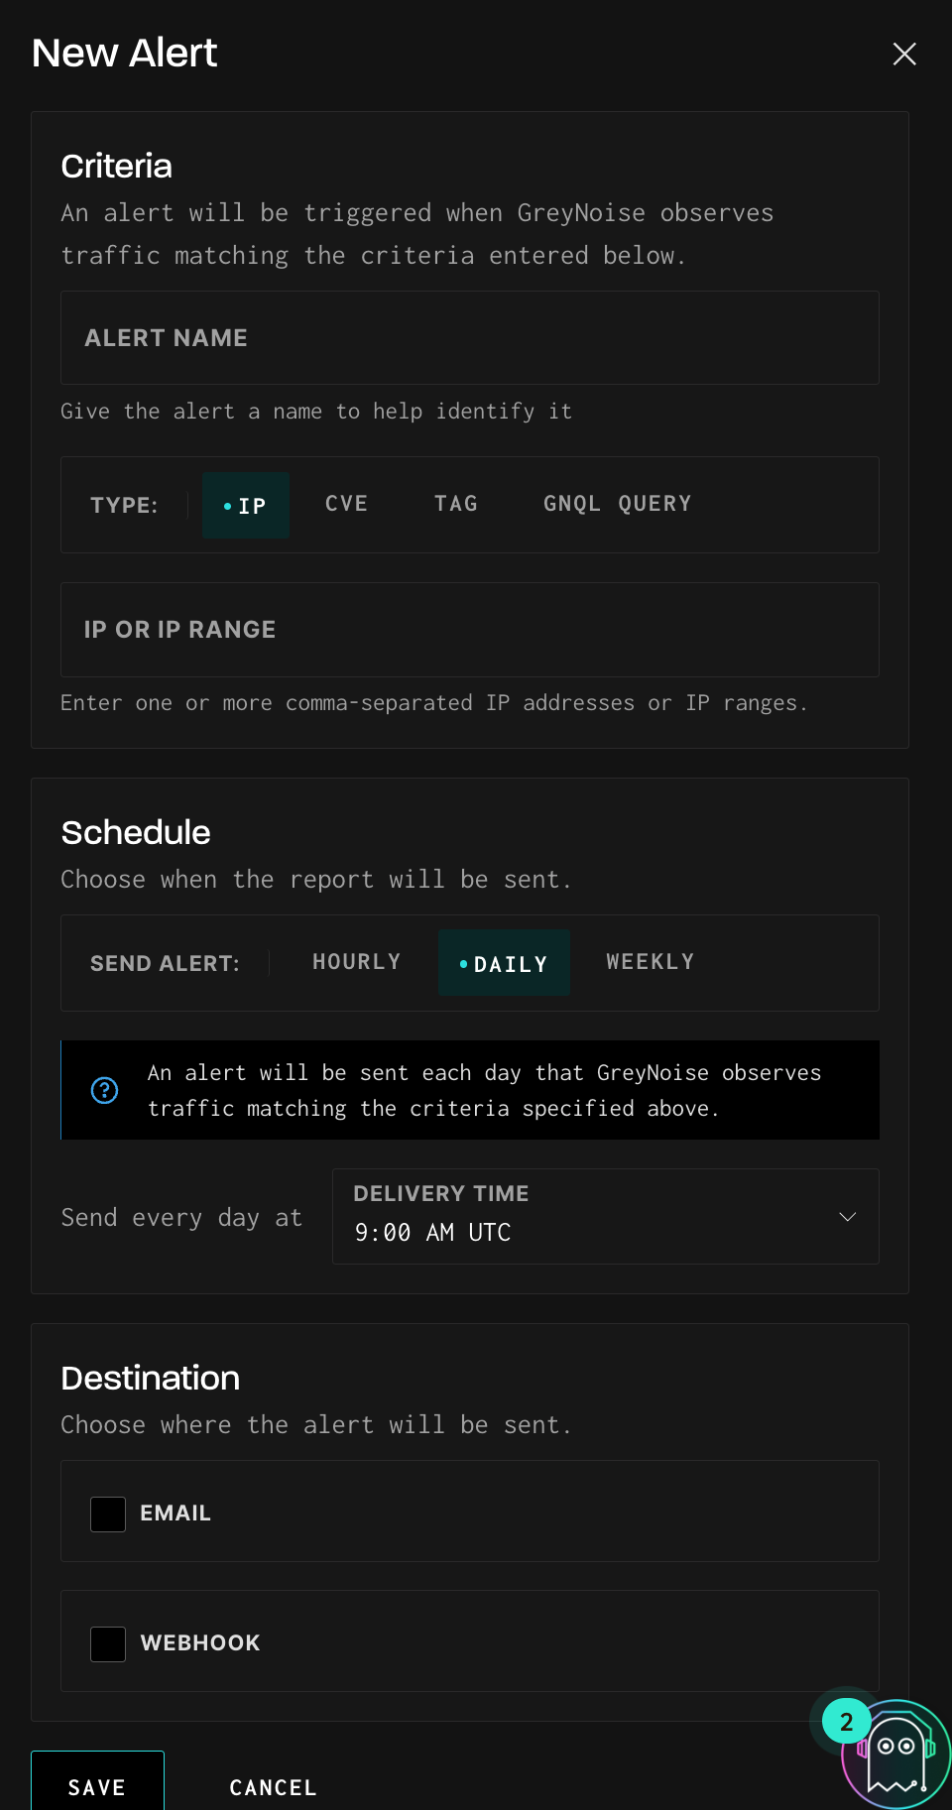
New tag for Jenkins CI/CD unsafe deserialization
New tag: Jenkins CI/CD unsafe deserialization
New tag for Linksys E-Series TheMoon botnet activity
New tag: Linksys E-Series TheMoon botnet activity
New tag for sitemap crawling activity
Sitemap crawling tag
Jan 24, 2025
New tag for Zyxel CPE telnet command injection (CVE-2024-40891)
New tag: Zyxel CPE telnet command injection (CVE-2024-40891)
New tags covering the Ivanti EPM and Avalanche vulnerability cluster
New tag: Ivanti EPM + Avalanche vulnerability cluster (5 CVEs)
Jan 22, 2025
The IP Timeline gives analysts a day-by-day view of up to 90 days of observed behavior for any IP — classifications, tags, ports scanned, HTTP paths, TLS/SSH fingerprints, and more. Rebuilt as a dedicated, fully-tested component with a new backing endpoint, it lets security teams correlate when an IP appeared in their environment, understand what schedule it operates on, and spot ownership or behavioral changes over time.
Jan 21, 2025
Smoother Universal Signup redirect in the Visualizer
Visualizer — improved Universal Signup redirect
Jan 17, 2025
Same-week tag for Ivanti Connect Secure RCE (CVE-2025-0282)
Same-week tag: Ivanti Connect Secure RCE (CVE-2025-0282, CISA KEV)
Jan 15, 2025
New tag for DigiEver DVR NTP RCE
DigiEver DVR NTP RCE tag
Jan 9, 2025
New tag for NUUO NVRmini missing authentication (CVE-2022-23227)
New tag: NUUO NVRmini missing-auth (CVE-2022-23227, CISA KEV)
New tag for Oracle WebLogic RCE (CVE-2020-2883)
New tag: Oracle WebLogic RCE (CVE-2020-2883)
Search queries now normalize smart quotes automatically
Search queries now normalize smart quotes automatically
Workspace invite emails are now case-insensitive
Workspace invite emails are now case-insensitive
Jan 7, 2025
New benign-actor tag for Nokia Deepfield
Nokia Deepfield benign-actor tag
Jan 6, 2025
Expanded sensor footprint with new regional coverage
Expanded sensor footprint with new regional coverage
Sensor honeypots renamed to Profiles across the product
Sensor honeypots renamed to 'Profiles' across the product